
India Cybersecurity Market Analysis by Mordor Intelligence
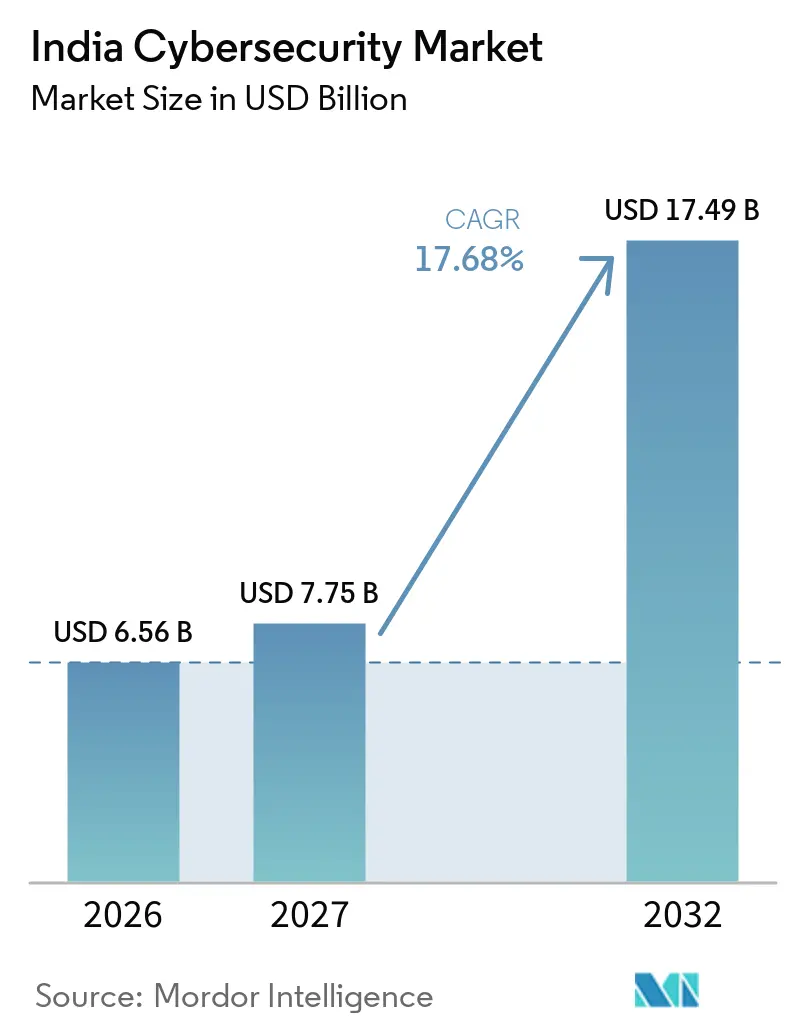
The India cybersecurity market size is expected to increase from USD 6.56 billion in 2026 to USD 7.75 billion in 2027 and reach USD 17.49 billion by 2032, growing at a CAGR of 17.68% over 2027-2032.
Digital expansion in India connects payment fraud prevention with stronger protection of personal data and machine communications. Compliance obligations reinforce that need by linking incident response with the ability to retain and retrieve usable operating evidence. Suppliers can address these needs by combining security products with monitoring and response while assigning clear responsibility for operating controls. Payment platforms and connected-device networks give these needs a concrete form, but analyst availability and small-business affordability can limit deployment. Suppliers able to add integration and incident-handling capacity to their platforms are better placed to convert demand where buyers lack staff to operate controls.
Key Report Takeaways
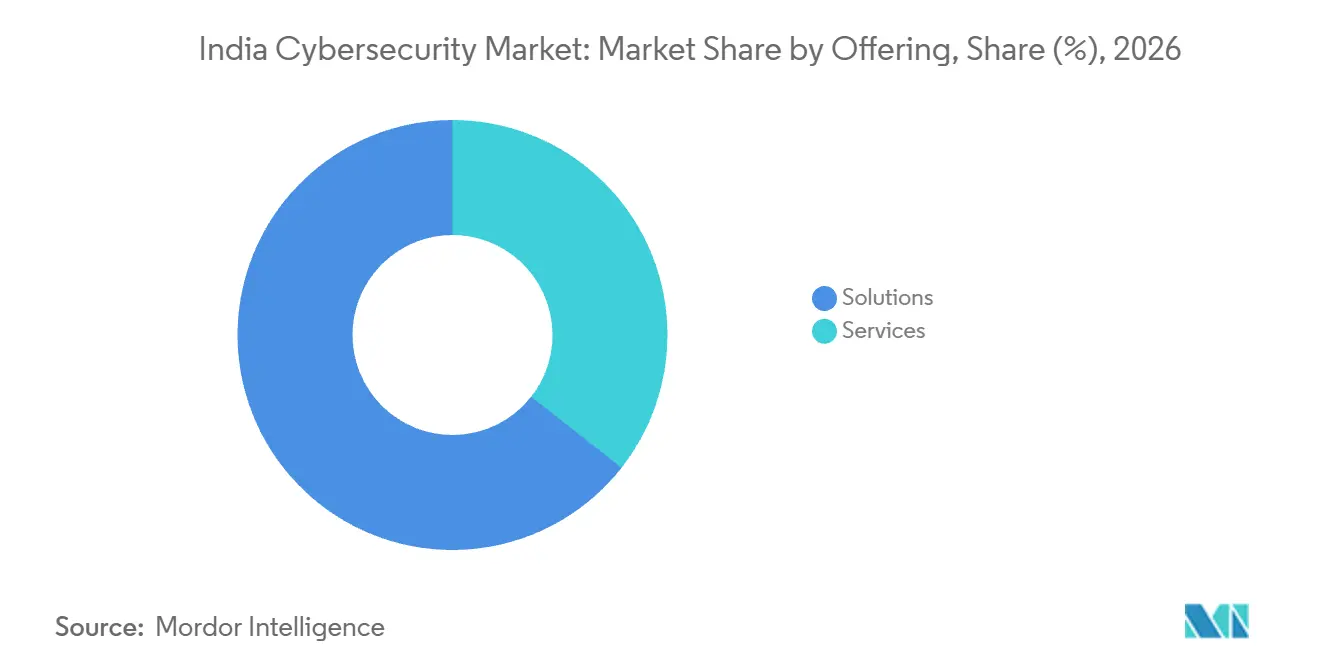
- By offering, solutions held a 64.41% India cybersecurity market share in 2026, while services are forecast to grow fastest at a CAGR of 18.21% over 2027-2032.
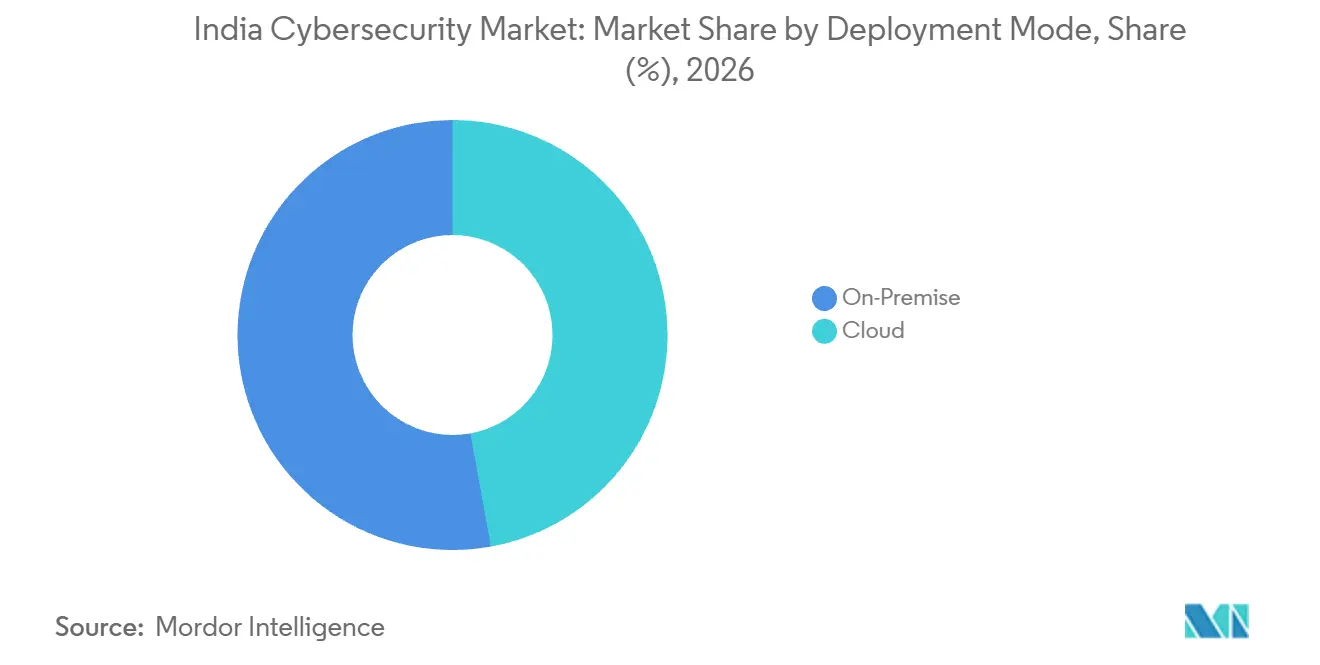
- Deployment mode was led by on-premise systems, with a 52.86% share of the India cybersecurity market size in 2026, and cloud is forecast to grow fastest at a CAGR of 21.45% over 2027-2032.
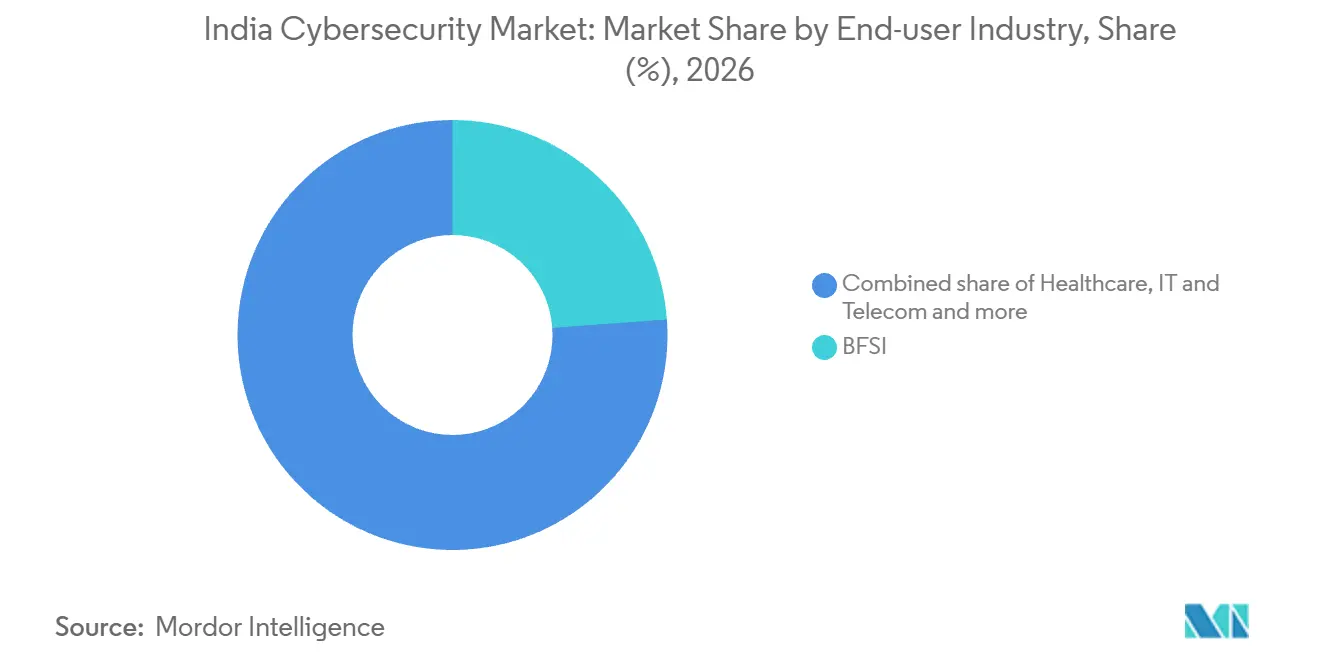
- Among end-user industries, BFSI accounted for 23.85% of the market in 2026, while healthcare is forecast to expand fastest at a CAGR of 18.44% over 2027-2032.
- Across enterprise sizes, large enterprises held 69.3% of the market in 2026, and small and medium enterprises are forecast to grow fastest at a CAGR of 19.32% over 2027-2032.
Note: Market numbers in this report are based on Mordor Intelligence's proprietary estimation framework, which combines nine months of actuals with Q4 projections for base year 2026.
Market Trends and Insights
Drivers Impact Analysis of India Cybersecurity Market*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Digital India and Enterprise Modernization Mandating Robust Cybersecurity Controls | +6.2% | Nationwide | Medium term (2-4 years) |
| Surge in UPI and Real-Time Payments Driving Identity/Fraud Protection Demand | +5.4% | Nationwide | Short term (≤ 2 years) |
| Government DPDP Act and CERT-In Compliance Deadlines Accelerating Security Spend | +4.7% | Nationwide | Short term (≤ 2 years) |
| 5G and IoT Roll-outs Exposing New Attack Surface in Telecom and Smart Manufacturing | +3.9% | Nationwide | Medium term (2-4 years) |
| Rise of Ransomware-as-a-Service Targeting Public Sector and Critical Infrastructure | +2.7% | Nationwide | Short term (≤ 2 years) |
| Venture Capital and Government Grants Fueling Indian Cybersecurity Start-up Ecosystem | +1.8% | Nationwide | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Digital India and Enterprise Modernization Mandating Robust Cybersecurity Controls
Digital expansion makes assurance of online operations an enterprise requirement as more services depend on connected infrastructure. TRAI reported 1.11 billion internet subscribers in India at the end of June 2026, up 1.96% from the previous quarter. In 2025, the Indian Computer Emergency Response Team (CERT-In) had empaneled 231 certified security audit organizations, and most audits were carried out in banking and financial institutions, power and energy, and transport. This assurance activity provides a practical link between wider digital reach and the identification of control weaknesses in important operating systems across the India cybersecurity market. Where an audit identifies weaknesses, remediation creates work beyond the assessment itself, linking modernization to implementation revenue and supporting India cybersecurity market growth.
Surge in UPI and Real-Time Payments Driving Identity/Fraud Protection Demand
Payment providers need fraud controls that can operate within the transaction decision rather than depend entirely on later investigation. India’s Unified Payments Interface (UPI) processed 24.51 billion transactions in August 2026. On June 30, 2025, the Reserve Bank of India (RBI) directed scheduled commercial, small finance, payments and cooperative banks to integrate the Department of Telecommunications’ Financial Fraud Risk Indicator into their systems. That direction gives banks a concrete integration task alongside the operating scale of real-time payments, reflecting India cybersecurity market trends toward proactive fraud prevention. Bank-side integration is the step that can make telecommunications intelligence actionable before a payment decision.
Government DPDP Act and CERT-In Compliance Deadlines Accelerating Security Spend
Compliance creates demand for connected detection, recordkeeping and escalation capabilities that can meet an enforceable reporting deadline. Covered service providers, intermediaries, data centers, body corporates and government organizations must report Annexure I cyber incidents to CERT-In within 6 hours of noticing them or being informed.[1] They must securely retain all information and communication technology (ICT) system logs in India for a rolling 180 days and provide them with incident reports or when CERT-In directs. These obligations connect response speed with the ability to retrieve usable evidence. The Ministry of Electronics and Information Technology (MeitY)’s Digital Personal Data Protection Rules, 2025, scheduled Rules 3, 5 to 16, 22 and 23 to commence 18 months after publication on November 13, 2025. Standing CERT-In duties and scheduled DPDP commencement create separate operating and preparation needs, making implementation sequencing part of the compliance purchase.
5G and IoT Roll-outs Exposing New Attack Surface in Telecom and Smart Manufacturing
Machine connectivity shifts part of the security requirement from human account access to the management of connected endpoints. In June 2026, India had 563,000 installed 5G base transceiver stations, and 5G services were available in 99.9% of its districts. Cellular machine-to-machine (M2M) connections increased from 137.7 million in July 2026 to 140.5 million in August 2026. For operators securing machine communications, this expanding connection base increases the importance of distinguishing authorized devices from unwanted access. Controls sized only around human accounts could therefore understate the workload that device-level authorization adds.
Restraints Impact Analysis of India Cybersecurity Market*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Shortage of Certified SOC Analysts | -2.8% | Nationwide | Medium term (2-4 years) |
| Price Sensitivity among MSMEs Limiting Adoption of Enterprise-Grade Solutions | -2.1% | Nationwide | Medium term (2-4 years) |
| Fragmented Regulation on Cross-border Data Flows Creating Procurement Delays | -1.2% | Nationwide | Short term (≤ 2 years) |
| Legacy infrastructure complexity | -0.9% | Nationwide | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Shortage of Certified SOC Analysts
Experienced security staffing can limit usable operating capacity even when a buyer has acquired the necessary technology. The Data Security Council of India (DSCI) and SANS 2025-2026 survey found that 73% of surveyed Indian enterprises and 68% of surveyed cybersecurity providers reported limited availability of skilled cybersecurity candidates. ISC2’s 2025 study of 524 cybersecurity professionals in India found that 48% reported staff shortages, down from 59% in 2024. ETtech reported in November 2025 that entry-level security operations center (SOC) analyst roles were easier to staff than positions requiring scarce hands-on, cross-functional skills. Across the India cybersecurity industry, complex engagements can require more costly recruitment or longer staffing lead times when junior capacity cannot replace the required practical expertise.
Price Sensitivity among MSMEs Limiting Adoption of Enterprise-Grade Solutions
Affordability can limit the protection that small and medium enterprises (SMEs) can implement, even when their operations face meaningful cyber exposure. In commentary published in January 2025, Ruchin Kumar, Futurex’s vice president for South Asia, wrote in a personal capacity about Indian fintech SMEs with fewer than 200 employees. He linked their heightened cyber risk to limited financial resources and insufficient cybersecurity skills and technology. Financial capacity and implementation resources jointly determine the protection those fintech buyers can put to work. In Tata Tele Business Services and CyberMedia Research’s 2026 study of SMEs across major Indian cities, respondents cited budget constraints (23%), expertise gaps (45%) and integration complexity (43%) as obstacles to effective cybersecurity implementation. The commercial ceiling for an enterprise-grade deployment therefore includes delivery effort as well as the product outlay, which can keep broader coverage beyond those firms’ affordable implementation range.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
India Cybersecurity Market Segment Analysis
By Offering:
Solutions Lead While Services Extend Operating ResponsibilitySolutions accounted for a 64.41% share of the India cybersecurity market size in 2026. Gartner forecast that Indian end users would spend USD 1.56 billion on security software in 2026, which it described as the country’s largest information-security segment. In 2025, DSCI reported domestic demand generated more than 45% of India’s cybersecurity product-industry revenue, with BFSI, IT-ITeS and government sectors accounting for over one-third of demand. With BFSI, IT-ITeS and government accounting for over one-third of the domestic demand DSCI measured for product companies, institutional buyers in 3 sectors anchor product demand behind the Solutions lead.
Services are forecast to form the fastest-growing segment, with a CAGR of 18.21% over 2027-2032. In October 2025, Airtel Business secured a multi-year contract from the Indian Railway Security Operations Centre to deliver cybersecurity services for Indian Railways’ digital operations. The contract shows that the service buyer base extends into transport infrastructure, where protection concerns an operating network’s digital backbone. A multi-year commitment makes continuity of the delivered function part of the commercial proposition across the contract term.

By Deployment Mode:
On-Premise Scale Coexists With Cloud AdoptionOn-premise deployment represented a 52.86% India cybersecurity market share in 2026. In a survey conducted from May to July 2025, 70% of more than 350 chief information officers and technology leaders at India’s top enterprises reported on-premise security solutions in the in-house staff model. That operating combination places deployment choices alongside the organization’s use of its own security team, linking local implementation with internal delivery capacity. An in-house operating model makes local team capacity a limit on usable product scope, even when deployment remains on-premise.
Cloud is the fastest-growing segment, with a forecast CAGR of 21.45% over 2027-2032. In January 2025, Orca Security reported 100% year-over-year customer growth in India for its cloud security platform.[2] Orca also reported 500% customer growth since opening its data center in India in 2023 and an expanded partner base. The company linked its expansion to AI-driven demand for a comprehensive, integrated cloud security platform. Local infrastructure and wider partner coverage can therefore support cloud adoption together, giving Indian buyers more routes to an integrated platform.
By End-user Industry:
Banking Programs Contrast With Healthcare AssuranceBanking, financial services and insurance (BFSI) was the largest segment, accounting for 23.85% of the market in 2026. State Bank of India awarded PricewaterhouseCoopers Services LLP a 7-year contract on July 15, 2025, to manage its on-premises Global Cyber Security Operations Centre. The contract paired an on-premises security operation with an external management provider, separating where the function resides from who delivers the work. Retaining an on-premises center need not reserve its management for the bank’s own staff, making operating responsibility a separately contestable contract.
Healthcare is the fastest-growing segment, with a forecast CAGR of 18.44% over 2027-2032. The 2025 EY and CII HealthTech survey found that 90% of surveyed Indian healthcare providers reported third-party audits to identify data-protection and security gaps. AIIMS Bhubaneswar listed a bid to procure a cybersecurity audit for its IT Cell on July 28, 2026, with bids due August 21, 2026. The combination of reported adoption and a named procurement solicitation connects healthcare demand to external assessment of control gaps. A discrete audit mandate can separate the purchase of assurance from corrective technology, leaving remediation as a subsequent decision for the healthcare buyer.
By End-user Enterprise Size:
Group Programs and Smaller Delivery PackagesLarge enterprises were the largest segment, accounting for 69.3% of the market in 2026. In FY 2025-26, Mahindra & Mahindra cited enhanced cybersecurity and fraud-prevention systems and periodic risk assessments among its group-wide risk-management measures. These measures place cybersecurity within a group control structure, linking technical protection with assessment and remediation responsibilities. For an enterprise organized across a group, the delivery problem is maintaining a consistent control approach while identifying where corrective work is needed. Group-wide oversight favors capabilities that connect technical findings with corrective action, since controls and periodic assessment serve the same governance framework.
SMEs are forecast to be the fastest-growing segment, with a CAGR of 19.32% over 2027-2032. In a 2026 survey by Tata Tele Business Services and CyberMedia Research across 8 Indian cities, 84% of surveyed SMEs planned to increase cybersecurity investments over the next 12 to 24 months. Packaged controls and operating work could give those prospective investments a defined scope around a specific business application. A provider can reuse a common delivery process across these engagements while defining access and incident responsibilities for each customer. That model makes the boundary of service coverage important, since responsibilities outside the package still need an owner.
Geography Analysis
Bengaluru and Pune illustrate how providers have organized announced cybersecurity capacity around dedicated facilities for enterprise service delivery. Cognizant announced the launch of a Bengaluru Cyber Defense Center on December 15, 2025, designed to deliver managed security, engineering and transformation services to global clients. Zensar Technologies announced the inauguration of its Pune ZenSOC on June 11, 2025, to provide cybersecurity protection to clients. Cognizant described the Bengaluru center as its largest facility in its worldwide Cyber Defense Center network, designed for global clients, so its location need not identify where purchasing clients are based.
On June 18, 2025, Telangana’s chief minister inaugurated Google’s Safety Engineering Center near Hitech City in Hyderabad, which the state described as Google’s first GSEC in the Asia-Pacific region.[3] The Telangana government virtually launched security operations and cyber fusion centers at its Cyber Security Conclave 2025 in Hyderabad. In a December 2025 vacancy notice, Rajasthan’s Department of Information Technology & Communication described the Jaipur-based Rajasthan State Computer Security Incident Response Team as being established. Its proposed remit covered state departments, critical infrastructure and strategically important private organizations. Because the proposed remit spans state departments, critical infrastructure and strategically important private organizations, the team’s service area would extend beyond Jaipur even though it is based there.
Workforce development and community awareness connect other locations to the security ecosystem through different delivery routes. DSCI established an Advanced Cyber Skill Centre in Kandivali, Mumbai, which Union Minister Piyush Goyal inaugurated on July 19, 2025, with courses planned in ethical hacking, security operations, threat hunting and incident response. In April 2026, MeitY, C-DAC Hyderabad and Reliance Foundation announced e-SafeHER to support cybersecurity awareness training for rural women. Initial delivery was to begin in Madhya Pradesh and Odisha through community channels including Self-Help Groups, with C-DAC providing content and Reliance Foundation supporting dissemination. For training providers, the geographic distinction changes the distribution model, with professional instruction delivered through a dedicated center and awareness content carried by rural community groups.
Regulatory Framework and Outlook
Selected jurisdictions are compared from the perspective of cybersecurity service suppliers handling personal data and serving government organizations. The national framework and Assam’s additional state-government policy create different compliance layers, with the state duties focused on covered state-owned information. Scheduled Digital Personal Data Protection (DPDP) safeguards add a national compliance layer when suppliers act as data fiduciaries or process data under applicable contracts.
Regulatory Table of India Cybersecurity Market
| Decision factor | India | Assam |
|---|---|---|
| Primary authority | CERT-In for incident response; MeitY for DPDP rulemaking | Information Technology Department under Apex Committee guidance |
| Key instruments or direction | CERT-In directions; scheduled DPDP Rules, 2025 safeguards | Cyber Security Policy 2020 for covered state government information and ICT assets |
| Commercial effect | Incident-response baseline and scheduled safeguards for covered personal-data work | Minimum security requirements for covered state-owned information |
| Current policy attractiveness | Medium | Medium |
| Future direction of policy attractiveness | Hardening | No change |
| Source: Mordor Intelligence | ||
India’s Medium rating reflects defined national response obligations, and Hardening reflects the scheduled 2027 commencement of DPDP safeguards. That transition adds direct duties for suppliers acting as data fiduciaries and contractual requirements where they process data under applicable agreements. Assam’s Medium rating reflects its operative policy for covered state-government information alongside national requirements, while No change reflects the absence of a scheduled state-policy transition. MeitY’s May 2026 workshop called for empowered state chief information security officers and operational security centers as a policy direction, so implementation opportunities depend on state adoption rather than an enacted rule.
Value Chain Stages
The value chain compares how risk definition, security products and continuing operations create different sources of supplier earnings. KPMG in India advises on governance, cloud assurance, privacy and resilience, placing risk assessment upstream of technical implementation. Tata Communications provides managed monitoring and response, making continuing operations a distinct delivery stage. These roles make the handoffs between defining a control requirement, supplying protection and responding to incidents commercially important.
Value Chain Analysis Table of India Cybersecurity Market
| Primary activity | Key participants | Value capture | Bottleneck | Resilience response |
|---|---|---|---|---|
| Assess risks and design controls | Cybersecurity advisers such as KPMG in India | Advisory and assurance fees | Converting governance, privacy and cloud risks into a defined control scope | Assign assets, control requirements and accountable owners |
| Supply security products | Enterprise security product suppliers such as Quick Heal Technologies Ltd. through Seqrite | Product sales | Mapping protection across endpoint, access and data requirements | Test coverage against the assessed control requirements |
| Monitor and respond | Managed SOC providers such as Tata Communications, and incident-response providers such as SISA | Managed service contracts and response retainers | Allocating incident ownership between monitoring and response | Define escalation authority and response responsibilities |
| Source: Mordor Intelligence | ||||
Quick Heal’s FY 2025-26 enterprise strategy combined security products and managed services within a single-platform architecture. That architecture gives one provider the potential to supply both controls and continuing service work, changing how much of the relationship it can capture after initial product supply. Clear responsibility for incident handling then becomes a commercial boundary as well as an operational one, determining which provider performs and charges for response work.
Competitive Landscape
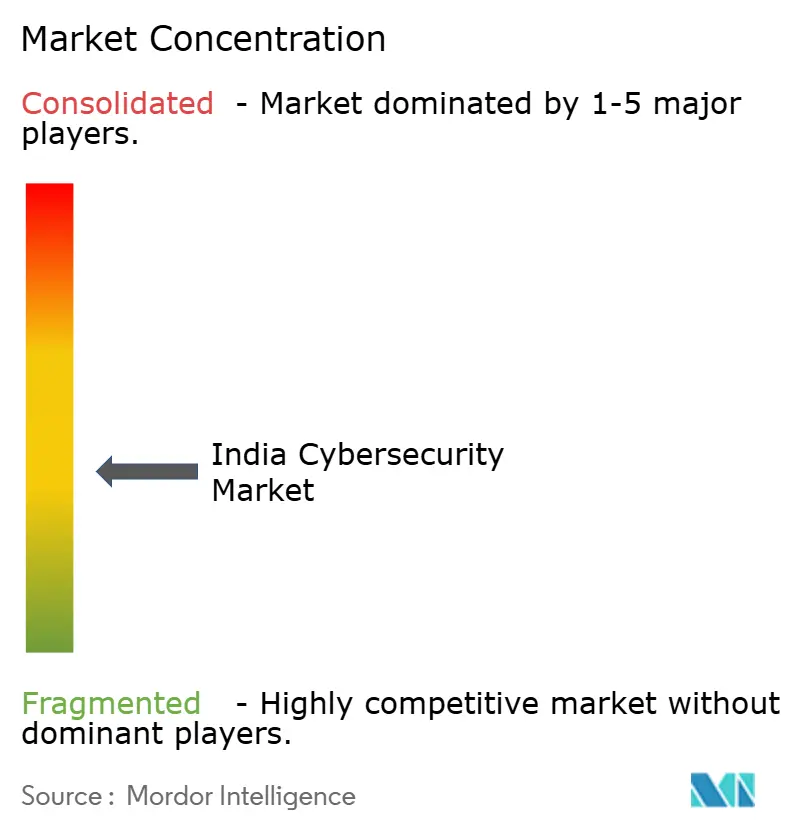
Competition is moderately fragmented, combining enterprise product vendors and managed-service providers with different responsibilities for delivering protection. Quick Heal Technologies Ltd., through Seqrite, supplies enterprise security products, and Tata Communications provides managed security operations and response. Cisco Systems, Inc. provides Multicloud Defense technology, Palo Alto Networks, Inc. supplies cybersecurity platforms and threat intelligence, and Wipro Ltd. provides managed security services. Quick Heal said its enterprise business converted a large institutional order during the quarter ended December 31, 2025. Institutional order conversion can make procurement timing consequential for a product business, whereas the managed-service proposition centers on continuing operating responsibility.
Partnerships give service providers a way to combine specialist technology with a managed operating model, making delivery capability central to differentiation. On September 15, 2025, Wipro announced an expanded CrowdStrike partnership for CyberShield MDR, powered by Falcon Next-Gen SIEM. Wipro said it would host and manage the global service from 8 cyber defense centers worldwide, placing the operating role with the service provider. An enterprise could use the announced service to shift platform operations outside its own team, making staffing responsibility part of the outsourcing decision.
Competitive direction includes protection that spans public and private cloud environments. On June 24, 2025, Tech Mahindra Ltd. announced managed services for Cisco Multicloud Defense to protect enterprise workloads across public and private clouds. That scope makes consistent policy execution a potential source of value where an enterprise uses several cloud environments. Regulatory fit for covered Indian buyers consequently depends on connecting the managed service’s escalation and record retrieval to CERT-In reporting and log-retention duties.
India Cybersecurity Industry Leaders
-
Quick Heal Technologies Ltd.
-
Tata Communications
-
Cisco Systems, Inc.
-
Palo Alto Networks, Inc.
-
Wipro Ltd.
- *Disclaimer: Major Players sorted in no particular order
India Cybersecurity Market Companies Covered in this Report
- Tata Communications
- Wipro Ltd.
- HCLTech
- Infosys Ltd.
- Tech Mahindra Ltd.
- Cisco Systems, Inc.
- Check Point Software Technologies India
- Sophos Technologies Pvt. Ltd.
- Fortinet Technologies India
- McAfee Software (India) Pvt. Ltd.
- Palo Alto Networks, Inc.
- Quick Heal Technologies Ltd.
- Zscaler India Pvt. Ltd.
- Juniper Networks India Pvt. Ltd.
- Trend Micro India Pvt. Ltd.
- IBM India Pvt. Ltd.
- CrowdStrike India Pvt. Ltd.
- Kaspersky Lab India
- Indusface Pvt. Ltd.
- Safe Security (Lucideus)
- eSec Forte Technologies
- SecurityHQ India
- Cyberops Infosec LLP
- Sequretek
- Sectrio (Subex)
- Innefu Labs
Key Opportunities for Market Participants
These opportunities compare ways for data fiduciaries to implement personal-data safeguards ahead of Rule 6’s scheduled commencement under the Digital Personal Data Protection (DPDP) Rules, 2025. The Rules published on November 13, 2025, scheduled Rule 6 to commence 18 months later and cover personal data held or controlled by data fiduciaries, including processing on their behalf. That timetable creates an implementation window in which suppliers can connect technical controls, operating evidence and processor-security assurance.
Market Opportunities Table of India Cybersecurity Market
| Opportunity | Why now | Buyer / lead segment | Recommended play | Main barrier | Likely beneficiaries |
|---|---|---|---|---|---|
| Personal-data security and access controls | Scheduled Rule 6 data-security and access safeguards | Data fiduciaries protecting personal-data systems | Map processing exposure and implement appropriate data-security and access controls | Aligning controls across fiduciary and applicable processor systems | Data-security and identity-control suppliers |
| Monitoring and recovery readiness | Scheduled Rule 6 monitoring and reasonable continuity measures, such as backups | Data fiduciaries operating personal-data systems | Connect access logs, investigation workflows and tested recovery procedures | Making records and recovery measures usable during disruption | Managed security and cyber-recovery service providers |
| Processor-security assurance | Scheduled Rule 6 contractual safeguard provisions wherever applicable | Data fiduciaries using data processors | Assess processor safeguards against applicable contractual requirements | Obtaining consistent control evidence across processing relationships | Cybersecurity assurance and advisory providers |
| Source: Mordor Intelligence | |||||
The central opening is integrated safeguard implementation that connects personal-data processing with the ability to control access and investigate compromise. Supplier value can extend across organizational boundaries when assurance verifies that processor controls match the applicable contractual safeguards. Commercial differentiation will rest on demonstrable control coverage across those processing relationships, giving assurance a role in verifying implementation.
Recent Industry Developments in India Cybersecurity Market
- Oct 2026: IBI Group agreed to resell Memcyco’s SaaS portfolio and bring its digital impersonation and account takeover protection to organizations across India, supported by local solution advisory and customer engagement.
- Oct 2026: CERT-In and Singapore’s SingCERT exchanged a cybersecurity cooperation MOU covering information exchange, coordinated incident response, technology cooperation and capacity building, with implementation to be overseen by a joint Expert Group.
- Sep 2026: QNu Labs launched its QShield 2.0 cryptographic assessment platform in Bengaluru, powering the company’s National Cryptographic Assessment & Assurance Framework.
India Cybersecurity Market Report Scope and Research Methodology
Market Definition and Coverage
The India cybersecurity market measures annual spending by organizations in India on commercially procured cybersecurity solutions and services for cyber-threat prevention, detection, and response. Values cover end-user purchases of security hardware and software and cybersecurity service fees, classified by offering, deployment mode, buyer industry, and enterprise size.
Scope exclusions: General-purpose IT infrastructure and communications equipment not primarily bought for cybersecurity outcomes, general IT services and outsourcing that are not cybersecurity services, defense cyber operations that are not commercially procured, and cybersecurity purchases by buyers outside India are excluded.
Segments Covered in This Report
- By Offering
- Solutions
- Application Security
- Cloud Security
- Data Security
- Identity and Access Management
- Infrastructure Protection
- Integrated Risk Management
- Network Security
- End-point Security
- Services
- Professional Services
- Managed Services
- Solutions
- By Deployment Mode
- Cloud
- On-Premise
- By End-user Industry
- BFSI
- Healthcare
- IT and Telecom
- Industrial and Defense
- Retail and E-commerce
- Energy and Utilities
- Manufacturing
- Others
- By End-user Enterprise Size
- Large Enterprises
- Small and Medium Enterprises (SMEs)
Data Sources, Market Sizing, and Validation
Desk Research
Public sources such as the Data Security Council of India's India Cybersecurity Domestic Report and Indian Cybersecurity Product Landscape Report provide market context, product-company indicators, buyer sectors, and historical demand signals. CERT-In's directions establish incident reporting and log-retention duties. Ministry of Electronics and Information Technology releases carried by the Press Information Bureau document audit and public-sector activity. These sources inform demand indicators and market boundaries, such as security-specific spending, compliance obligations, and commercially supplied products and services.
Company annual reports, investor presentations, procurement notices, and reputable business reporting can add evidence on security revenues, buyer contracts, deployment choices, and spending trends, with each item checked for its India relevance and security-specific content. These named sources are illustrative and not exhaustive, and further sources inform collection, validation, and clarification.
Primary Interviews and Surveys
Structured interviews and questionnaires would cover cybersecurity solution and service providers, Indian organizational buyers, channel or implementation partners, and sector specialists, with CXOs, functional security leaders, and operating managers describing spending, deployment, and purchasing practice. The findings would test secondary estimates and segment evidence, identify gaps in source coverage, and reconcile conflicting answers through follow-up questions and comparison with documented spending or procurement signals.
Distribution of primary research fieldwork respondents
| Company type | Respondent position | Region |
|---|---|---|
| Top tier: 33% | CXOs: 20% | |
| Mid tier: 42% | Functional/Unit leaders: 30% | |
| Smaller Players: 25% | Managers: 50% |
Market-Sizing & Forecasting
The model starts top down with annual Indian organizational spending on commercially procured cybersecurity solutions and services, then checks selected totals against supplier revenue roll-ups and sampled contract or channel evidence. Key inputs include security-specific budget and procurement trends, cybersecurity product and service revenue, covered incident and audit activity, digital and cloud adoption, and changes in compliance duties. Together they indicate the size and pace of buyer demand without treating incident counts as spending. Once the annual indicators are aligned to India and the defined transaction, a scenario forecast estimates market value in USD while varying these drivers and their timing. Selected spending records and supplier checks test the resulting total and segment shares. Offering, cloud or on-premise deployment, buyer industry, and enterprise-size shares are derived from published splits, financial disclosures, procurement records, and buyer evidence, with the categories reconciled to the market total. Interview feedback would check whether the variables and resulting growth paths match purchasing conditions in India, and gaps in company or buyer data would be handled through documented ranges and cross-checks rather than unsupported point precision.
Data Validation & Update Cycle
Analysts triangulate the market model against independent supplier revenue, organizational spending, procurement, and compliance activity, then investigate anomalies and material variances by tracing each input to its source and checking the year, geography, unit, and scope. A second review checks arithmetic, segment reconciliation, source quality, and forecast logic before sign-off, with re-contact triggered when a material conflict remains or a source clarification could change a key estimate. The evidence base is refreshed annually, reviewed between cycles when a material regulatory or market event changes spending conditions, and given a fresh pre-delivery review.
Mordor Intelligence's India Cybersecurity Market Size Compared Against Other Published Estimates
Cybersecurity estimates differ when security-specific purchases are combined with general IT spending or noncommercial defense activity. The study counts commercially procured security hardware, software and services bought by organizations in India, retaining a clear boundary around prevention, detection and response purchases.
Key Gap Drivers include that spending boundary and the indicators used to translate security needs into buyer demand. Security budgets, procurement records and supplier revenue are checked alongside cloud adoption and compliance developments; incident counts inform context without being treated as expenditure.
Benchmark comparison
| Source | Market Size | Gaps in Research Methodology |
|---|---|---|
| Mordor Intelligence | USD 7.75 B (2027) | |
| Government Trade Agency A | USD 5.6 B (2025) | At its 2025 base, this estimate is 27.7% below this report's 2027 value of USD 7.75 B, 2 years later. The published 2025 base precedes the report year, and the source projects continued growth in India's cybersecurity market. |
| Global Consultancy A | USD 3.3 B (2025) | At its 2025 base, this estimate is 57.4% below this report's 2027 value of USD 7.75 B, 2 years later. The source measures end-user information-security spending, a narrower category than the full cybersecurity solutions and services boundary. |
Mordor Intelligence links the baseline to identifiable security purchases and checks it against supplier and buyer evidence. This helps buyers distinguish a spending opportunity from a general measure of cyber activity.
Key Questions Answered in the Report
What is the India cybersecurity market size and growth outlook?
The market is expected to increase from USD 7.75 billion in 2027 to USD 17.49 billion by 2032, growing at a CAGR of 17.68% over 2027-2032.
What is driving demand for cybersecurity products and services in India?
UPI processed 24.51 billion transactions in India in August 2026. CERT-In’s 6-hour deadline for covered entities to report specified incidents after notice adds a compliance force.
Which offering leads cybersecurity spending in India?
Solutions held 64.41% of the market in 2026. Services are forecast to grow fastest at a CAGR of 18.21% over 2027-2032.
Which companies are major cybersecurity competitors in India?
Major competitors include Quick Heal Technologies Ltd., Tata Communications, Cisco Systems, Inc., Palo Alto Networks, Inc., and Wipro Ltd., spanning enterprise products and managed services.
What could limit the growth of cybersecurity services in India?
DSCI and SANS’s 2025-2026 survey found limited skilled-candidate availability among 73% of surveyed Indian enterprises and 68% of providers. ISC2’s 2025 India study reported staff shortages among 48% of 524 respondents, down from 59% in 2024.
How does cybersecurity activity vary geographically within India?
Telangana launched security operations and cyber fusion centers at a 2025 conclave in Hyderabad. In 2026, e-SafeHER was announced for rural women’s cybersecurity awareness training, initially in Madhya Pradesh and Odisha.