
Workload and Container Identity Security Market Size and Share
Market Overview
| Study Period | 2021 - 2032 |
|---|---|
| Market Size (2027) | USD 1.53 Billion |
| Market Size (2032) | USD 3.54 Billion |
| Growth Rate (2027 - 2032) | 18.27 % |
| Fastest Growing Market | Asia-Pacific |
| Largest Market | North America |
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image © Mordor Intelligence. Reuse requires attribution under CC BY 4.0. | |
Workload and Container Identity Security Market Analysis by Mordor Intelligence
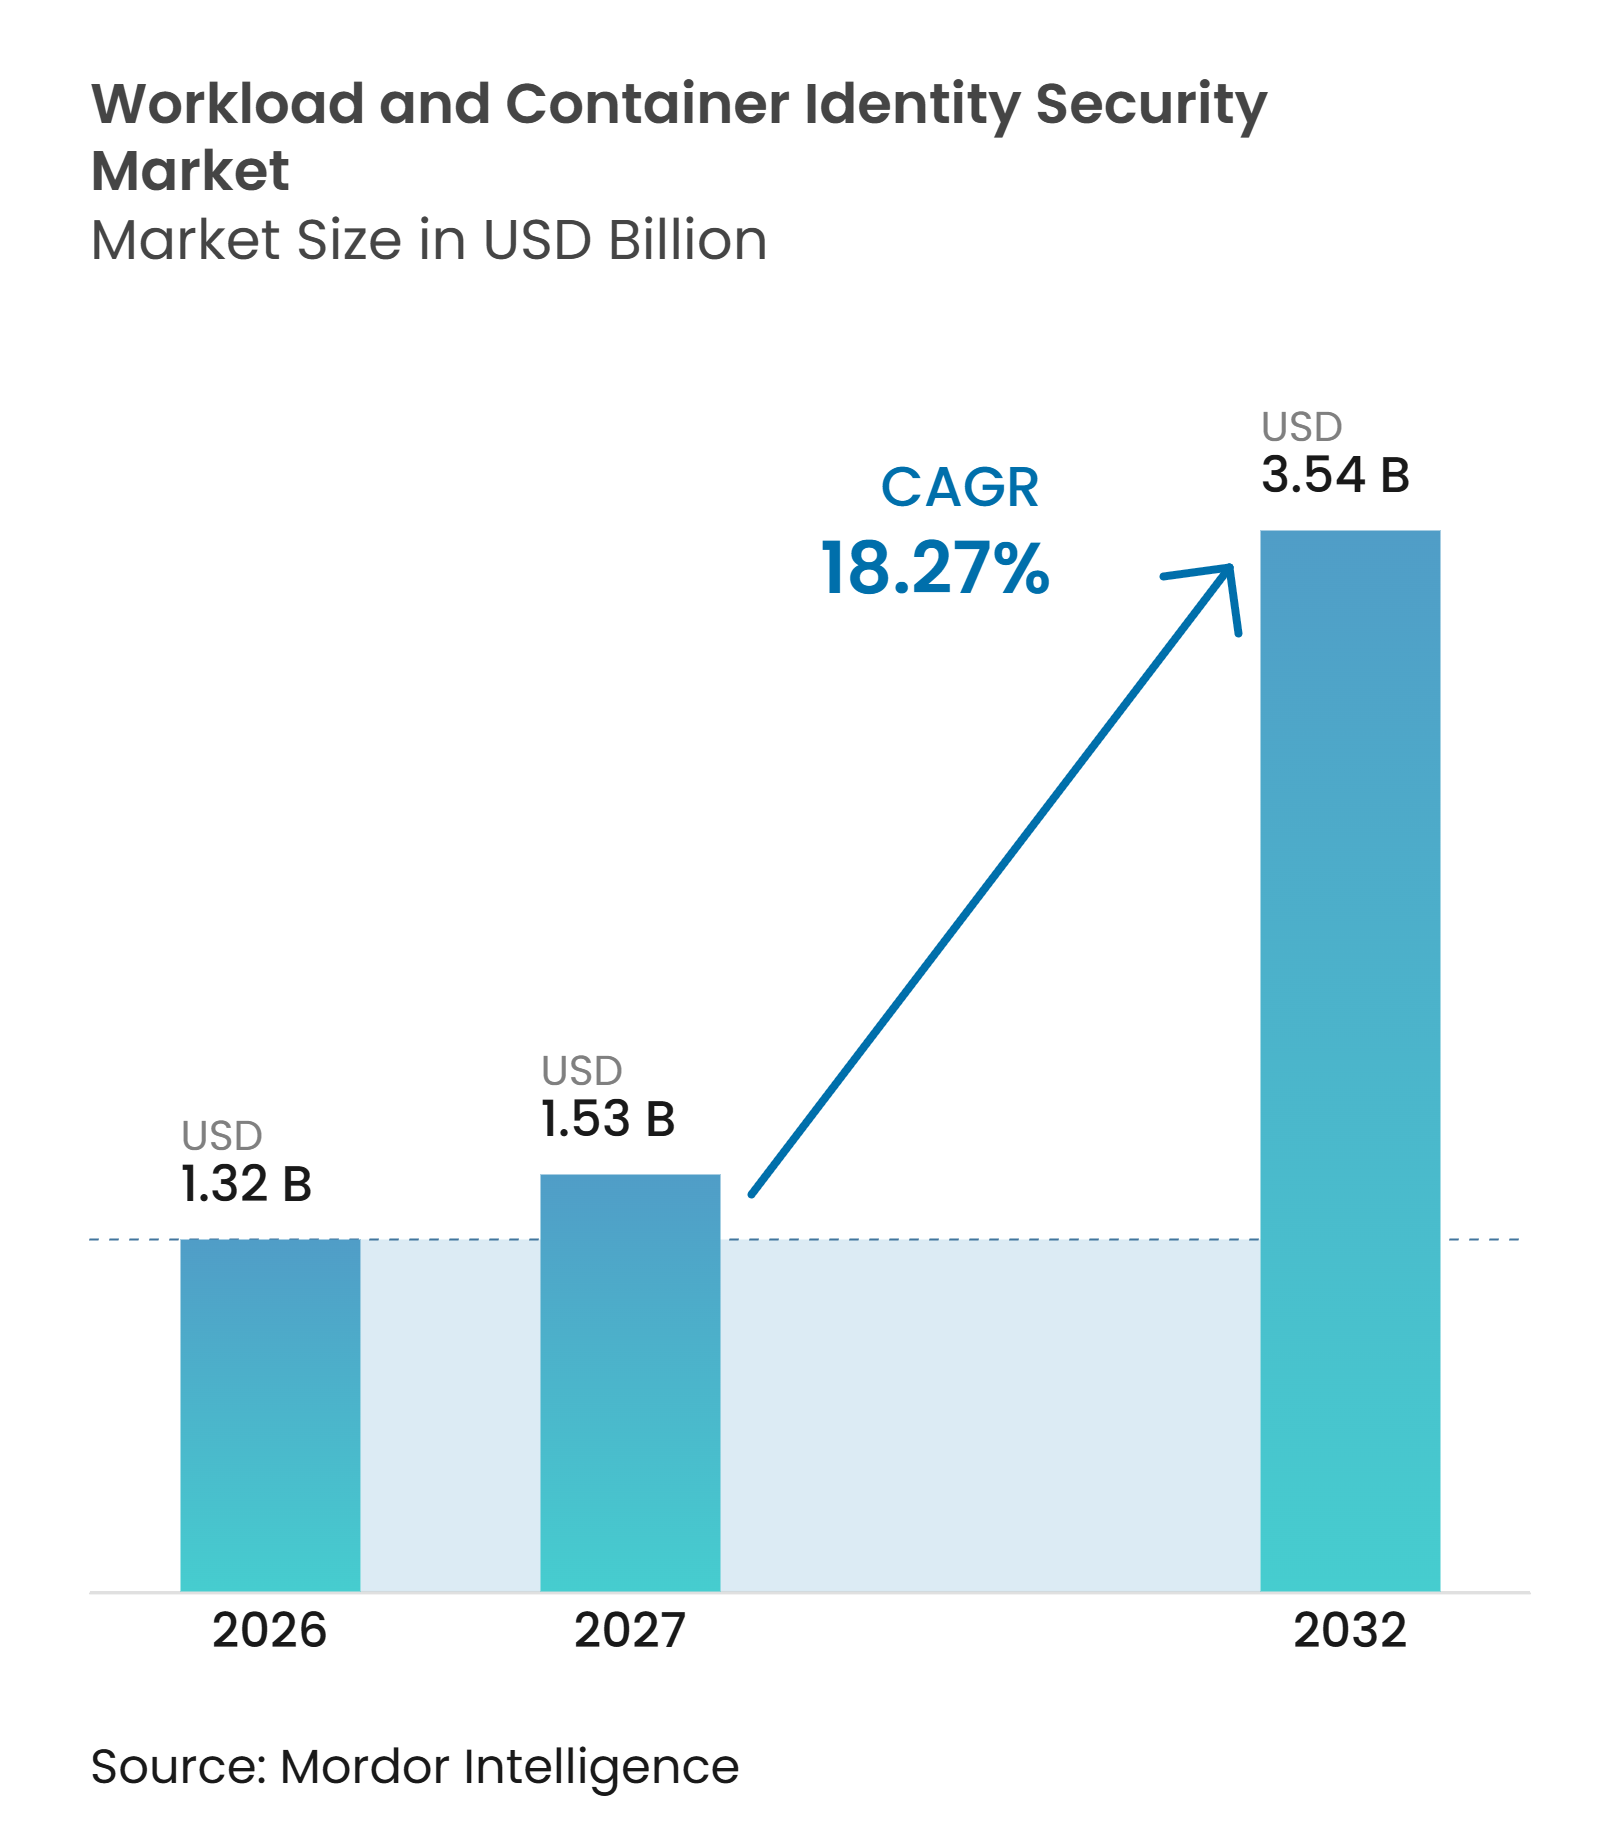
The workload and container identity security market size is projected to expand from USD 1.32 billion in 2026 and USD 1.53 billion in 2027 to USD 3.54 billion by 2032, registering a CAGR of 18.27% between 2027 to 2032. Demand is being shaped by the need to authenticate services, containers, and automated processes at a scale beyond manual credential administration, while zero trust programs are moving from policy goals into operating requirements. Regulatory attention to software supply chains and access controls is also increasing the need for traceable machine identities. Providers are responding by combining identity issuance, secrets management, policy controls, and audit functions in broader platforms that support development, deployment, monitoring, and incident response. Buyers increasingly evaluate whether platforms can cover changing applications without adding manual work for developers or security staff. The workload and container identity security market also has room to expand as organizations extend protections from cloud applications to hybrid environments and AI-driven processes, with interoperable standards and clear audit evidence strengthening supplier positions in regulated settings.
Key Report Takeaways
- By component, solutions held 73.98% of the workload and container identity security market share in 2026.
- By identity type, Workload and Container Identities are projected to expand at a 19.16% CAGR through 2032.
- By deployment mode, hybrid deployment is expected to expand at a 19.83% CAGR through 2032.
- By organization size, large enterprises accounted for 72.91% of the workload and container identity security market in 2026, while SMEs are the fastest-growing organization-size segment.
- By end-user industry, Healthcare and Life Sciences is projected to expand at a 19.09% CAGR through 2032.
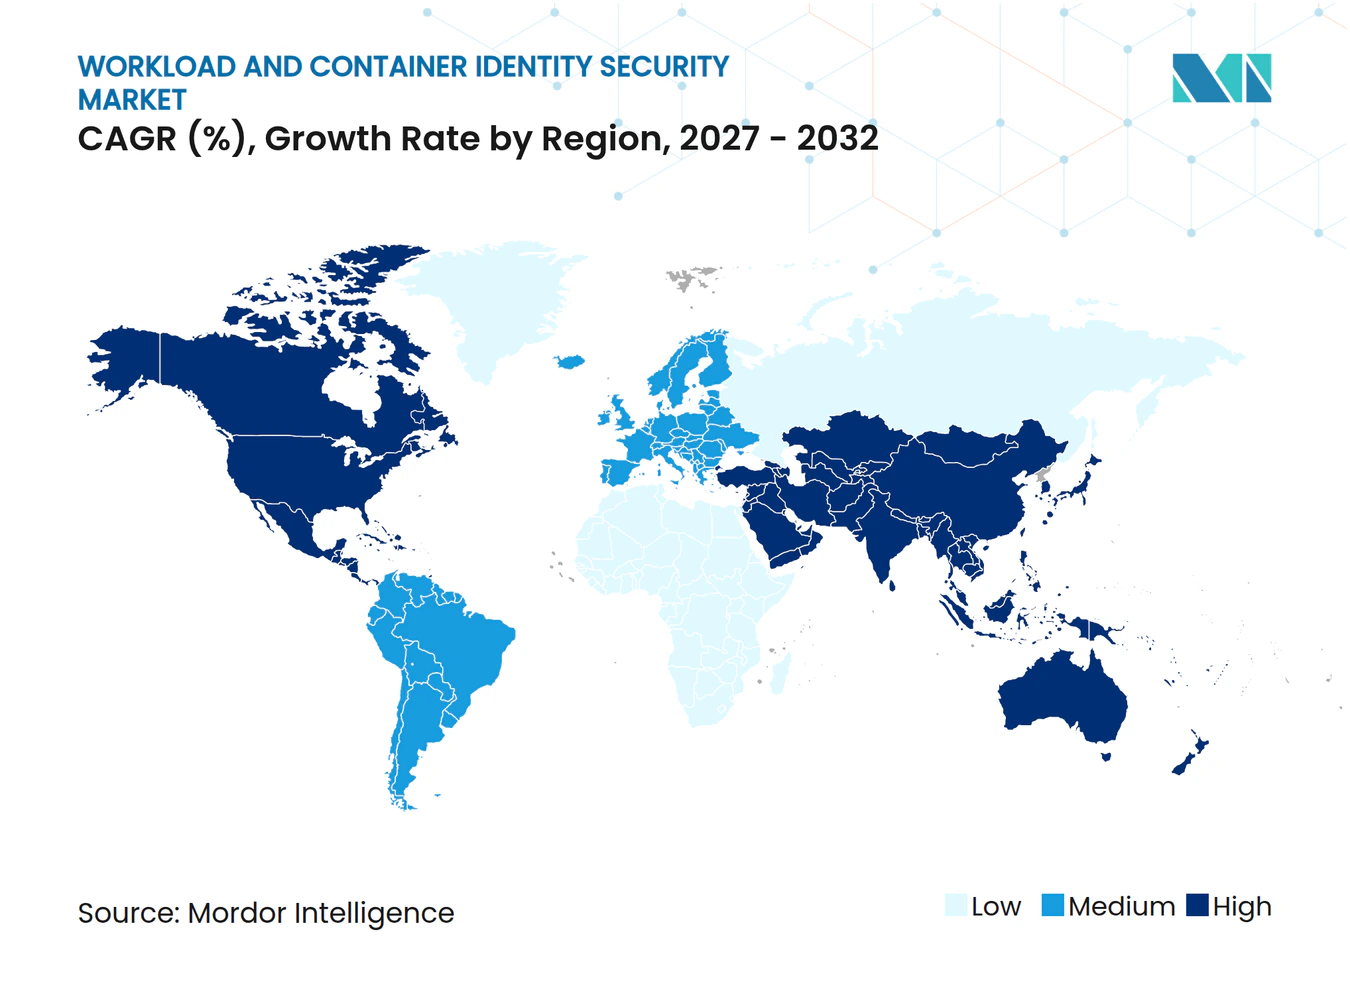
- By geography, North America held 45.98% of revenue in 2026, while Asia-Pacific is projected to expand at a 19.53% CAGR through 2032.
Note: Market numbers in this report are based on Mordor Intelligence's proprietary estimation framework, which combines nine months of actuals with Q4 projections for base year 2026.
Market Trends and Insights
Drivers Impact Analysis of Workload and Container Identity Security Market*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Expansion of Cloud-Native Workloads and Machine-to-Machine Access | +4.2% | Global, concentrated in North America and Asia-Pacific | Short term (≤ 2 years) |
| Zero Trust and Secretless Workload Authentication | +3.8% | Global, early gains in North America and Western Europe | Short term (≤ 2 years) |
| AI Agent and Automated-Process Identity Governance | +3.1% | North America and Europe, spill-over to Asia-Pacific core | Medium term (2-4 years) |
| Kubernetes and Container Identity Sprawl | +2.7% | Global, concentrated in North America, Asia-Pacific, and Northern Europe | Short term (≤ 2 years) |
| Regulatory Pressure for Software Supply-Chain Traceability | +2.1% | North America and EU, emerging requirements in Asia-Pacific | Medium term (2-4 years) |
| Runtime Visibility Through eBPF and Kernel-Level Telemetry | +1.4% | North America and Asia-Pacific core, spill-over to EU | Medium term (2-4 years) |
| Source: Mordor Intelligence | |||
Expansion of Cloud-Native Workloads and Machine-to-Machine Access
Cloud-native deployment is increasing the number of software entities that need secure authentication. The Cloud Native Computing Foundation reported that 56% of organizations ran containers for most or all production applications in 2025, compared with 41% in 2023.[1] The same survey found that 82% of these organizations deployed Kubernetes in production. Each new workload can require an identity assertion, credential exchange, or both, which makes manual governance less practical. Microsoft reported that 51% of workload identities in the environments it surveyed were inactive, leaving credentials that could be exposed to token theft or lateral movement.[2] Sysdig reported that machine identities outnumbered human identities by 40,000 to 1 in large cloud deployments, reinforcing the need for automated identity controls.
Zero Trust and Secretless Workload Authentication
The workload and container identity security market benefits as organizations reduce their use of long-lived secrets for workload-to-workload access. NIST published SP 1800-35 in June 2025 with 19 example implementations for zero trust architecture.[3] Several implementations address workload and service identity through frameworks such as SPIFFE. Red Hat made its Zero Trust Workload Identity Manager generally available in January 2026 for OpenShift environments. The product issues short-lived, cryptographically verified runtime identities and supports secretless vault authentication. NIST SP 800-207A identifies identity-based access as a core control for cloud-native applications, strengthening the compliance case for these platforms.
AI Agent and Automated-Process Identity Governance
AI agents introduce non-human identities that can act under delegated authority and access external services. An agent can also create sub-agents, making accountability more difficult when existing controls focus on a single user or service account. The IETF WIMSE working group released a 2025 draft for an Agent Identity Management System that recognizes limits in current OAuth and OpenID Connect flows for multi-hop delegation. Okta stated in February 2026 that AI agent controls should cover the complete lifecycle from deployment through expiration. Palo Alto Networks introduced Idira in May 2026 with dynamic privilege controls across human, machine, and agentic identities. This approach supports a shift toward unified identity governance rather than separate tools for each identity class.
Kubernetes and Container Identity Sprawl
Container identity sprawl becomes harder to manage as workloads are created and removed in short timeframes. The CNCF Kubernetes Policy Working Group identified least-privilege role-based access control and strong authentication as foundational controls that are often misconfigured or absent in production settings. Sysdig reported that 60% of containers existed for 60 seconds or less. Such short lifecycles can leave gaps in audit processes designed around periodic snapshots. The eBPF Foundation has identified kernel-level tooling, including Cilium and Tetragon, as a way to obtain workload telemetry with lower overhead than legacy sidecar approaches. The workload and container identity security market therefore benefits from security programs that need continuous observation of runtime activity.
Restraints Impact Analysis of Workload and Container Identity Security Market*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Integration Complexity Across Legacy and Hybrid Estates | -3.2% | Global, most severe in Europe and South America where legacy infrastructure density is high | Medium term (2-4 years) |
| Fragmented Assurance Standards for Non-Human Identities | -2.6% | Global | Long term (≥ 4 years) |
| Shortage of Kubernetes and Workload-Identity Skills | -1.9% | Global, most acute in Asia-Pacific and South America | Medium term (2-4 years) |
| Ephemeral-Identity Ownership and Remediation Backlogs | -1.4% | Global, concentrated in North America and EU large enterprise segments | Medium term (2-4 years) |
| Source: Mordor Intelligence | |||
Integration Complexity Across Legacy and Hybrid Estates
The workload and container identity security market faces slower adoption where cloud-native controls must connect with older applications. On-premises workloads may depend on Kerberos, legacy public key infrastructure, or static API keys that cannot be removed without application changes. Aembit stated that hybrid non-human identity protection remains difficult because of static credentials, uneven security, and fragmented tools. This can create different security postures within the same organization. Cloud-native systems may use verified and short-lived credentials, while legacy systems continue to use long-lived secrets. Organizations may delay broad deployments until identity platforms can work across both environments without disrupting existing services.
Fragmented Assurance Standards for Non-Human Identities
Human identity controls benefit from mature protocols such as SAML, SCIM, and OpenID Connect. Non-human identity practices do not yet have the same consistent audit language or regulatory recognition. The OWASP Non-Human Identities Top 10 identifies excessive privileges, inadequate monitoring, and lifecycle gaps as key areas of risk. These weaknesses can make it harder for a buyer to show auditors that its workload credentials are governed effectively. Control functions are often divided between certificate management, secrets management, privileged access management, and cloud entitlement tools. The absence of a common assurance model can moderate procurement among organizations that need clear compliance evidence before changing identity architecture.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Workload and Container Identity Security Market Segment Analysis
By Component:
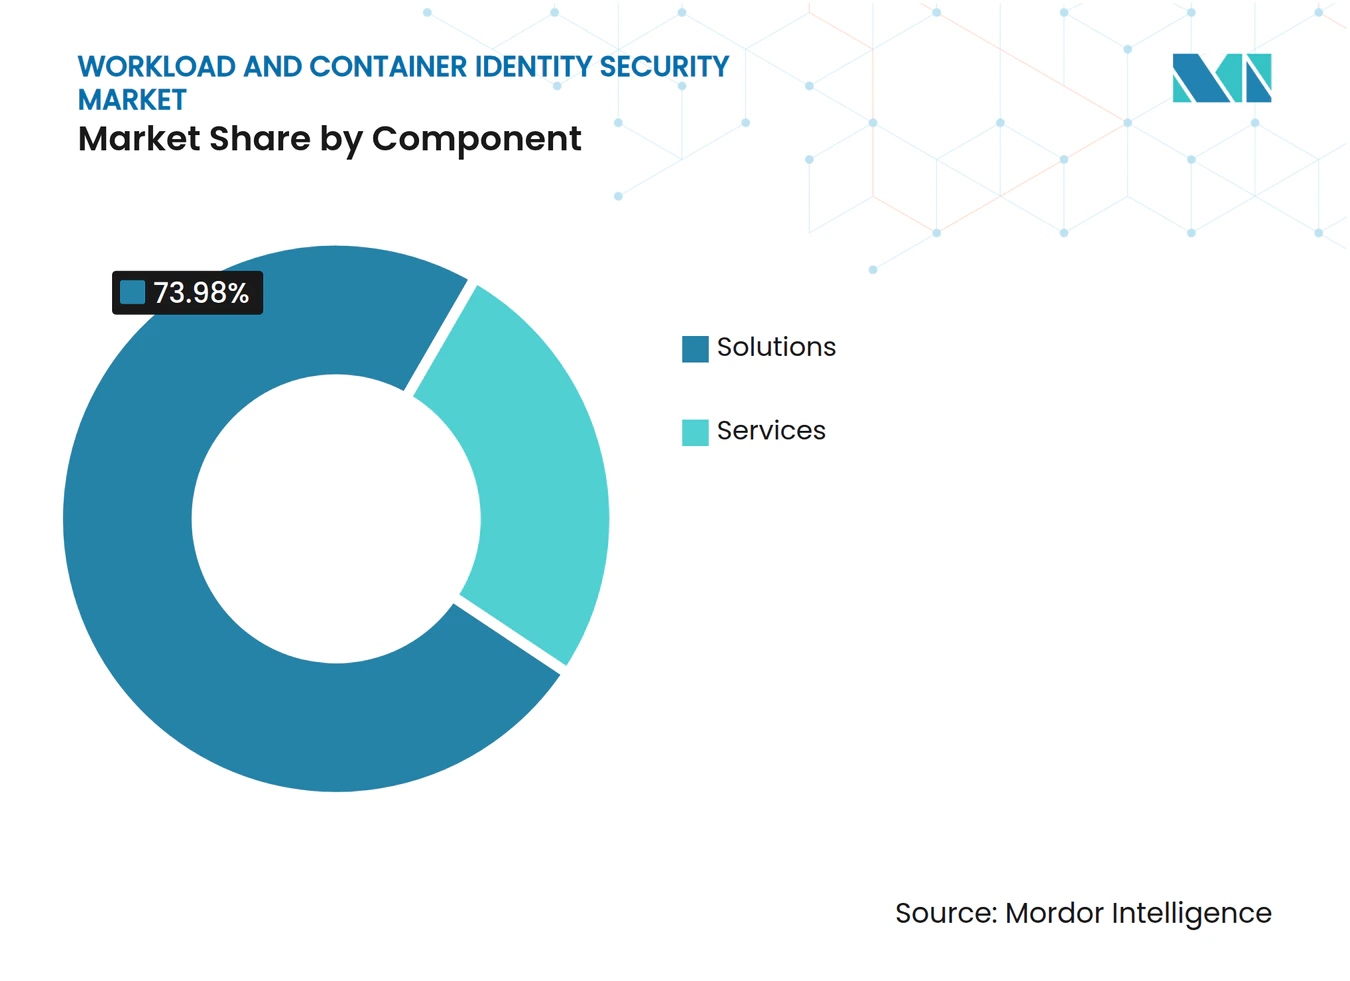
Solutions Anchor Enterprise Workload Identity SpendingSolutions held 73.98% of the workload and container identity security market share in 2026. This position reflects demand for integrated functions that issue workload identities, connect to secrets systems, enforce policy, and maintain lifecycle records. The workload and container identity security industry is moving toward products that can be deployed through cloud services and integrated development tools. SaaS delivery reduces work that previously required dedicated implementation support. Services remain important for organizations moving from legacy PKI to SPIFFE-based controls. These projects require configuration and application expertise that products do not always include. PCI DSS 4.0.1 and NIST SP 800-207A also make platform audit trails and attestation capabilities more relevant to buyer decisions.
Large organizations compare full platform coverage across secrets, machine identity, and agentic identity with the depth of individual specialist products. Smaller organizations often prefer SaaS products that avoid new infrastructure and reduce initial operating demands. This preference can preserve services demand through managed deployments. These deployments increasingly resemble subscriptions instead of conventional consulting work. Platform suppliers are also publishing Terraform providers, continuous integration and delivery plugins, and Kubernetes operator libraries to reduce deployment effort. CyberArk's unified Terraform provider is an example of product-led implementation support. The workload and container identity security market is likely to see services represent a smaller share as self-service functions become more capable. Services will still be needed where organizations have complex hybrid environments or specialized compliance requirements.


By Identity Type:
Workload and Container Identities Drive Market DifferentiationWorkload and Container Identities are projected to expand at a 19.16% CAGR through 2032. This category spans application and service identities, API and service-to-service identities, workload and container identities, machine and device identities, and cryptographic access identities. Containerized architecture drives its importance because every Kubernetes pod requires an identity assertion that can be issued and rotated quickly. The Cloud Native Computing Foundation found that 58% of organizations used Cert Manager and 29% used Cilium in production in 2025. These technologies support the operational environment in which workload identities are used. Traditional PKI systems were generally designed for services with longer operating lives. The workload and container identity security market size for this identity category is supported by demand for credentials that keep pace with container orchestration.
As enterprises standardize on SPIFFE-compatible identity issuers, the boundary between workload identity and API identity becomes less distinct. One credential plane can serve several types of non-human access. This supports platform consolidation by suppliers including CyberArk, HashiCorp, and cloud providers. HashiCorp announced native SPIFFE support in Vault Enterprise during 2025. Cryptographic access identities and machine and device identities may expand more slowly because existing PKI and certificate lifecycle systems already address part of their needs. Application and service identities remain important as organizations extend governance to older microservices. The workload and container identity security industry also gains from users seeking a common policy model across these related identity types. The result is a clearer preference for interoperable identity infrastructure over isolated credential repositories.
By Deployment Mode:
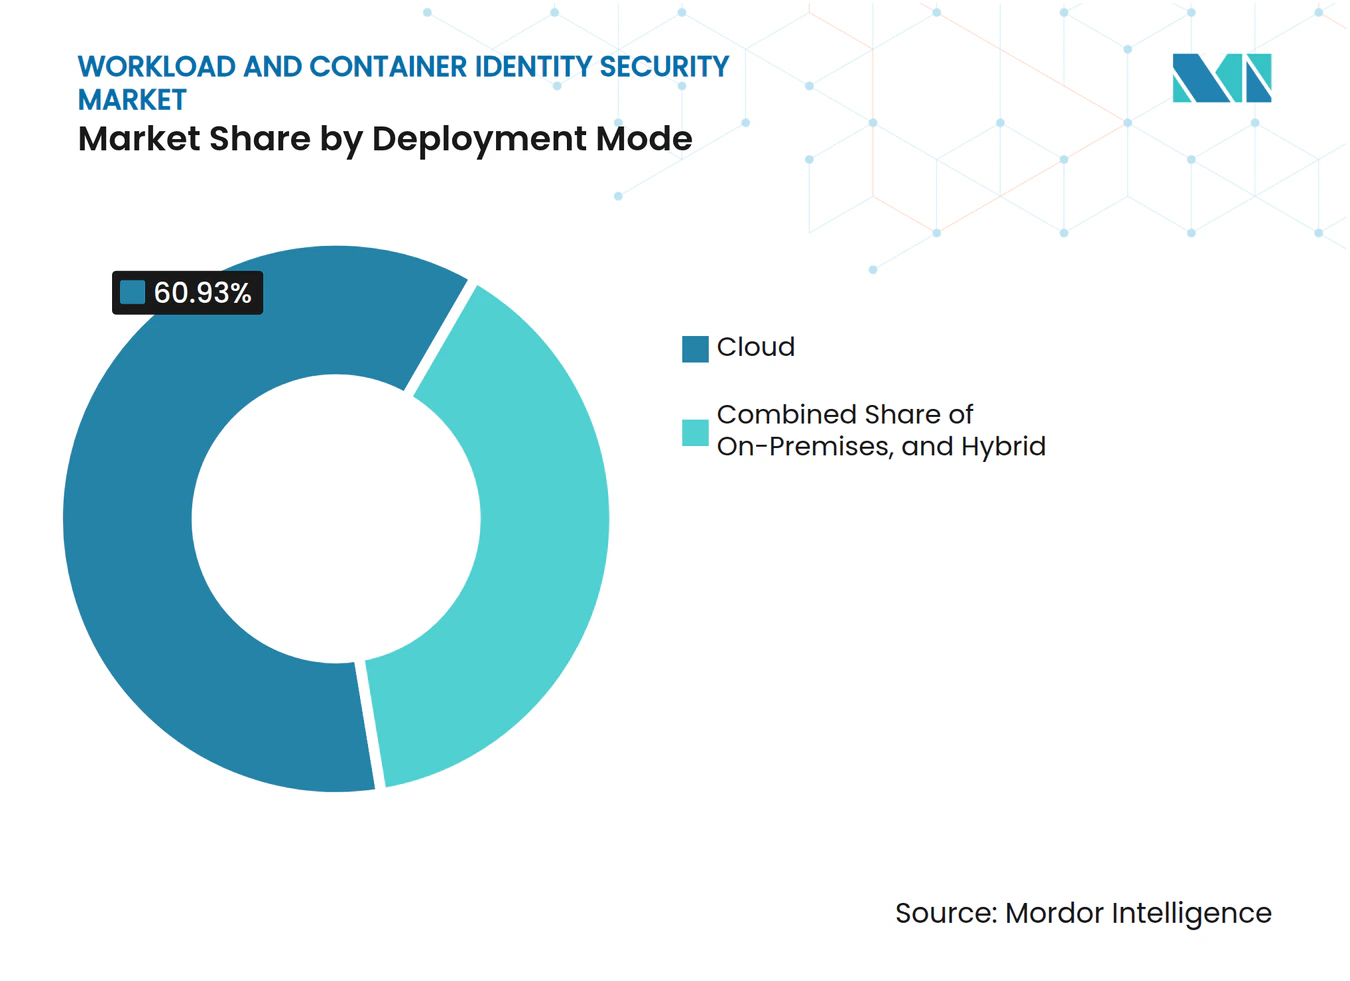
Hybrid Growth Outpaces The Dominant Cloud TierHybrid deployment is projected to expand at a 19.83% CAGR through 2032. Cloud remains the largest deployment mode and is often the first choice for organizations starting a workload identity program. Cloud platforms align with containerized applications through capabilities such as AWS IAM Roles for Service Accounts, GCP Workload Identity Federation, and Azure Managed Identities. Hybrid growth reflects the next stage of adoption, where organizations extend governance to on-premises systems. HashiCorp's native SPIFFE support in Vault Enterprise shows that on-premises secrets suppliers are addressing this need. Aembit has also described the need for a dedicated intermediary when Windows Server workloads and Azure services share an identity plane.
On-premises deployment remains relevant in regulated settings where data residency or security architecture limits the use of cloud-hosted identity infrastructure. Government and national security requirements can also require physical control-plane auditability. The workload and container identity security market size for hybrid use cases is therefore shaped by organizations that must secure new and old systems together. Buyers want to remove static credentials without interrupting essential applications. This need makes intermediary services, federation, and cross-environment policy enforcement important product features. SPIFFE-based ephemeral credentials provide a common direction across cloud, hybrid, and on-premises deployments. The workload and container identity security market can benefit when this standard reduces the technical gap between environments. Adoption will depend on how easily providers connect new identity functions to legacy applications.


By Organization Size:
Large Enterprises Lead, SMEs AccelerateLarge enterprises accounted for 72.91% of revenue in 2026. Their position is linked to the volume of containerized workloads and the established security procurement structures within these organizations. Companies operating thousands of Kubernetes pods across several cloud regions need automated identity controls, audit trails, and policy enforcement. At this scale, workload identity is an operational requirement rather than an optional efficiency measure. Palo Alto Networks introduced Idira in May 2026 with traditional privileged access management, zero standing privilege, and protections for machine and agentic identities. This packaging demonstrates how providers can incorporate workload functions into larger security contracts. Large enterprises also have the resources to fund broad identity modernization programs.
SMEs are the fastest-growing organization-size group because managed service providers and SaaS tools reduce minimum deployment requirements. Smaller teams can adopt cloud-managed patterns without operating on-premises domain controllers or large identity teams. This model supports workload identity controls with less infrastructure overhead. The workload and container identity security market can gain from suppliers that provide guided onboarding and managed operations. Such offerings help organizations that have limited internal Kubernetes and identity expertise. Simplified delivery can also narrow the gap between smaller organizations and larger enterprises that already have mature governance practices. Providers may use tiered packages to give SMEs a clear route from basic credential management to broader policy controls. This creates an opportunity for vendors that can balance ease of use with the audit evidence required by regulated customers.
By End-User Industry:
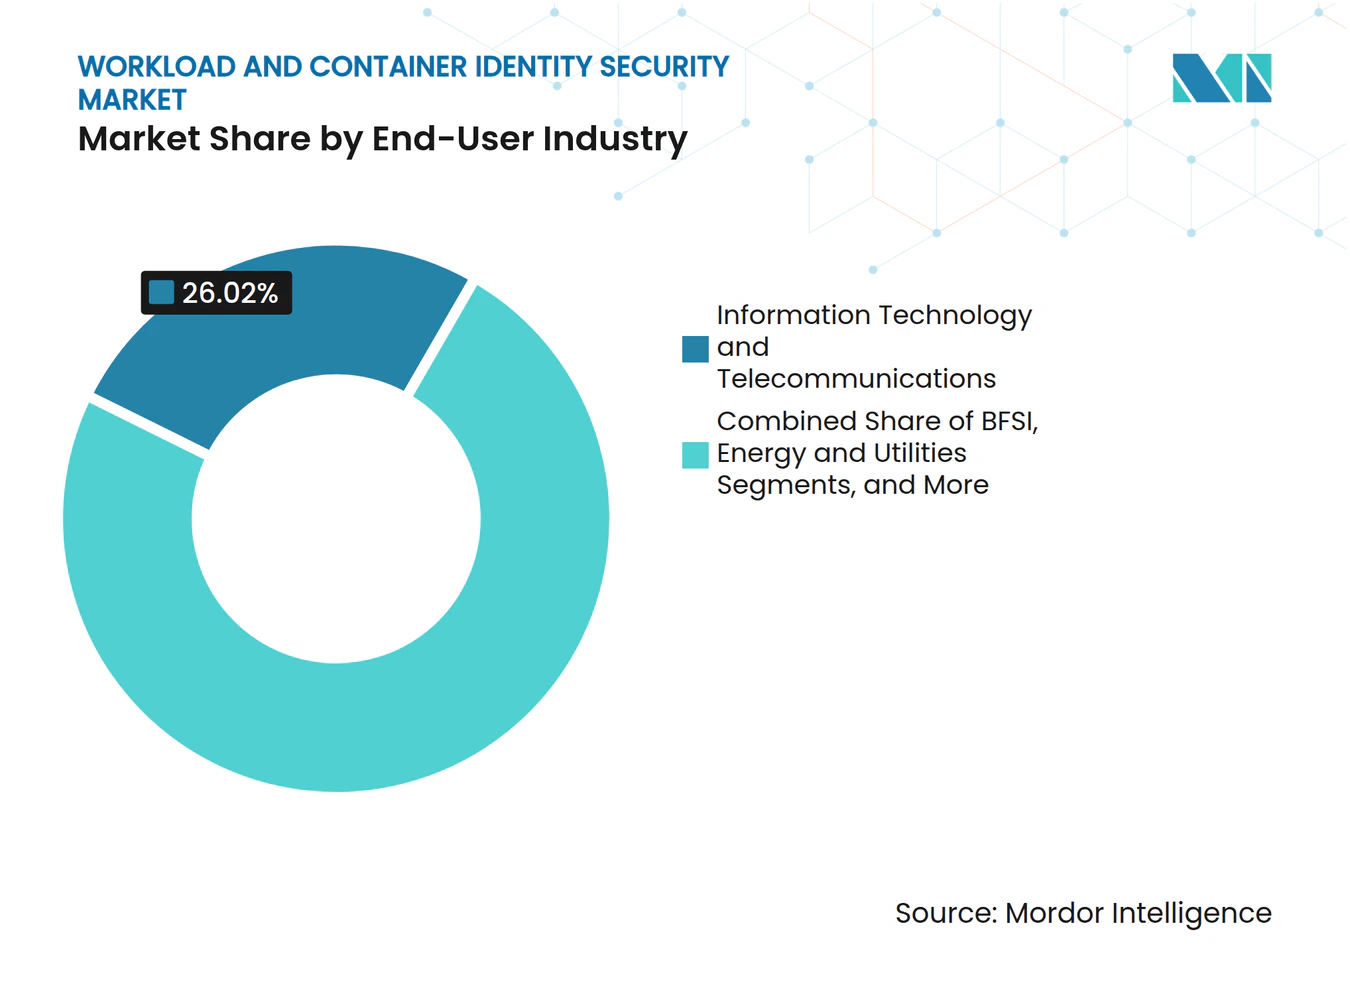
IT And Telecom Sets The Pace As Healthcare AcceleratesHealthcare and Life Sciences is projected to expand at a 19.09% CAGR through 2032. Information Technology and Telecommunications leads current end-user spending because it operates dense cloud-native environments and integrates these architectures early. These organizations encounter identity sprawl, ephemeral credentials, and secrets management issues before formal requirements make the changes necessary. BFSI is the second-largest demand group because of PCI DSS 4.0.1 controls, credential-lifecycle obligations, automated trading, and API banking. Retail and E-Commerce, Government and Defense, and Industrial Manufacturing form additional demand groups. Their needs arise from commerce platform migration, federal zero trust requirements, and operational technology integration. The workload and container identity security market is therefore exposed to several industries that are expanding cloud-based services while tightening access controls.
Healthcare cloud migration and stronger privacy obligations support faster adoption in that sector. Fortified Health Security reported that healthcare organizations identified 4 times more identity and access control vulnerabilities in the first half of 2026 than in the same period of 2025. The revised HIPAA Security Rule is expected to require stronger controls for electronic protected health information, including encryption, multi-factor authentication, and complete access logs. Demand in healthcare is supported by the need to maintain a traceable record for each service interaction. These systems can support covered entities and business associates that need detailed evidence of how workloads accessed protected data. The category also benefits where legacy clinical systems connect to newer cloud platforms. Providers that make hybrid deployment easier may be well positioned to serve these organizations. Healthcare adoption remains tied to the pace of regulatory action and the ability to integrate identity controls without disrupting clinical operations.
Geography Analysis
North America Workload and Container Identity Security Market
North America held 45.98% of the workload and container identity security market in 2026. The region combines extensive cloud infrastructure, federal security requirements, and a supplier base that includes specialists and broad platform providers. CISA updated the minimum elements for software bills of materials in August 2025, adding data fields that include component hash, license, tool name, and generation context. These requirements add pressure for software supply chains to improve traceability. The United States has strong demand from federal agencies and large enterprises. Canada supports regional demand through its established mid-market adoption of centralized identity management. Competition is particularly strong in North America, where Aembit, Teleport, and Silverfort compete with larger platform companies.
Europe and APAC Workload and Container Identity Security Market
Europe is shaped by compliance needs and a comparatively higher concentration of on-premises infrastructure. NIS2 requirements and the EU Cyber Resilience Act are relevant to operators that need stronger traceability across software and container environments. European demand is supported by identity brokers that work across cloud and older systems. Germany, the United Kingdom, and France remain important country-level markets because of financial services, industrial manufacturing, and technology activity. Hybrid deployment has particular relevance because many organizations need controls that bridge their existing infrastructure with newer cloud applications. HashiCorp and Red Hat compete in this setting through their hybrid integration capabilities. Asia-Pacific is projected to expand at a 19.53% CAGR through 2032, making it the fastest-growing geographic segment.
APAC, South America and MEA Workload and Container Identity Security Market
India attracts attention because its cloud-native development base and global IT delivery sector create demand for developer-oriented workload identity tools. Upwind reported in March 2026 that 85% of Indian organizations had experienced a cloud security incident during the preceding year. Japan is modernizing legacy identity infrastructure for hybrid cloud deployments, while South Korea and Australia represent more mature compliance-led markets. South America, led by Brazil, remains earlier in adoption but is supported by data protection requirements. The Middle East and Africa also remain earlier-stage regions, with digital policy programs and cloud adoption creating new demand. Local data residency options can be important as suppliers enter these markets. The workload and container identity security market will depend on providers that can serve regional policy needs while maintaining consistent identity controls across global operations. This workload and container identity security market will also be influenced by each provider's ability to bring cloud and legacy systems under a consistent governance model.
Competitive Landscape
Market Concentration
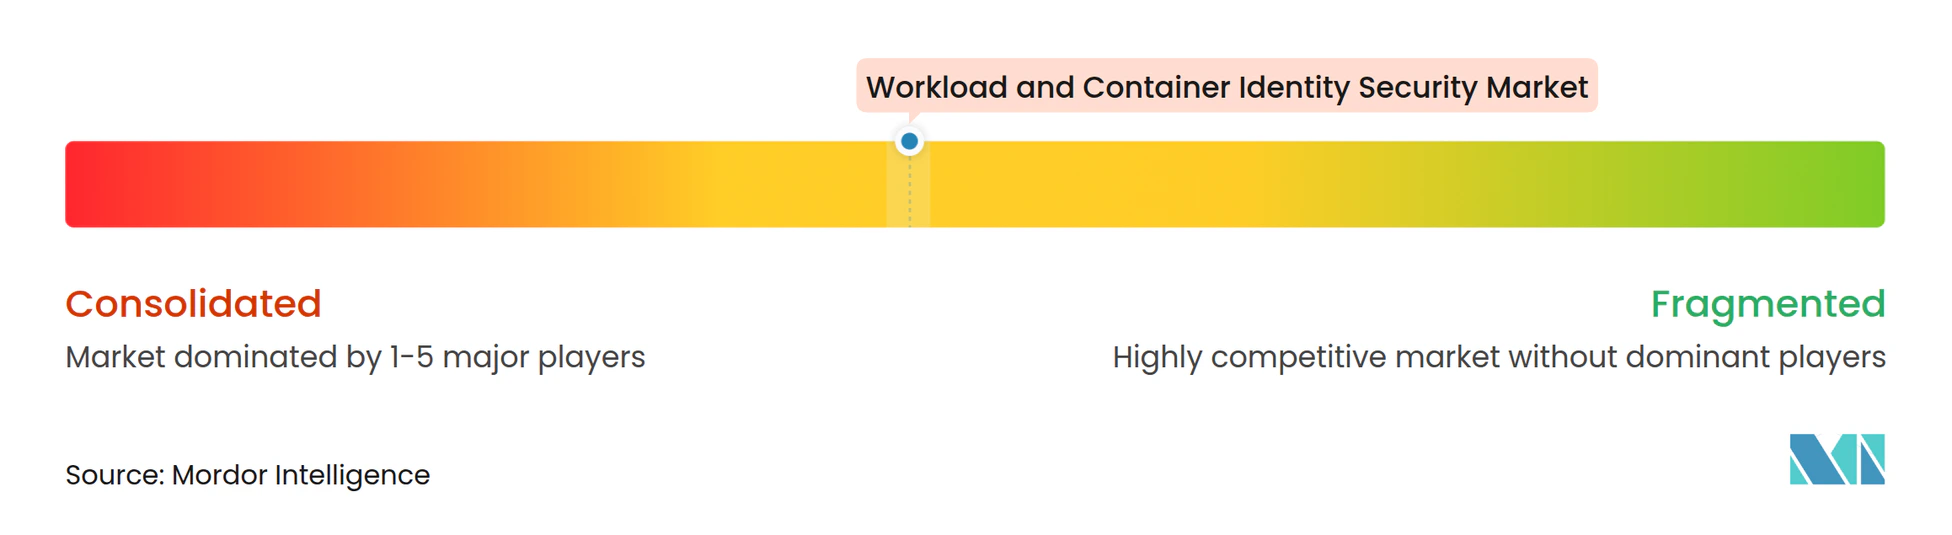
The workload and container identity security market has moderate concentration, with major platform vendors and a larger set of specialized providers. Palo Alto Networks, Microsoft, Amazon Web Services, Google, and HashiCorp have broad security or cloud platforms that can support workload identity functions. Specialists such as Aembit, Silverfort, Teleport, and Akeyless compete through more focused capabilities and can respond quickly where customers need a specific integration or runtime control. Platform suppliers can bundle secrets management, machine identity, privileged access, and governance in a single commercial relationship, which may make procurement and administration easier for organizations seeking fewer suppliers. This can reduce the need for buyers to assemble separate products across several identity control functions. The workload and container identity security market remains open to specialists where technical requirements are not fully met by the wider platforms. Hybrid identity brokerage and multi-hop AI agent delegation are examples of areas where buyers may seek focused providers, especially when workload patterns extend across several cloud environments and existing on-premises systems.
Consolidation has been a central competitive theme. Palo Alto Networks introduced Idira in May 2026 after acquiring CyberArk, combining privileged access management, zero standing privilege, and identity protections for human, machine, and agentic use cases. CyberArk released Workload Identity Manager version 1.11.0 LTS in May 2026, with OIDC federation for Certificate Manager SaaS and service account token authentication. Keyfactor closed a USD 1 billion-plus growth investment led by Summit Partners in July 2026 to expand machine identity security activities. These moves show that larger suppliers are building wider portfolios rather than treating workload identity as a stand-alone feature. This may increase pricing pressure in pure-cloud deployments while raising the importance of product differentiation.
Specialists continue to build positions around runtime visibility, AI agents, and hybrid integration. HashiCorp's Vault Enterprise added native SPIFFE support in 2025, which supports its role in hybrid secrets management architectures. Sysdig introduced a headless cloud security platform for AI agents in May 2026, extending cloud-native protection into AI coding workflows. Aembit made IAM for Agentic AI generally available in October 2025, adding verified agent identities, runtime policy controls, and audit trails. The workload and container identity security market will continue to reward products that can prove value in difficult runtime and cross-cloud environments. The workload and container identity security market also gives specialists an opportunity to serve buyers that need detailed technical support before committing to broader platform contracts. A concentration score cannot be calculated from the available information because the input does not provide the combined revenue share of the leading suppliers.
Workload and Container Identity Security Industry Leaders
-
Palo Alto Networks, Inc.
-
Microsoft Corporation
-
Amazon Web Services, Inc.
-
Google LLC
-
HashiCorp, Inc.
- *Disclaimer: Major Players sorted in no particular order
Workload and Container Identity Security Market Companies Covered in this Report
- Palo Alto Networks, Inc.
- Microsoft Corporation
- Amazon Web Services, Inc.
- Google LLC
- HashiCorp, Inc.
- Oasis Security Ltd.
- Okta, Inc.
- CrowdStrike Holdings, Inc.
- Sysdig, Inc.
- Aqua Security Software Ltd.
- StrongDM, Inc.
- Red Hat, Inc.
- Trend Micro Incorporated
- Teleport, Inc.
- Aembit, Inc.
- Akeyless Security Ltd.
- Delinea, Inc.
- BeyondTrust Corporation
- Keyfactor, Inc.
- Silverfort Ltd.
Recent Industry Developments in Workload and Container Identity Security Market
- October 2026: Aembit released MCP Identity Gateway version 1.35.6086, extending support for additional access token audiences and named-header credential delivery with integrated CrowdStrike AIDR inspection for runtime AI agent access control, expanding the platform's coverage of agentic workload authentication.
- October 2026: Aqua Security was named Cloud Security Platform of the Year in the 10th annual CyberSecurity Breakthrough Awards, recognizing its runtime-first cloud security approach and the April 2026 Aqua Compass MCP server launch for agentic container incident response.
- July 2026: Keyfactor closed a USD 1 billion-plus strategic growth investment led by Summit Partners to expand leadership in machine identity security for the AI and post-quantum enterprise, citing escalating strategic urgency around certificate and workload identity lifecycle management.
- July 2026: Aembit launched an OpenAI Workload Identity Federation Credential Provider, replacing long-lived static API keys with short-lived, identity-bound tokens issued by Aembit on behalf of authorized workloads, extending secretless authentication to AI inference pipelines accessing the OpenAI API.
Global Workload and Container Identity Security Market Report Scope
The Workload and Container Identity Security Market encompasses solutions and services for securing, authenticating, authorizing, and managing workload, container, application, service, machine, and cryptographic identities across cloud, on-premises, and hybrid environments globally. The Market is Segmented by Component (Solutions, and Services), Identity Type (Application and Service Identities, Application Programming Interface and Service-to-Service Identities, Workload and Container Identities, Machine and Device Identities, and Cryptographic Access Identities), Deployment Mode (Cloud, On-Premises, and Hybrid), Organization Size (Large Enterprises, and Small and Medium Enterprises), End-User Industry (BFSI, Healthcare and Life Sciences, Information Technology and Telecommunications, Retail and E-Commerce, Government and Defense, and Other End-user Industries), and Geography (North America, Europe, Asia-Pacific, South America, Middle East, and Africa). The Market Forecasts are Provided in Terms of Value (USD).
Segmentation Overview
| Solutions |
| Services |
| Application and Service Identities |
| Application Programming Interface and Service-to-Service Identities |
| Workload and Container Identities |
| Machine and Device Identities |
| Cryptographic Access Identities |
| Cloud |
| On-Premises |
| Hybrid |
| Large Enterprises |
| Small and Medium Enterprises |
| BFSI |
| Healthcare and Life Sciences |
| Information Technology and Telecommunications |
| Retail and E-Commerce |
| Energy and Utilities |
| Government and Defense |
| Other End-user Industries |
| North America | United States |
| Canada | |
| Mexico | |
| South America | Brazil |
| Argentina | |
| Rest of South America | |
| Europe | Germany |
| United Kingdom | |
| France | |
| Italy | |
| Spain | |
| Russia | |
| Rest of Europe | |
| Asia-Pacific | China |
| India | |
| Japan | |
| South Korea | |
| Australia | |
| Rest of Asia-Pacific | |
| Middle East | Saudi Arabia |
| United Arab Emirates | |
| Turkey | |
| Rest of Middle East | |
| Africa | South Africa |
| Egypt | |
| Nigeria | |
| Rest of Africa |
| By Component | Solutions | |
| Services | ||
| By Identity Type | Application and Service Identities | |
| Application Programming Interface and Service-to-Service Identities | ||
| Workload and Container Identities | ||
| Machine and Device Identities | ||
| Cryptographic Access Identities | ||
| By Deployment Mode | Cloud | |
| On-Premises | ||
| Hybrid | ||
| By Organization Size | Large Enterprises | |
| Small and Medium Enterprises | ||
| By End-User Industry | BFSI | |
| Healthcare and Life Sciences | ||
| Information Technology and Telecommunications | ||
| Retail and E-Commerce | ||
| Energy and Utilities | ||
| Government and Defense | ||
| Other End-user Industries | ||
| By Geography | North America | United States |
| Canada | ||
| Mexico | ||
| South America | Brazil | |
| Argentina | ||
| Rest of South America | ||
| Europe | Germany | |
| United Kingdom | ||
| France | ||
| Italy | ||
| Spain | ||
| Russia | ||
| Rest of Europe | ||
| Asia-Pacific | China | |
| India | ||
| Japan | ||
| South Korea | ||
| Australia | ||
| Rest of Asia-Pacific | ||
| Middle East | Saudi Arabia | |
| United Arab Emirates | ||
| Turkey | ||
| Rest of Middle East | ||
| Africa | South Africa | |
| Egypt | ||
| Nigeria | ||
| Rest of Africa | ||
Key Questions Answered in the Report
Question
Answer
What is the workload and container identity security market size?
The workload and container identity security market is projected to rise from USD 1.32 billion in 2026 and USD 1.53 billion in 2027 to USD 3.54 billion by 2032.
What is driving demand for workload and container identity security?
Cloud-native deployments, zero trust adoption, short-lived workload credentials, and governance needs for AI agents are increasing demand.
Which component leads spending?
Solutions led with 73.98% of revenue in 2026 because buyers favor platforms that combine identity issuance, policy enforcement, lifecycle governance, and secrets integration.
Which deployment mode is expanding fastest?
Hybrid deployment is projected to expand at a 19.83% CAGR through 2032 as organizations extend controls across cloud and on-premises environments.
Which end-user sector is projected to expand fastest?
Healthcare and Life Sciences is projected to expand at a 19.09% CAGR through 2032, supported by cloud migration and stronger access-control requirements.
Which region is projected to expand fastest?
Asia-Pacific is projected to expand at a 19.53% CAGR through 2032, supported by cloud adoption, digitalization, and expanding security requirements.