
OT Threat Intelligence Market Size and Share
Market Overview
| Study Period | 2021 - 2032 |
|---|---|
| Market Size (2027) | USD 2.77 Billion |
| Market Size (2032) | USD 7.22 Billion |
| Growth Rate (2027 - 2032) | 21.15 % |
| Fastest Growing Market | Asia-Pacific |
| Largest Market | North America |
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image © Mordor Intelligence. Reuse requires attribution under CC BY 4.0. | |
OT Threat Intelligence Market Analysis by Mordor Intelligence
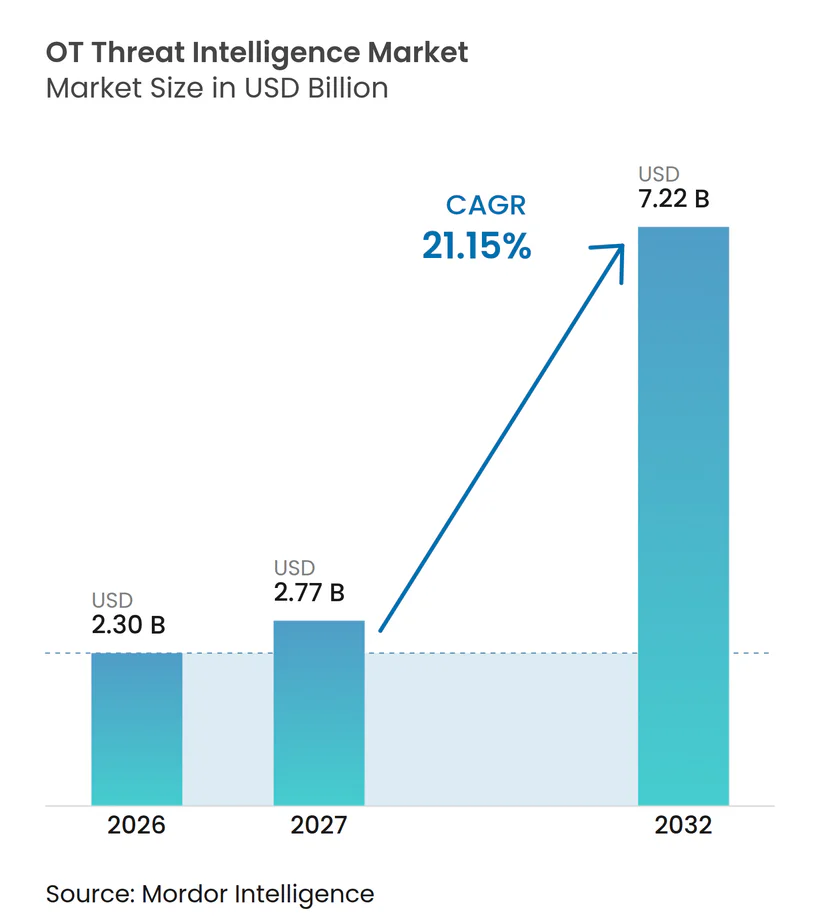
The OT threat intelligence market size was USD 2.30 billion in 2026 and is projected to reach USD 7.22 billion by 2032, expanding at a CAGR of 21.15% from 2027 to 2032. Rising attacks on industrial systems are moving threat intelligence from a specialist capability to an operational requirement for asset owners. Regulatory monitoring duties, cyber-insurance requirements, and connected industrial environments are reinforcing demand for platforms that connect asset context with adversary activity. The OT threat intelligence market is also benefiting from managed delivery models, which make specialized monitoring more accessible for operators with limited internal security teams. Platform vendors are strengthening their positions through broader device visibility, industrial protocol coverage, and integrations that link IT and OT security workflows. Legacy infrastructure, high retrofit costs, and shortages of personnel with both process and cybersecurity experience continue to limit the pace of deployment.
Key Report Takeaways
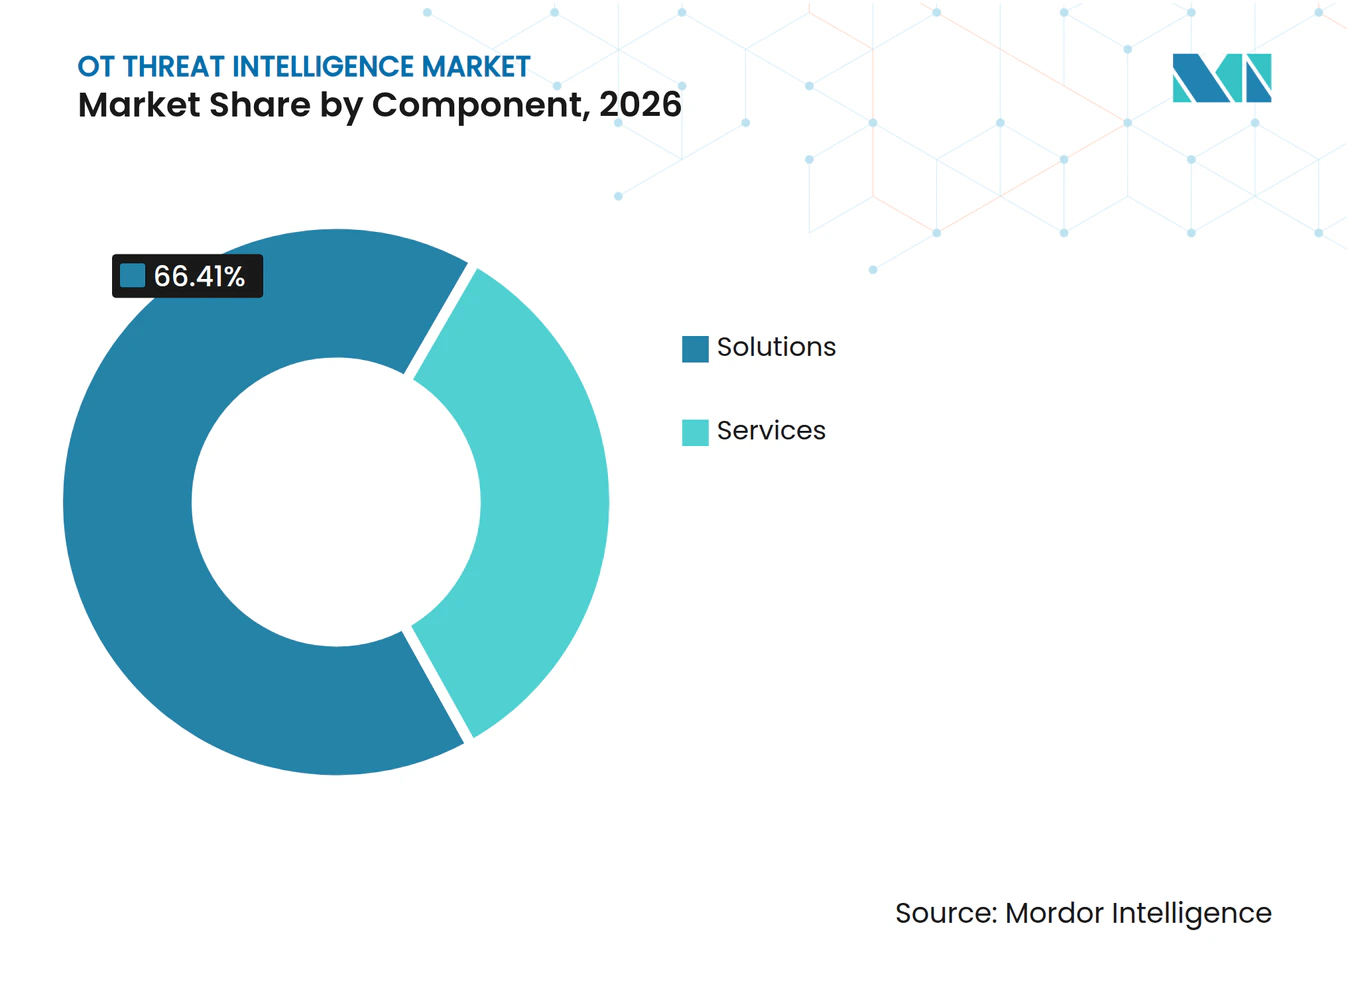
- By component, solutions held 66.41% of the OT threat intelligence market share in 2026, while services are projected to expand at a 22.65% CAGR through 2032.
- By deployment mode, on-premises systems accounted for 68.19% of the OT threat intelligence market size in 2026, while cloud deployment is projected to grow at a 22.91% CAGR through 2032.
- By application, threat detection and monitoring held 59.10% of the OT threat intelligence market in 2026, while incident response and forensics are expected to expand at a 22.34% CAGR through 2032.
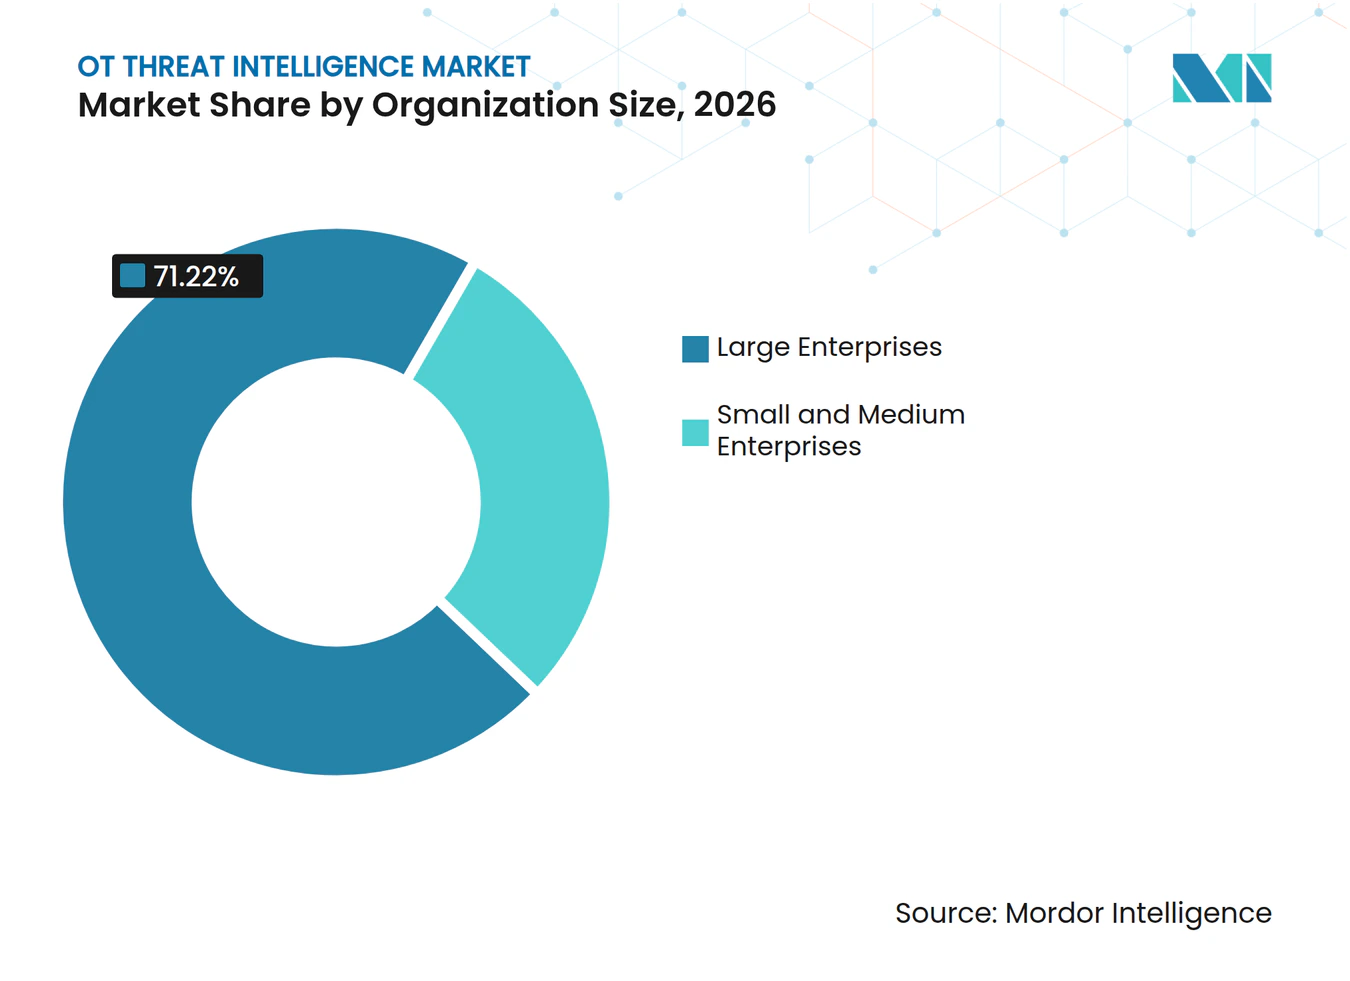
- By organization size, large enterprises accounted for 71.22% of the OT threat intelligence market in 2026, while small and medium enterprises are projected to grow at a 23.29% CAGR through 2032.
- By end-user industry, industrial manufacturing held 28.19% of the OT threat intelligence market in 2026, while energy and utilities are projected to expand at a 21.78% CAGR through 2032.
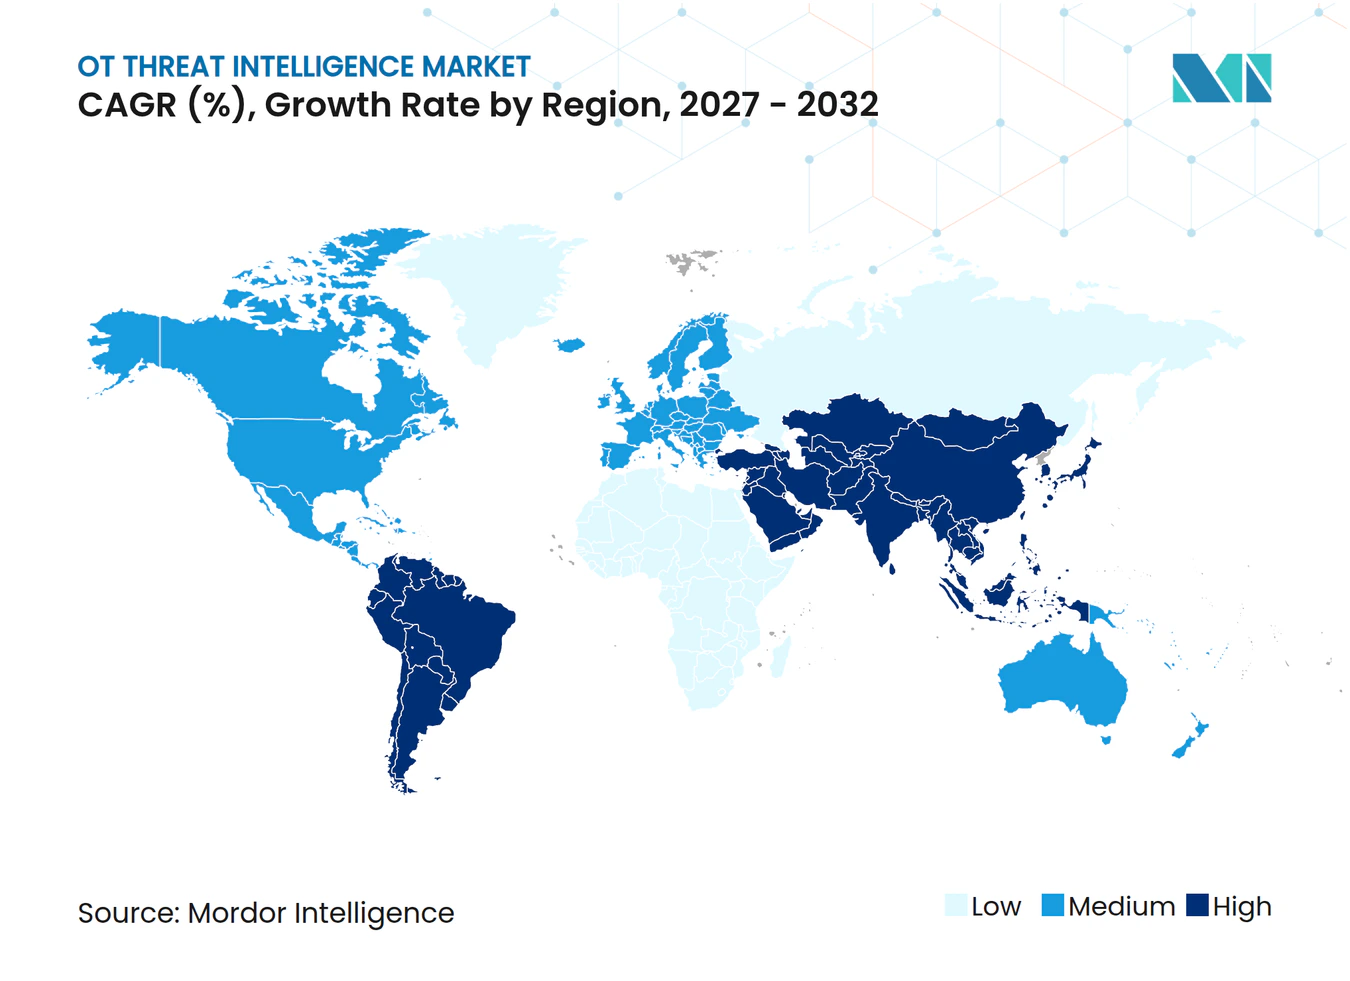
- By geography, North America held 35.41% of the market in 2026, while Asia-Pacific is projected to grow at a 22.06% CAGR through 2032.
Note: Market numbers in this report are based on Mordor Intelligence's proprietary estimation framework, which combines nine months of actuals with Q4 projections for base year 2026.
Market Trends and Insights
Drivers Impact Analysis of OT Threat Intelligence Market*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Escalating Cyberattacks on Critical Infrastructure | +5.5% | Global, concentrated in North America, Europe, and the Middle East | Short term (≤ 2 years) |
| IT-OT Convergence Expanding the Industrial Attack Surface | +4.8% | Global, with high intensity in North America and APAC manufacturing corridors | Medium term (2-4 years) |
| Regulatory Mandates for Critical-Infrastructure Cybersecurity | +3.6% | North America and EU core, extending into APAC national frameworks | Medium term (2-4 years) |
| Industrial IoT, Remote Operations, and Predictive-Maintenance Expansion | +2.8% | APAC and North America industrial zones | Long term (≥ 4 years) |
| Cyber-Insurance and Procurement Requirements for Demonstrable OT Resilience | +1.2% | North America and EU, with spillover to APAC | Short term (≤ 2 years) |
| Asset-Contextualized Intelligence Reducing Alert Noise in Safety-Critical Networks | +0.6% | Global | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Escalating Cyberattacks on Critical Infrastructure
Attacks on industrial control systems have increased the need for intelligence that supports operational decisions in critical infrastructure settings. A 2026 federal advisory described activity targeting Rockwell Automation Allen-Bradley PLCs, Schneider Electric Modicon controllers, and Siemens S7-1200 systems in energy, water, and government environments. The reported incidents involved operational disruption and financial losses, showing that attacks can affect physical processes as well as information systems. The OT threat intelligence market is responding to this risk by offering products that link industrial assets to attacker behavior and vulnerability context. General threat feeds provide less value when operators must determine which device or process requires immediate attention. Industrial operators, therefore, need prioritized intelligence that can support monitoring, response, and recovery planning.
IT-OT Convergence Expanding the Industrial Attack Surface
The connection between enterprise networks and operational environments has broadened the attack surface across industrial facilities. Dragos reported that ransomware groups targeting industrial organizations increased from 80 in 2024 to 119 in 2025, affecting more than 3,300 organizations, with manufacturers representing most victims. The same report described attack paths that begin in IT environments and then move toward operational systems. The OT threat intelligence market is gaining relevance because it can help security teams connect those paths across both domains. Cloud services, remote administration tools, and identity systems have further weakened the traditional separation between IT and OT. Platforms that correlate device, network, and identity signals can help teams detect activity before it affects industrial operations.
Regulatory Mandates for Critical-Infrastructure Cybersecurity
Binding cybersecurity requirements are creating sustained demand outside discretionary information technology budgets. The Federal Energy Regulatory Commission approved Reliability Standard CIP-015-1 in July 2025, requiring internal network security monitoring within electronic security perimeters for bulk electric system assets. CISA and the UK National Cyber Security Center also issued eight secure-connectivity principles for operational technology in January 2026.[1] These requirements increase the value of auditable asset inventories, monitoring records, and incident response evidence. The OT threat intelligence market supports these needs by combining visibility with risk prioritization and documentation. Compliance programs are therefore becoming a route for industrial organizations to formalize security investment.
Industrial IoT, Remote Operations, and Predictive-Maintenance Expansion
Industrial Internet of Things deployments, remote operations, and predictive maintenance are expanding the number of connected systems that require protection. NTT and Toshiba demonstrated remote control of production equipment 300 km away through a cloud-based PLC within a 20-millisecond control cycle in November 2025. The demonstration shows how distributed control architectures can increase the effect of latency, configuration errors, or malicious interference. IEC PAS 62443-1-6:2025 addresses Industrial IoT security requirements within the IEC 62443 framework. The OT threat intelligence market can support these environments by interpreting data from heterogeneous industrial protocols and identifying activity that merits review. As remote access grows, products that reduce alert volume while preserving process context should become more useful.
Restraints Impact Analysis of OT Threat Intelligence Market*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Legacy PLC, DCS, and SCADA Protocol Constraints | -2.4% | Global, most acute in aging North American, European, and South American brownfield plants | Medium term (2-4 years) |
| High Retrofit Cost and Operational-Disruption Risk | -1.6% | Global, most severe in SME-concentrated industrial clusters in APAC and South America | Medium term (2-4 years) |
| Shortage of OT-Specific Cybersecurity and Process-Safety Talent | -0.9% | Global, with critical gaps in APAC and the Middle East | Long term (≥ 4 years) |
| Limited Telemetry and Incomplete Industrial Asset Inventories | -0.6% | Global, particularly in brownfield OT deployments | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Legacy PLC, DCS, and SCADA Protocol Constraints
Many PLCs installed during the 1990s and 2000s lack the processing capacity needed for encryption, secure boot, or agent-based monitoring. This limits the telemetry available from brownfield plants, making complete asset visibility difficult to achieve. Siemens discontinued the S7-300 series in October 2025, but legacy systems remain common across industrial facilities. Passive monitoring is useful in these settings because it avoids placing software directly on fragile devices. The OT threat intelligence market presents an opportunity for vendors to monitor traffic without altering critical control equipment. Incomplete data will remain a barrier, as older protocols offer limited authentication, logging, or diagnostic capabilities.
High Retrofit Cost and Operational-Disruption Risk
Security retrofits can require capital investment and planned downtime that many operators find difficult to accept. TXOne Networks reported in 2026 that 54% of OT security decision-makers identified compatibility with legacy equipment as their leading constraint, while 38% identified high replacement costs as a primary barrier. A mid-size wastewater plant retrofit with a cybersecurity scope can require USD 80,000 to USD 400,000 in capital expenditure. Large municipal installations can require USD 1 million to USD 3 million. Managed services that use passive monitoring can reduce disruption by avoiding major network reconfiguration. The OT threat intelligence market can therefore benefit when providers offer phased deployment approaches that fit operational maintenance windows.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
OT Threat Intelligence Market Segment Analysis
By Component:
Solutions Lead Integrated Industrial IntelligenceSolutions accounted for 66.41% of the OT threat intelligence market in 2026, reflecting demand for platforms that combine asset discovery, vulnerability context, and threat detection. Integrated platforms can reduce the burden of joining multiple point products across complex industrial environments. OT protocols such as Modbus, DNP3, OPC UA, and PROFINET require specialized interpretation that many general-purpose security products lack. This requirement favors solutions built for industrial traffic and process contexts. Services have lower current revenue but are projected to grow at a 22.65% CAGR through 2032. Managed detection and response contracts can give plants access to specialist monitoring without building large internal teams.
The component mix also reflects a division between platform licensing and labor-based delivery. Solutions can create a shared view of assets, exposure, threats, and operational priorities across multiple sites. They may also reduce duplicate work for security and engineering teams with separate responsibilities. Dragos stated that EmberAI operates on its OT intelligence fabric and supports investigation across more than 600 protocols. Such capabilities can shift value toward embedded intelligence when users need faster assessment of industrial events. Services remain important when operators lack security staff or need incident response support. The OT threat intelligence industry is likely to retain both models because industrial organizations vary widely in technical resources and risk tolerance.


By Deployment Mode:
On-Premises Control Meets Cloud FlexibilityOn-premises systems held 68.19% of the OT threat intelligence market in 2026, reflecting longstanding preferences for local control in high-criticality environments. Many plant engineers remain cautious about transmitting raw operational telemetry across internet-routable connections. This concern is particularly strong in environments with air-gap traditions or strict security procedures. Cloud deployment is projected to expand at a 22.91% CAGR through 2032. Managed cloud services can provide smaller operators with advanced detection without a comparable investment in local hardware. The OT threat intelligence market is consequently moving toward options that allow customers to choose local, cloud, or hybrid operating models.
Deployment choice depends on risk appetite, available connectivity, and the location of operational data. On-premises deployments can support local processing where latency, sovereignty, or process sensitivity are important. Cloud delivery can simplify updates, analyst access, and multi-site monitoring when secure connectivity is available. Hybrid models can retain sensitive collection functions within the facility while using centralized analytics for wider review. With Platform 3.1, Dragos introduced Linux-native agents that run directly on sensors.[2] This approach shows how vendors are adapting products for flexible deployment. The OT threat intelligence market can broaden its customer base when platform design does not force a single architecture.
By Application:
Detection Remains the Foundational Use CaseThreat detection and monitoring held 59.10% of the OT threat intelligence market in 2026, making it the largest application. Continuous detection provides the evidence needed for vulnerability prioritization, incident response, and compliance work. Industrial systems present distinct monitoring challenges because many protocols lack rich native logs or anomaly baselines. Attackers can manipulate process variables in ways that do not resemble conventional IT events. Incident response and forensics are projected to grow at a 22.34% CAGR through 2032. This growth reflects the need to reconstruct events, demonstrate readiness for recovery, and meet documentation requirements following incidents.
Exposure management is becoming more useful as asset inventories improve and operators gain greater visibility into connected devices. Forescout reported 508 ICS advisories covering 2,155 vulnerabilities during 2025. Risk-based prioritization helps teams focus on vulnerabilities that can affect production, safety, or critical services. Compliance and audit readiness remain relevant as requirements for monitoring and incident reporting increase. Application demand, therefore, extends beyond alerting to include evidence management and response coordination. The OT threat intelligence market must support these related tasks without overwhelming operations teams with low-value notifications. Products that map technical findings to operational impact should have an advantage in environments with limited staff.
By Organization Size:
Large Enterprises Hold Scale, SMEs Gain AccessLarge enterprises accounted for 71.22% of the OT threat intelligence market in 2026 because they operate complex, often geographically dispersed industrial portfolios. Energy operators, chemical manufacturers, and oil and gas companies may need centralized visibility across many facilities. These customers commonly require multi-site normalization, customized intelligence feeds, and dedicated response support. Such requirements favor vendors with broad protocol coverage and established delivery capacity. Small and medium enterprises are projected to expand at a 23.29% CAGR through 2032. This growth reflects insurance, procurement, and customer requirements that increasingly reach smaller industrial suppliers.
SMEs also have a greater presence in legacy equipment environments, where traditional security deployments can be difficult. Cloud-delivered managed intelligence can reduce the capital barrier that previously limited access to advanced monitoring. Passive sensors may be better suited to facilities that cannot tolerate frequent network changes. The OT threat intelligence market can meet this need through simpler pricing, limited-scope services, and practical implementation support. Large enterprises will remain important because their operations generate complex requirements and larger contract values. However, SME adoption expands the addressable base beyond a small group of major industrial operators. Vendors that tailor deployment and support to these buyers can build a meaningful position in the OT threat intelligence industry.

By End-User Industry:
Manufacturing Leads, Energy and Utilities AccelerateIndustrial manufacturing accounted for 28.19% of the OT threat intelligence market in 2026, supported by its large installed base of connected engineering workstations and production systems. Manufacturing facilities often connect enterprise networks with PLC programming interfaces, creating routes for lateral movement. Dragos reported that manufacturers accounted for most organizations affected by OT ransomware in 2025. This exposure makes continuous visibility and asset-level detection important for plant operators. Energy and utilities are projected to expand at a 21.78% CAGR through 2032. Grid and pipeline systems face direct targeting risks and increasingly formal monitoring requirements.
Oil and gas, transportation and logistics, chemicals and pharmaceuticals also face growing pressure to strengthen control-system security. Their assets may operate in remote settings, run continuously, or support essential supply chains. Mining and metals, water and wastewater, and other users add demand as ransomware groups target a wider range of industrial operations. The Federal Energy Regulatory Commission's CIP-015-1 standard provides a clear monitoring requirement for relevant bulk electric system assets. These requirements can make intelligence platforms part of ongoing operational governance rather than a discrete technology purchase. The OT threat intelligence market must address the diverse asset types, protocols, and compliance requirements across these verticals.
Geography Analysis
The Americas OT Threat Intelligence Market
North America held 35.41% of the OT threat intelligence market in 2026, supported by a mature regulatory environment and a dense base of critical infrastructure operators. NERC CIP requirements, pipeline security directives, and federal guidance have increased the focus on continuous monitoring and rapid incident reporting. The United States accounts for the largest share of regional demand because of its extensive energy, water, manufacturing, and transportation infrastructure. Established domestic vendors also offer customers a broad range of OT security platforms and services. South America remains an earlier-stage opportunity, with Brazil and Argentina emerging as active investment areas as energy systems become more interconnected.
Europe OT Threat Intelligence Market
Europe is the second-largest regional area within the OT threat intelligence market, supported by the EU NIS2 Directive and industrial security requirements. NIS2 establishes higher expectations for cybersecurity risk management among affected entities. Germany is a leading national market, where many organizations face cybersecurity oversight and requirements for critical infrastructure protection. The United Kingdom, France, and Italy also have material industrial demand. Manufacturing disruption caused by a cyberattack in 2025 and ongoing power grid attacks in Ukraine raised board-level attention to operational resilience across the region. These conditions are increasing interest in products that can document device visibility, monitor networks, and prioritize industrial risk.
APAC and MEA OT Threat Intelligence Market
Asia-Pacific is projected to grow at a 22.06% CAGR through 2032, making it the fastest-growing regional area. Japan's active cyber defense framework took full effect on October 1, 2026, and requires critical infrastructure operators to report cyberattacks to the government. India has also introduced power-sector cybersecurity requirements covering network segmentation, continuous monitoring, and incident response. China, South Korea, and Japan represent the largest national markets in the region. The Middle East and Africa offer earlier-stage opportunities as smart-city programs and industrial modernization expand connected operations. The OT threat intelligence market can gain from these programs, where local security capabilities develop more slowly than the underlying digital infrastructure.
Competitive Landscape
Market Concentration
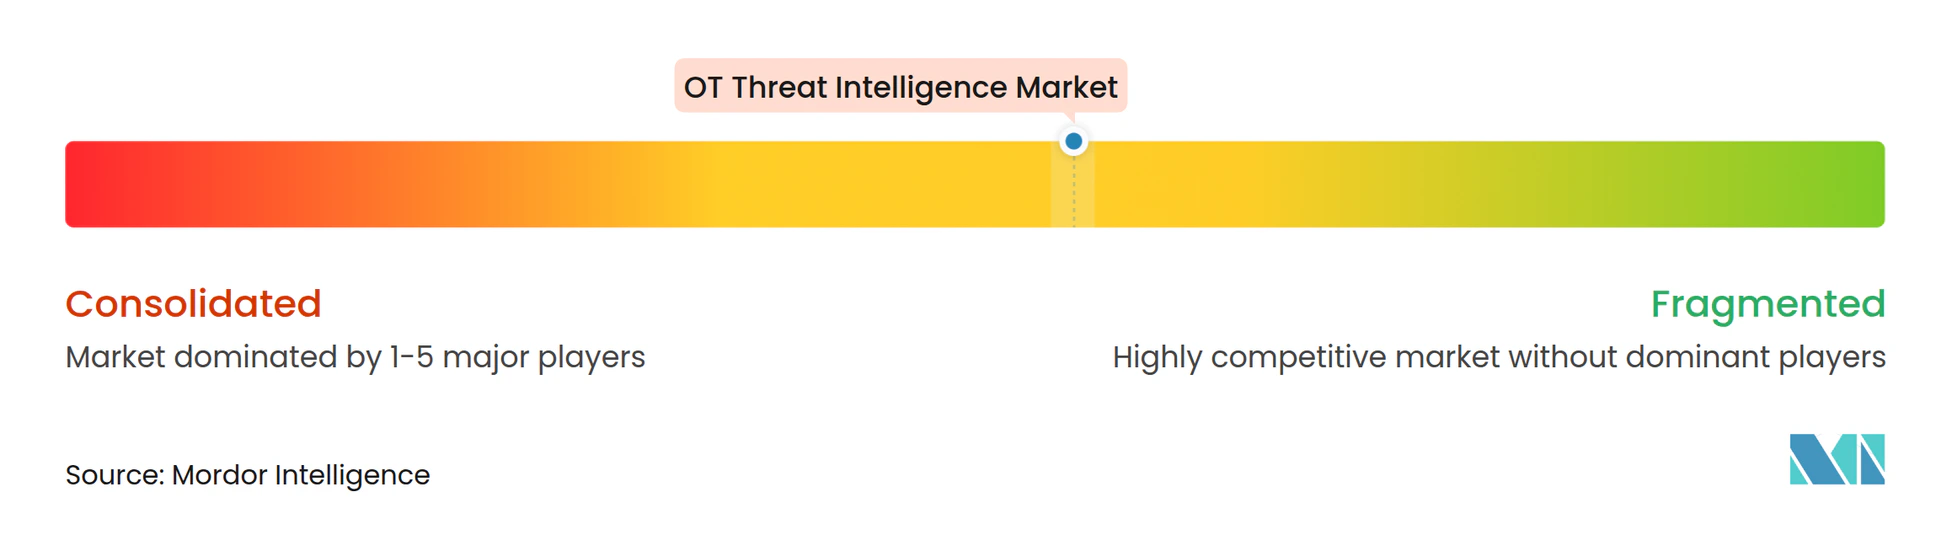
The OT threat intelligence market is moderately concentrated among leading platform providers, while specialist vendors compete in specific sectors and deployment needs. Dragos, Claroty, and Nozomi Networks have built differentiated positions through industrial telemetry, protocol expertise, and asset visibility. Nozomi Networks reported that it protects more than 115 million industrial and IoT assets across over 12,000 installations.[3] Dragos stated that its intelligence fabric processes more than 5 petabytes of daily OT telemetry across more than 600 protocols. These data resources can strengthen detection quality and make it harder for smaller vendors to match the breadth of established platforms. The competitive position of the OT threat intelligence market leaders also depends on their ability to translate technical data into useful actions for plant and security teams.
Accenture finalized a majority investment in Dragos in June 2026, broadening Dragos's distribution in critical infrastructure accounts while retaining the company's operational independence. Dragos then acquired runZero and NetRise in September 2026, extending its coverage across devices, networks, cloud environments, and software supply chains. Claroty introduced the Claire CPS-native AI security agent in May 2026, drawing on data from more than 6,500 OEMs and over 20,000 deployment sites. Nozomi Networks launched Vantage IQ in January 2026 as a private, company-trained AI assistant for OT and IoT security teams. These moves show that large providers are investing in AI-supported analysis, broader visibility, and more connected security operations. The OT threat intelligence market is also moving toward products that connect IT, OT, IoT, and cloud risk in a single operating model.
Smaller vendors have opportunities in brownfield sites and sectors with specialized operational requirements. TXOne Networks, Radiflow, Rhebo, and SIGA OT Solutions focus on approaches that can support older equipment without extensive network changes. Tenable brings enterprise vulnerability management capabilities to exposure management use cases. Regional managed security providers can support smaller European operators as they enter formal OT security programs under NIS2-related obligations. Competition is shaped by technology depth, delivery capacity, sector expertise, and the ability to work with legacy assets. The OT threat intelligence industry remains open to specialized providers where broad platforms do not meet local implementation or pricing needs.
OT Threat Intelligence Industry Leaders
-
Dragos, Inc.
-
Claroty Ltd.
-
Nozomi Networks Inc.
-
Forescout Technologies, Inc.
-
Waterfall Security Solutions Ltd.
- *Disclaimer: Major Players sorted in no particular order
OT Threat Intelligence Market Companies Covered in this Report
- Dragos, Inc.
- Claroty Ltd.
- Nozomi Networks Inc.
- Forescout Technologies, Inc.
- Waterfall Security Solutions Ltd.
- Radiflow Ltd.
- TXOne Networks Inc.
- Mission Secure, Inc.
- Tenable Holdings, Inc.
- Cydome Security Ltd.
- Naval Dome Ltd.
- CyberOwl Ltd.
- Applied Risk B.V.
- Rhebo GmbH
- ORDR, Inc.
- SIGA OT Solutions GmbH
- Seclab Limited
- Otorio Ltd.
- SecurityGate.io, Inc.
- Shield-IoT Ltd.
Recent Industry Developments in OT Threat Intelligence Market
- September 2026: Dragos, Inc. officially acquired runZero and NetRise following Accenture's majority investment, creating an extended OT platform with unified visibility across connected devices, networks, cloud environments, and software supply chains. runZero adds exposure management; NetRise contributes firmware-level visibility supporting NERC CIP, NIS2, and TSA compliance documentation.
- July 2026: Claroty and Frenos announced a partnership to integrate Claroty's CPS detection with Frenos's AI-native OT penetration testing platform, enabling continuous validation of the defensive posture against real-world adversarial behaviors without operational disruption.
- June 2026: Dragos launched EmberAI, an OT-native AI built on the Dragos Intelligence Fabric spanning 600+ protocols and 10-plus years of adversary tracking. EmberAI enables plain-language investigation of assets and vulnerabilities, with customer data operating entirely within the controlled Dragos Platform deployment.
- June 2026: Accenture finalized a majority investment in Dragos alongside the acquisitions of runZero and NetRise, expanding Accenture's USD 10 billion cybersecurity business into end-to-end OT security for critical infrastructure while preserving Dragos's operational independence.
Global OT Threat Intelligence Market Report Scope
The OT Threat Intelligence Market comprises revenues generated from software solutions and services that collect, analyze, contextualize, correlate, and deliver actionable cyber threat intelligence for operational technology (OT) environments, industrial control systems (ICS), critical infrastructure, and industrial IoT ecosystems. These solutions help organizations identify emerging threats, prioritize vulnerabilities, support threat hunting, improve incident response, strengthen compliance readiness, and enhance cyber resilience by providing OT-specific intelligence related to threat actors, malware campaigns, vulnerabilities, attack techniques, and industrial cyber risks.
The OT Threat Intelligence Market Report is Segmented by Component (Solutions, and Services), Deployment Mode (On-Premises, and Cloud), Application (Threat Detection and Monitoring, Vulnerability Prioritization and Exposure Management, Incident Response and Forensics, Risk, Compliance, and Audit Readiness, and Other Applications), Organization Size (Large Enterprises, and Small and Medium Enterprises), End-User Industry (Energy and Utilities, Industrial Manufacturing, Oil and Gas, Transportation and Logistics, Chemicals and Pharmaceuticals, Mining and Metals, Water and Wastewater, and Other End-User Industries), and Geography (North America, South America, Europe, Asia-Pacific, Middle East, and Africa). The Market Forecasts are Provided in Terms of Value (USD).
Segmentation Overview
| Solutions |
| Services |
| On-Premises |
| Cloud |
| Threat Detection and Monitoring |
| Vulnerability Prioritization and Exposure Management |
| Incident Response and Forensics |
| Risk, Compliance, and Audit Readiness |
| Other Applications |
| Large Enterprises |
| Small and Medium Enterprises |
| Energy and Utilities |
| Industrial Manufacturing |
| Oil and Gas |
| Transportation and Logistics |
| Chemicals and Pharmaceuticals |
| Mining and Metals |
| Water and Wastewater |
| Other End-User Industries |
| North America | United States |
| Canada | |
| South America | Brazil |
| Argentina | |
| Mexico | |
| Rest of South America | |
| Europe | Germany |
| United Kingdom | |
| France | |
| Italy | |
| Russia | |
| Rest of Europe | |
| Asia-Pacific | China |
| Japan | |
| India | |
| South Korea | |
| Rest of Asia-Pacific | |
| Middle East | Saudi Arabia |
| United Arab Emirates | |
| Rest of Middle East | |
| Africa | South Africa |
| Nigeria | |
| Rest of Africa |
| By Component | Solutions | |
| Services | ||
| By Deployment Mode | On-Premises | |
| Cloud | ||
| By Application | Threat Detection and Monitoring | |
| Vulnerability Prioritization and Exposure Management | ||
| Incident Response and Forensics | ||
| Risk, Compliance, and Audit Readiness | ||
| Other Applications | ||
| By Organization Size | Large Enterprises | |
| Small and Medium Enterprises | ||
| By End-User Industry | Energy and Utilities | |
| Industrial Manufacturing | ||
| Oil and Gas | ||
| Transportation and Logistics | ||
| Chemicals and Pharmaceuticals | ||
| Mining and Metals | ||
| Water and Wastewater | ||
| Other End-User Industries | ||
| By Geography | North America | United States |
| Canada | ||
| South America | Brazil | |
| Argentina | ||
| Mexico | ||
| Rest of South America | ||
| Europe | Germany | |
| United Kingdom | ||
| France | ||
| Italy | ||
| Russia | ||
| Rest of Europe | ||
| Asia-Pacific | China | |
| Japan | ||
| India | ||
| South Korea | ||
| Rest of Asia-Pacific | ||
| Middle East | Saudi Arabia | |
| United Arab Emirates | ||
| Rest of Middle East | ||
| Africa | South Africa | |
| Nigeria | ||
| Rest of Africa | ||
Key Questions Answered in the Report
What is the OT threat intelligence market size?
The OT threat intelligence market was valued at USD 2.30 billion in 2026 and is projected to reach USD 7.22 billion by 2032 at a 21.15% CAGR.
What is driving demand for OT threat intelligence platforms?
Attacks on critical infrastructure, IT-OT convergence, regulatory requirements, and connected industrial operations are increasing the need for contextual intelligence.
Which component holds the largest share of OT threat intelligence demand?
Solutions held 66.41% of demand in 2026 because organizations need integrated asset discovery, vulnerability context, and threat detection.
Which deployment model is growing the fastest?
Cloud deployment is projected to expand at a 22.91% CAGR through 2032, supported by managed services and lower local hardware requirements.
Which end-user sector is expanding the fastest?
Energy and utilities are projected to grow at a 21.78% CAGR through 2032 due to direct targeting risks and expanding monitoring requirements.
Which region is expected to grow the fastest?
Asia-Pacific is projected to expand at a 22.06% CAGR through 2032 as national cybersecurity frameworks and connected industrial systems develop.