
Managed Exposure Management Services Market Size and Share
Market Overview
| Study Period | 2021 - 2032 |
|---|---|
| Market Size (2027) | USD 3.69 Billion |
| Market Size (2032) | USD 7.83 Billion |
| Growth Rate (2027 - 2032) | 16.24 % |
| Fastest Growing Market | Asia-Pacific |
| Largest Market | North America |
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image © Mordor Intelligence. Reuse requires attribution under CC BY 4.0. | |
Managed Exposure Management Services Market Analysis by Mordor Intelligence
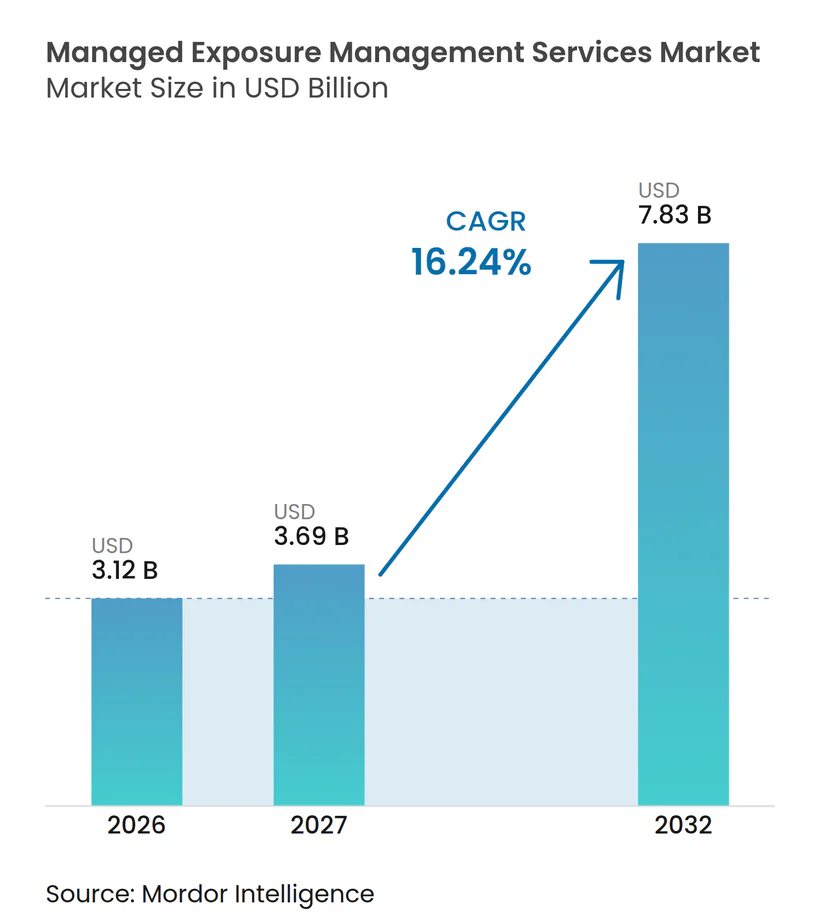
The managed exposure management services market size is projected to expand from USD 3.12 billion in 2026 to USD 3.69 billion in 2027, and to USD 7.83 billion by 2032, registering a CAGR of 16.24% from 2027 to 2032. The market is moving from annual security reviews toward provider-managed programs that identify, prioritize, and verify exposures across a changing digital environment. Broader cloud use, more SaaS connections, and complex hybrid environments make static asset inventories less useful for many enterprises. Buyers also need documented evidence of continuous security controls for insurance, regulatory, and internal governance purposes. Providers are responding by combining discovery, prioritization, and remediation workflows with advisory services, while platform vendors are exerting price pressure through bundled offerings. The managed exposure management services market, therefore, favors providers that can connect security findings to practical remediation across a client’s existing tools.
Key Report Takeaways
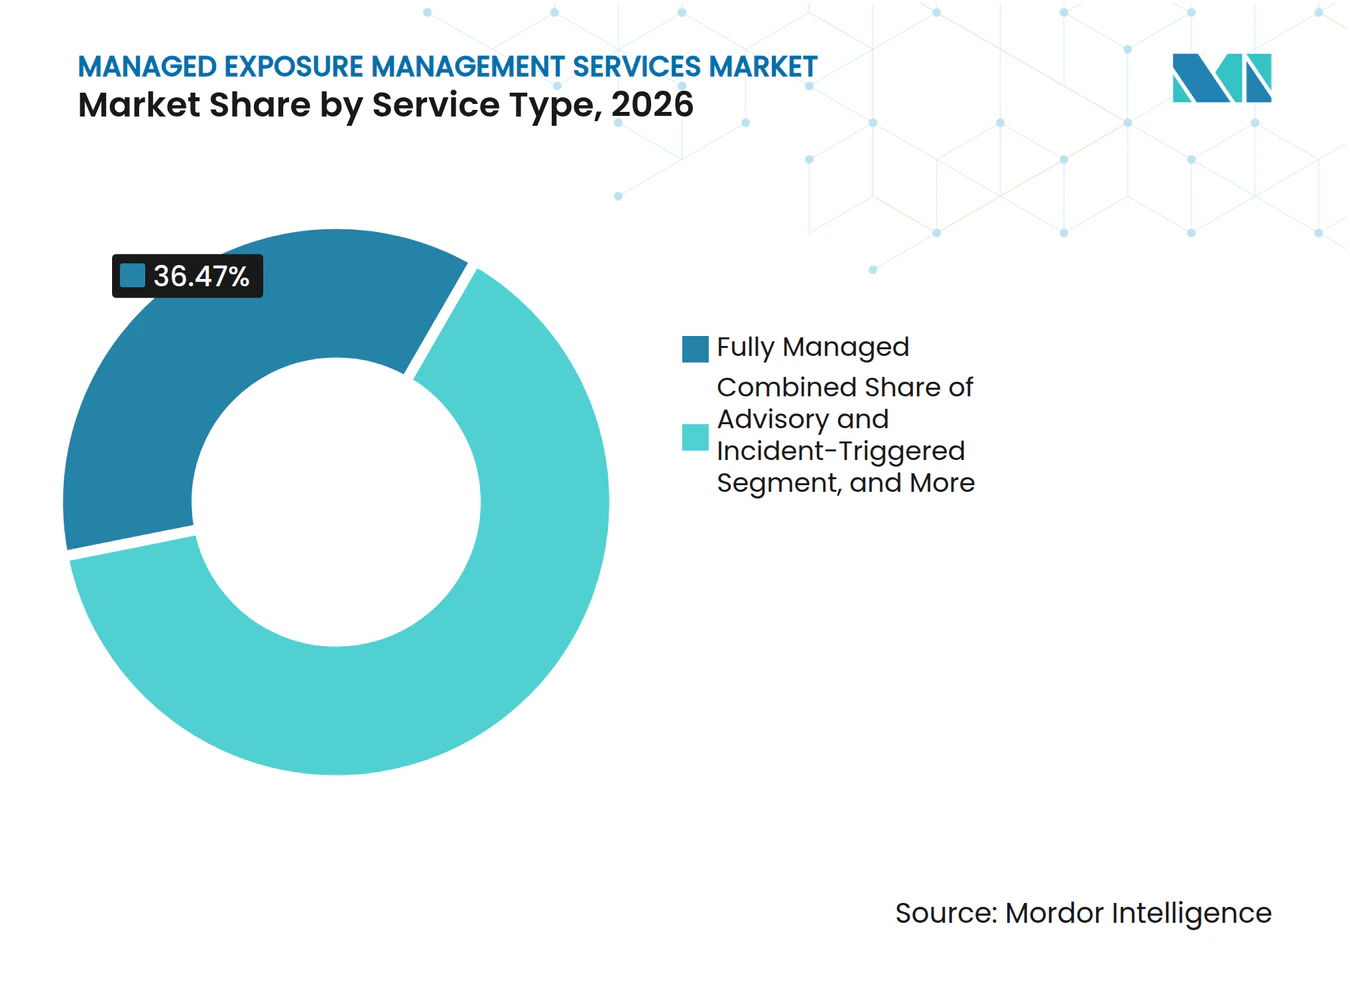
- By service type, Fully Managed held 36.47% of the Managed exposure management services market share in 2026, while Co-Managed services are projected to expand at a 17.53% CAGR through 2032.
- By application, Vulnerability and Exposure Management accounted for 31.83% of the Managed exposure management services market size in 2026, while Remediation Orchestration and Verification is projected to grow at a 16.82% CAGR through 2032.
- By deployment model, Cloud-Based deployment held 62.17% of market share in 2026, while Hybrid deployment is expected to grow at a 17.03% CAGR through 2032.
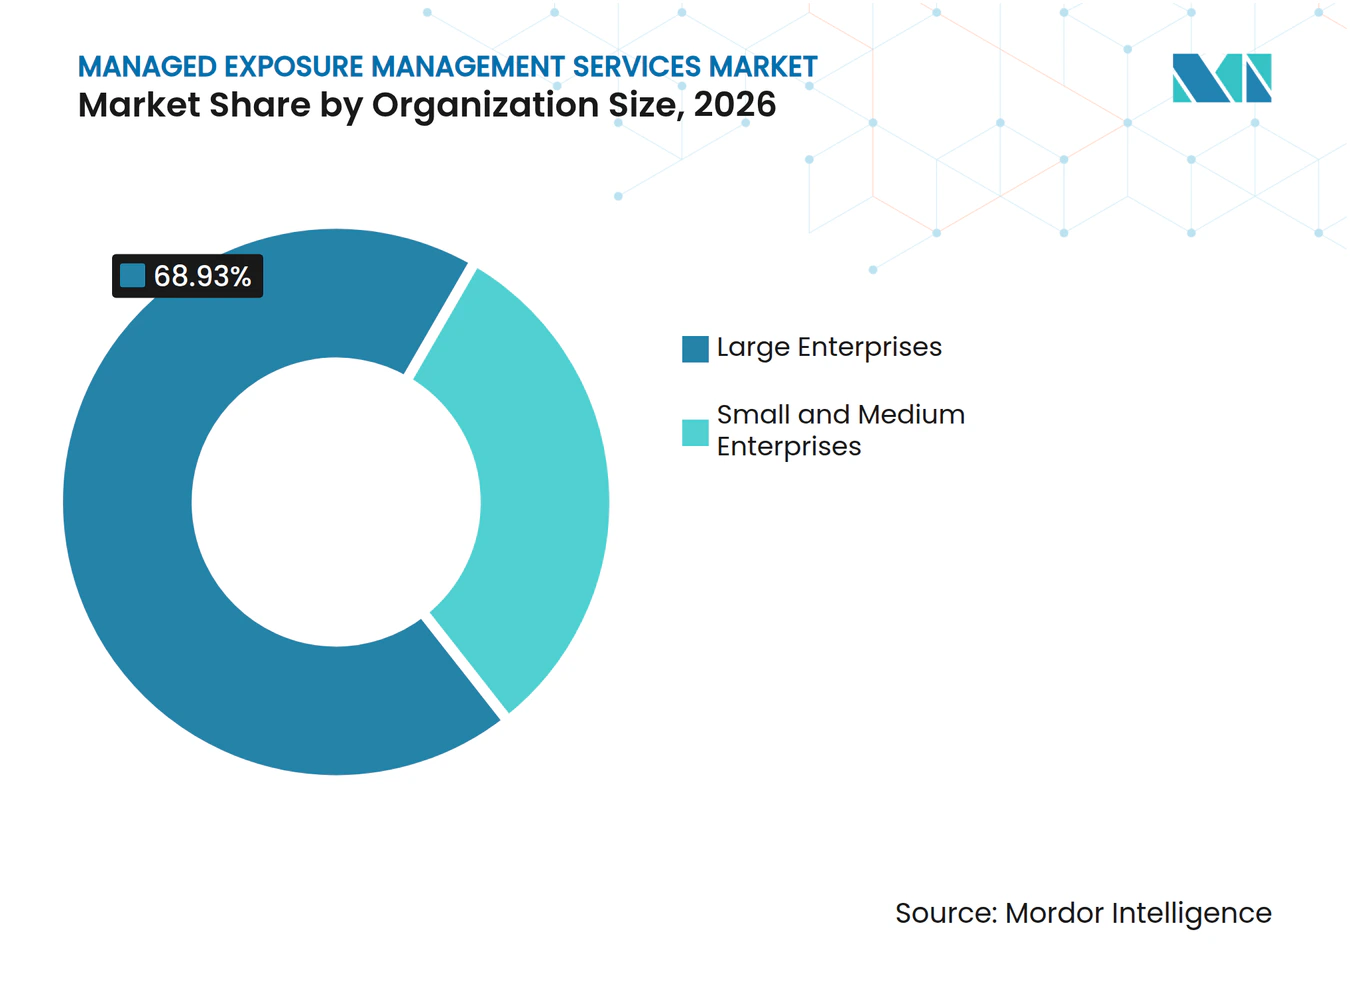
- By organization size, Large Enterprises held 68.93% of market share in 2026, while Small and Medium Enterprises are projected to expand at a 17.26% CAGR through 2032.
- By end-user industry, BFSI accounted for 24.63% of market share in 2026, while Healthcare is expected to advance at a 17.43% CAGR through 2032.
- By geography, North America held 40.27% of global revenue in 2026, while Asia-Pacific is projected to grow at a 17.32% CAGR through 2032.
Note: Market numbers in this report are based on Mordor Intelligence's proprietary estimation framework, which combines nine months of actuals with Q4 projections for base year 2026.
Global Managed Exposure Management Services Market Trends and Insights
Drivers Impact Analysis*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Escalating Cyberattacks and Internet-Facing Asset Exploitation | +3.5% | Global, with concentrated pressure in North America, Europe, and Asia-Pacific | Short term (≤ 2 years) |
| Expansion of Cloud, SaaS, and Hybrid Digital Footprints | +3.2% | Global, most pronounced in North America, Western Europe, and Asia-Pacific urban centers | Medium term (2-4 years) |
| Cybersecurity Skills Shortages and Outsourcing Demand | +2.8% | Global, most acute in North America, Australia, United Kingdom, and India | Medium term (2-4 years) |
| Regulatory Demand for Continuous Exposure Evidence | +2.5% | Europe, North America, Asia-Pacific, with spillover to the Middle East | Medium term (2-4 years) |
| Cyber Insurance and Contractual Exposure-Evidence Requirements | +1.8% | North America and Europe, with emerging relevance in Asia-Pacific | Short term (≤ 2 years) |
| Exposure Inheritance From Mergers, Acquisitions, and Third-Party Connections | +1.4% | Global, with concentration in North America and Europe | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Escalating Cyberattacks and Exploitation of Internet-Facing Assets
Internet-facing assets remain a common entry point for threat actors, which increases the value of continuous external discovery for organizations that cannot rely on a fixed inventory. CISA directs federal civilian agencies to conduct regular credentialed vulnerability scanning and maintain processes for identifying and prioritizing internet-accessible assets. The Managed exposure management services market benefits when enterprises apply similar expectations to their external asset inventory and require an ongoing process rather than an isolated technical exercise. Continuous provider-led monitoring can identify assets that are not visible to internal teams, assign ownership of the exposure, and keep security teams focused on remediation.
Expansion of Cloud, SaaS, and Hybrid Digital Footprints
Hybrid and multi-cloud operations are widening the environment that security teams must track, often across different providers, identities, and operating groups. Fortinet reported that 88% of organizations operated hybrid or multi-cloud environments in 2026, compared with 82% in the prior year. The same report found that 81% relied on 2 or more cloud providers for critical workloads, and 29% used more than 3, increasing the number of settings and connections requiring review. The Cloud Security Alliance found that 55% of employees adopted SaaS tools without security involvement, while 56% reported concern over excessive API access.[1] These conditions cause inventories built through periodic scans to age quickly, making it harder for internal teams to establish a complete view of risk. The Managed exposure management services market is gaining demand because continuous discovery can track changes in cloud configurations, SaaS use, identities, and externally exposed services through a single managed process.
Cybersecurity Skills Shortages and Outsourcing Demand
The cybersecurity skills gap is influencing how buyers choose between internal operations and managed services, particularly when exposure management requires both technical depth and cross-functional coordination. ISC2 reported that 95% of organizations had at least 1 cybersecurity skill needed in 2025. The need is not limited to staffing levels; organizations also require practitioners who can prioritize findings, assess business relevance, and manage remediation across teams. The managed exposure management services market gives buyers access to shared specialist capacity without building a complete internal exposure management function for every hour of the day. Managed providers can also spread the cost of alert triage and initial investigation tools across multiple clients, thereby improving the economics of continuous service delivery. This structure can be particularly relevant for organizations that need continuous coverage but cannot sustain a large in-house team or develop every required specialty internally.
Regulatory Demand for Continuous Exposure Evidence
Regulation is becoming a direct procurement consideration for financial institutions, critical infrastructure operators, and listed companies that need to demonstrate consistent cyber risk management. The EU Digital Operational Resilience Act took effect on January 17, 2025, and requires covered financial entities to maintain ICT risk management arrangements and test digital operational resilience. NIS2 establishes cybersecurity risk management and reporting duties for essential entities across critical sectors. In the United States, the SEC rule requires public companies to disclose material cybersecurity incidents and describe processes for assessing and managing cyber risk. These obligations increase the importance of records that show how exposures were identified, assigned, addressed, and monitored over time by accountable people. The managed exposure management services market is supported when providers can supply reporting and operational evidence alongside technical monitoring, rather than leaving the customer to assemble evidence from separate systems.
Restraints Impact Analysis*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Integration Friction Across Security and IT Toolchains | -3.0% | Global, most severe in large enterprises with heterogeneous tooling estates in North America and Europe | Medium term (2-4 years) |
| High Implementation Complexity and Specialist-Cost Burden | -2.5% | Global, most pronounced in emerging markets, mid-market segments, and regions with lower MSSP density | Medium term (2-4 years) |
| Data Residency, Authorization, and Safe-Scanning Constraints | -1.8% | Europe, Asia-Pacific, the Middle East, and government and defense organizations globally | Long term (≥ 4 years) |
| Unclear Asset Ownership and Remediation Accountability | -1.5% | Global, most acute in large decentralized enterprises | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Integration Friction Across Security and IT Toolchains
Integration is a practical barrier because exposure management must connect discovery, prioritization, and remediation across separate security and IT systems that often have different data structures and processes. Large enterprises rarely start with a clean environment, so providers must work with varied asset names, workflows, escalation rules, and different teams that may not use the same systems. The handoff from security teams to IT operations and application owners can delay remediation even when a risk is identified quickly and technically understood. These requirements can extend onboarding, consume buyer technical resources, and make early value harder to demonstrate.
High Implementation Complexity and Specialist-Cost Burden
The cost of a managed exposure program goes beyond a service subscription, as buyers must prepare the environment and maintain the operating model after launch. Buyers must also account for scoping, discovery calibration, remediation workflow design, continuing analyst involvement, and the time that internal teams spend providing asset context. Censinet reported that healthcare organizations typically allocated 4%-7% of IT budgets to cybersecurity, compared with 15% in financial services. This difference can limit adoption even when healthcare organizations recognize their exposure and want more consistent monitoring. Legacy systems can create more work because some environments require on-premises discovery agents, specialized configuration, and coordination with teams responsible for aging applications or devices. Providers also need demonstrated sector expertise, especially in healthcare, financial services, and government, which can lengthen buyer evaluations and implementation timelines.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Segment Analysis
By Service Type: Co-Managed Models Expand Buyer Control
Fully managed services held 36.47% of the managed exposure management services market share in 2026. This position reflects buyer demand for a provider that assumes responsibility for discovery, prioritization, remediation coordination, and remediation validation within a single operating model. Large regulated organizations often prefer this model because it reduces the operational load on internal security teams, which would otherwise need to operate scanners, interpret findings, and coordinate work across multiple owners. It can also create a documented record of continuous security activity for audit, insurance, and executive oversight reviews, rather than leaving a buyer with separate technical outputs from disconnected tools. The managed exposure management services industry uses this model, where clients need broad operational support, clear service accountability, and a consistent process for escalating exposures that require action.
Co-Managed services are projected to grow at a 17.53% CAGR from 2027 to 2032. These services allow buyers to retain authority over remediation decisions while outsourcing discovery, scanning, and prioritization, as well as the recurring operational effort of keeping exposure data current. The approach suits enterprises that have developed stronger internal governance and understand their business priorities but do not want to operate every technical process or maintain specialist coverage at all times. Monitoring-Only and Advisory and Incident-Triggered offerings meet more limited needs, including insurance renewal, acquisition due diligence, regulatory audits, and focused support after a significant event. As automation lowers the cost of continuous discovery, providers may face pressure to distinguish basic monitoring from more valuable remediation coordination, evidence collection, and advisory work.



By Application: Remediation Verification Becomes More Important
Vulnerability and Exposure Management accounted for 31.83% of the managed exposure management services market size in 2026. The segment is based on continuous scanning and prioritization across enterprise assets, including the external services, cloud resources, and known systems that make up an organization’s digital environment. Buyers increasingly expect analysis of findings rather than a large volume of raw scanner results, as technical teams need a workable order to address risks. Risk and Compliance Management, Threat Intelligence, and Digital Risk Protection extend the core vulnerability program by linking exposure information with broader operational and governance needs. Asset Discovery and Inventory also support every application, because organizations cannot protect services that are absent from their records or lack an assigned owner.
Remediation Orchestration and Verification is projected to expand at a 16.82% CAGR from 2027 to 2032. Its growth shows that buyers need confirmation that remediation took place, that it was assigned to the correct team, and that the action resolved the exposure. This work connects security operations with IT operations, where remediation tasks are completed and where delays can arise from competing business priorities or unclear responsibility. Accenture and CrowdStrike stated in March 2025 that their collaboration could deliver up to 15% cost optimization in vulnerability management workflows through consolidated exposure visibility and attack-path analysis.[2] The Managed exposure management services industry is therefore placing greater value on services that close the gap between a detected issue, a planned response, and verified resolution.
By Deployment Model: Hybrid Architectures Address Data Constraints
Cloud-based deployment accounted for 62.17% of the managed exposure management services market share in 2026. Cloud delivery supports continuous external discovery across multi-cloud environments and enables providers to update detection content without extensive client-side changes, reducing the need for separate update cycles for each customer. It also fits the wider move toward software-as-a-service security operations, where teams need accessible reporting and shared workflows across locations. Cloud-Based services are useful when clients need scalability across changing assets, locations, and connected services that may not be present during a traditional internal review. However, not every client can move raw security data outside its own environment, particularly when legal, contractual, or government requirements restrict data handling.
Hybrid deployment is projected to grow at a 17.03% CAGR from 2027 to 2032. The model combines local data collection with cloud-based analytics and workflow management, allowing providers to apply centralized analysis while preserving closer control over sensitive information. It can help organizations retain sensitive data in their environment while still using provider-operated analytics, reporting, and remediation coordination. Government agencies, defense contractors, and financial institutions may favor this model where data residency rules are strict or internal policy limits external data transfers.
By Organization Size: Subscription Delivery Broadens SME Access
Large Enterprises held 68.93% of the market share in 2026. Their scale, broader asset base, obligations across multiple jurisdictions, and dependence on numerous business systems make continuous exposure management a priority. These buyers often have established relationships with managed security providers, but their internal environments can still be difficult to coordinate across business units and technology teams. They also face ongoing difficulty hiring the analysts needed to run mature exposure programs internally and to maintain specialist expertise across discovery, prioritization, and verification.
Small and Medium Enterprises are expected to grow at a 17.26% CAGR from 2027 to 2032. Subscription-based services shift the purchasing model from large upfront spending to more predictable operating costs, which better fit the budgeting process and limited staffing of smaller organizations. This can make continuous discovery and prioritization more accessible to organizations with smaller security teams that cannot independently maintain every specialist capability. Outsourced monitoring also allows internal teams to focus on decisions, remediation coordination, and business operations rather than the repetitive task of reviewing large volumes of technical findings. Insurance requirements for scanning records, patch management, and incident response plans can provide an additional reason for smaller organizations to adopt managed services.

By End-User Industry: Healthcare Demand Rises With Security Pressure
BFSI accounted for 24.63% of the market share in 2026. Financial institutions work under demanding cyber-risk and operational resilience requirements because they manage sensitive customer data, critical payment processes, and large networks of third-party providers. DORA in Europe, the SEC disclosure rule in the United States, and other sector frameworks reinforce the need for continuous visibility, clear reporting, and evidence that material issues receive attention. The managed exposure management services industry serves this need by linking identification, prioritization, remediation tracking, and governance records.
Healthcare is projected to grow at a 17.43% CAGR from 2027 to 2032. The sector must manage aging clinical devices, complex care networks, and security risks that can affect patient care, while many organizations operate with limited resources for specialized security work. A Federal Reserve study noted that cyber events involving third-party providers can cause greater losses than routine incidents at large U.S. financial institutions, underscoring the broader importance of supplier risk oversight. In 2026, ARPA-H supported a hospital-scale digital twin project focused on vulnerability detection and remediation across medical devices. Government and Defense, Manufacturing, Information Technology and Telecommunications, Retail and E-Commerce, Energy and Utilities, and Education also have growing requirements for formal exposure management.
Geography Analysis
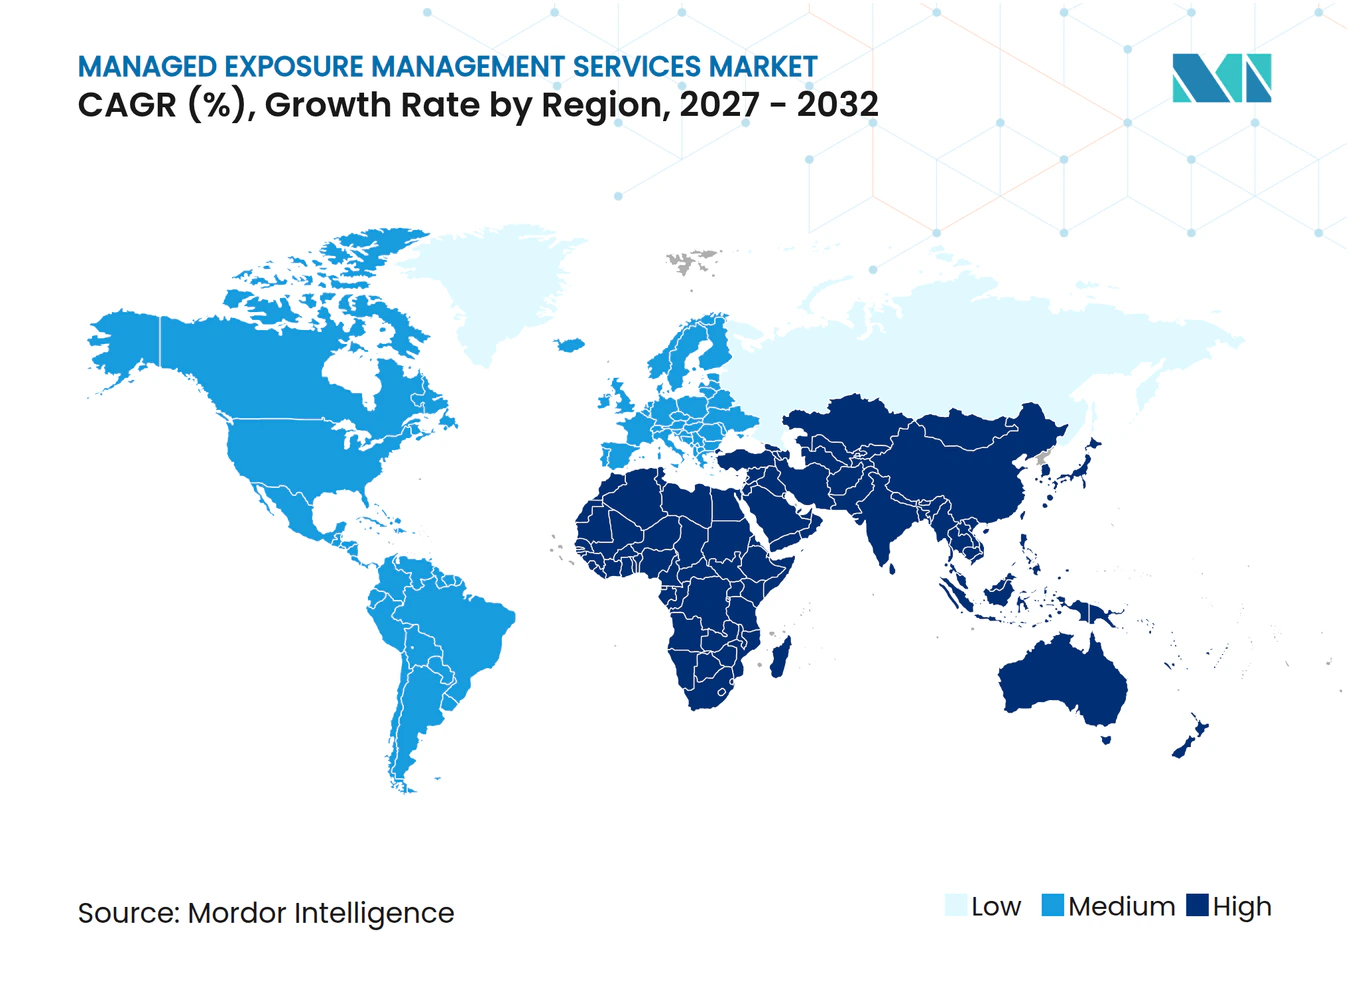
North America held 40.27% of the managed exposure management services market revenue in 2026. The region has a mature managed security provider ecosystem, sophisticated enterprise security procurement, and many organizations that already use specialized security tools and external service partners. Financial services and healthcare organizations face several federal, state, and sector-specific obligations that encourage more formal risk oversight and regular reviews of technical controls. The SEC rule requires public companies to report material cyber incidents and to describe their cyber risk management processes. The United States leads regional revenue, while Canada is expanding managed security programs among financial institutions and critical infrastructure operators that need clear evidence of risk management.
Europe holds a significant share of global revenue, supported by the implementation of DORA and NIS2. DORA applies to financial entities and requires digital operational resilience arrangements, while NIS2 extends risk-management requirements to essential and important entities in critical sectors. Germany, the United Kingdom, and France remain important markets because they have major financial institutions, defense contractors, and multinational organizations with cross-border operating needs. The Bank of England identified gaps in proactive detection, credentials management, and risk-based remediation planning in its 2025 CBEST thematic work.[3] These conditions support the Managed exposure management services market by increasing demand for services that provide ongoing exposure evidence and clearly documented work.
Asia-Pacific is projected to grow at a 17.32% CAGR from 2027 to 2032. Rapid cloud adoption, rising threat levels, and limited specialist capacity support outsourced delivery in the region, especially where enterprises need continuous operations but cannot expand internal security teams at the same pace. India is an important growth market, while Japan is building local capacity through domestic managed attack surface and vulnerability management offerings, including NTT East’s BizDrive ASM in August 2025 and Uniadex’s Tenable One-based service in April 2026. South America, the Middle East, and Africa remain earlier-stage markets, with demand developing through financial-services digitization, cloud adoption, and stronger national cybersecurity requirements.
Competitive Landscape
Market Concentration
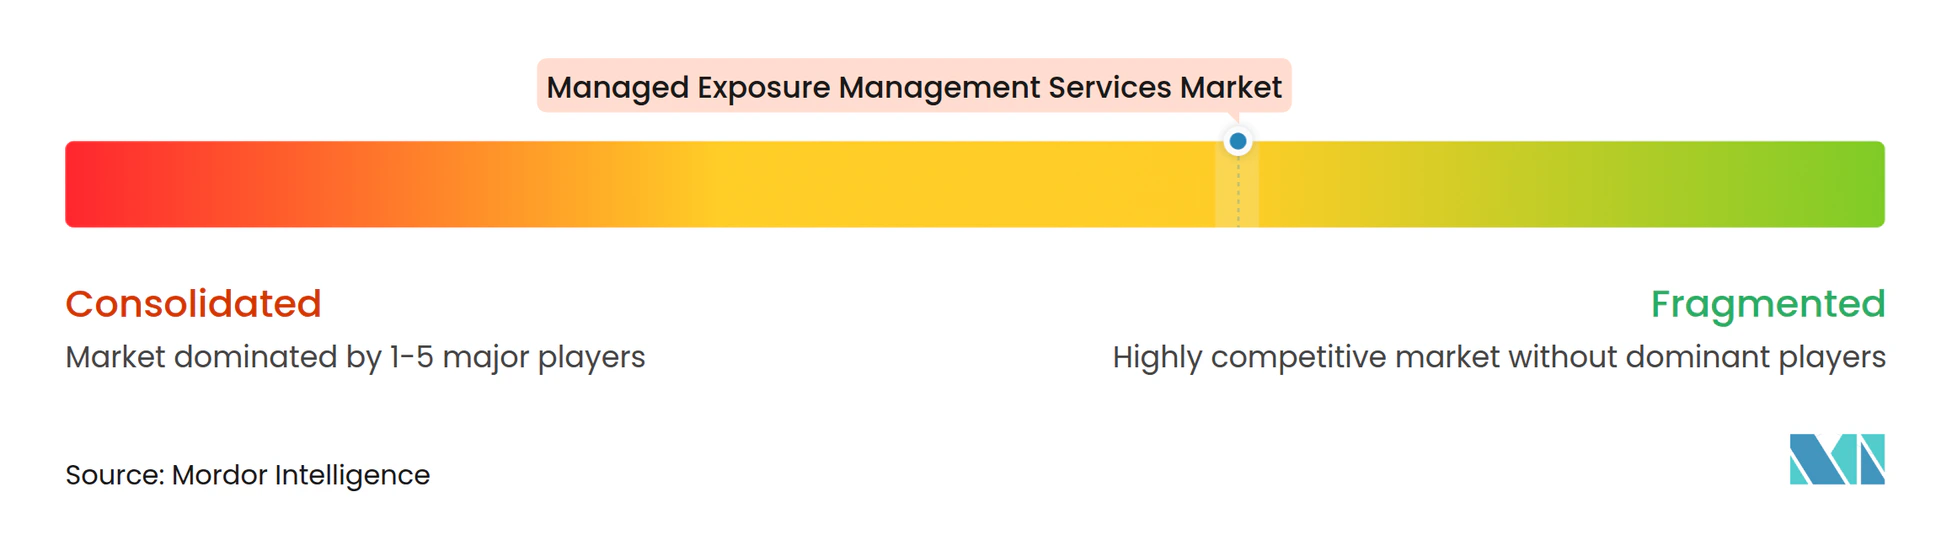
The managed exposure management services market is moderately fragmented, and no provider holds a dominant position. Competition involves global consultancies, established vulnerability platform vendors, and specialist attack surface management providers, each of which approaches the buyer through a different combination of services and technology. Global consultancies can connect exposure management with broader transformation work, while platform vendors can extend tools customers already use, and specialists can emphasize the depth of external discovery. Accenture, Deloitte, IBM, and Kyndryl compete by offering broad security transformation programs and sector-specific compliance expertise that can be bundled into larger client engagements. Tenable, Qualys, and Rapid7 build on platform relationships and scanner data to add managed delivery capabilities for existing customers.
Platform vendors are adding integrations to translate findings into remediation workflows across different client tools, reflecting the need to integrate with existing customer operating environments. Tenable expanded its open security ecosystem in October 2026 with connectors to SentinelOne, Corelight, Snyk, and BeyondTrust. This move connects exposure data with network telemetry, identity context, and code-level findings so that teams can use more related information when prioritizing a response. Accenture and AttackIQ announced a February 2026 partnership to combine breach and attack simulation, AI-driven prioritization, and security operations modernization.[4] These moves show that the Managed exposure management services market increasingly rewards providers that support both technical discovery and the operational response that follows.
Providers also have room to serve operational technology and industrial Internet of Things environments, where many programs remain focused on conventional IT assets and may not yet cover the full range of connected systems. ISO 27001 and SOC 2 Type II certifications are increasingly important in enterprise evaluations and can favor established providers that can demonstrate mature security and governance practices. Pricing pressure is rising as platform vendors bundle managed capabilities into current technology contracts, which requires pure-play providers to show value through sector expertise, external discovery depth, and verified remediation results.
Managed Exposure Management Services Industry Leaders
-
Accenture plc
-
Armis, Inc.
-
BitSight Technologies, Inc.
-
Cisco Systems, Inc.
-
CrowdStrike Holdings, Inc.
- *Disclaimer: Major Players sorted in no particular order
Recent Industry Developments
- October 2026: Tenable expanded its open security ecosystem, launching cross-platform connectors to SentinelOne, Corelight, Snyk, and BeyondTrust through its Tenable OPEN program. The connectors integrate Tenable's exposure data with network telemetry, identity context, and code-level vulnerability findings, enabling unified triage from a single AI-assisted interface and extending the Tenable One platform's value beyond standalone scanner deployments. This positions Tenable to compete more directly with platform-consolidation strategies from CrowdStrike and Microsoft in the managed exposure segment.
- February 2026: Armis achieved U.S. Department of Defense Impact Level 5 authorization from DISA, enabling it to manage and secure DoD critical infrastructure and Controlled Unclassified Information systems via its Armis Centrix platform. This followed earlier FedRAMP Moderate and IL4 authorizations and opened the U.S. government and defense vertical to Armis's asset-intelligence and vulnerability management platform.
- February 2026: Accenture and AttackIQ announced a partnership to accelerate security operations modernization, integrating AttackIQ's breach and attack simulation and AI-driven control validation capabilities into Accenture's global SOC modernization services. The collaboration included a future roadmap for continuous threat exposure management programs aligned to the CTEM framework, with plans to unify adversarial testing, telemetry aggregation, and exposure prioritization across client environments.
- March 2025: Accenture and CrowdStrike announced a strategic collaboration to transform security operations for enterprise clients, combining the CrowdStrike Falcon platform with Accenture's managed security services. The continuous threat exposure management component of the collaboration was cited as capable of achieving up to 15% cost optimization by consolidating exposure visibility across the extended attack surface and streamlining prioritization using attack path analysis, with the first client deployment referencing WHSmith's global security operations modernization.
Global Managed Exposure Management Services Market Report Scope
Managed exposure management services help organizations identify, assess, prioritize, and remediate cybersecurity vulnerabilities and exposures across their digital attack surface. These services combine continuous monitoring, threat intelligence, risk assessment, and remediation guidance to improve an organization’s security posture.
The Managed Exposure Management Services Market Report is Segmented by Service Type (Fully Managed, Co-Managed, Monitoring-Only, and Advisory and Incident-Triggered), Application (Asset Discovery and Inventory, Risk and Compliance Management, Vulnerability and Exposure Management, Threat Intelligence and Digital Risk Protection, and Remediation Orchestration and Verification), Deployment Model (On-Premises, Cloud-Based, and Hybrid), Organization Size (Small and Medium Enterprises and Large Enterprises), End-User Industry (Information Technology and Telecommunications, BFSI, Healthcare, Retail and E-Commerce, Manufacturing, Government and Defense, Education, Energy and Utilities, Transportation and Logistics, Hospitality and Travel, and Other End-User Industries), and Geography (North America, South America, Europe, Asia-Pacific, Middle East, and Africa). The Market Forecasts are Provided in Terms of Value (USD).
| Fully Managed |
| Co-Managed |
| Monitoring-Only |
| Advisory and Incident-Triggered |
| Asset Discovery and Inventory |
| Risk and Compliance Management |
| Vulnerability and Exposure Management |
| Threat Intelligence and Digital Risk Protection |
| Remediation Orchestration and Verification |
| On-Premises |
| Cloud-Based |
| Hybrid |
| Small and Medium Enterprises |
| Large Enterprises |
| Information Technology and Telecommunications |
| BFSI |
| Healthcare |
| Retail and E-Commerce |
| Manufacturing |
| Government and Defense |
| Other End-User Industries |
| North America | United States |
| Canada | |
| Mexico | |
| South America | Brazil |
| Argentina | |
| Rest of South America | |
| Europe | Germany |
| United Kingdom | |
| France | |
| Italy | |
| Spain | |
| Russia | |
| Rest of Europe | |
| Asia-Pacific | China |
| India | |
| Japan | |
| South Korea | |
| Australia | |
| Rest of Asia-Pacific | |
| Middle East | Saudi Arabia |
| United Arab Emirates | |
| Turkey | |
| Rest of Middle East | |
| Africa | South Africa |
| Egypt | |
| Nigeria | |
| Rest of Africa |
| By Service Type | Fully Managed | |
| Co-Managed | ||
| Monitoring-Only | ||
| Advisory and Incident-Triggered | ||
| By Application | Asset Discovery and Inventory | |
| Risk and Compliance Management | ||
| Vulnerability and Exposure Management | ||
| Threat Intelligence and Digital Risk Protection | ||
| Remediation Orchestration and Verification | ||
| By Deployment Model | On-Premises | |
| Cloud-Based | ||
| Hybrid | ||
| By Organization Size | Small and Medium Enterprises | |
| Large Enterprises | ||
| By End-User Industry | Information Technology and Telecommunications | |
| BFSI | ||
| Healthcare | ||
| Retail and E-Commerce | ||
| Manufacturing | ||
| Government and Defense | ||
| Other End-User Industries | ||
| By Geography | North America | United States |
| Canada | ||
| Mexico | ||
| South America | Brazil | |
| Argentina | ||
| Rest of South America | ||
| Europe | Germany | |
| United Kingdom | ||
| France | ||
| Italy | ||
| Spain | ||
| Russia | ||
| Rest of Europe | ||
| Asia-Pacific | China | |
| India | ||
| Japan | ||
| South Korea | ||
| Australia | ||
| Rest of Asia-Pacific | ||
| Middle East | Saudi Arabia | |
| United Arab Emirates | ||
| Turkey | ||
| Rest of Middle East | ||
| Africa | South Africa | |
| Egypt | ||
| Nigeria | ||
| Rest of Africa | ||
Key Questions Answered in the Report
What is the size of the Managed exposure management services market?
The Managed exposure management services market is projected to increase from USD 3.12 billion in 2026 and USD 3.69 billion in 2027 to USD 7.83 billion by 2032, at a 16.24% CAGR.
What is driving demand for managed exposure management services?
The Managed exposure management services market is supported by expanding cloud, SaaS, and hybrid environments, which make static asset inventories less useful.
Which service type has the largest share?
Fully Managed services held 36.47% share in 2026, while Co-Managed services are projected to grow faster at a 17.53% CAGR through 2032.
Which deployment model leads adoption?
Cloud-Based deployment held 62.17% share in 2026, supported by the need to monitor distributed digital environments.
Which end-user sector is growing fastest?
Healthcare is expected to grow at a 17.43% CAGR through 2032, driven by medical-device exposure, legacy systems, and the need to protect care delivery.