
IoT Certificate Lifecycle Management Market Size and Share
Market Overview
| Study Period | 2021 - 2032 |
|---|---|
| Market Size (2027) | USD 1.91 Billion |
| Market Size (2032) | USD 3.64 Billion |
| Growth Rate (2027 - 2032) | 13.77 % |
| Fastest Growing Market | Asia-Pacific |
| Largest Market | North America |
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image © Mordor Intelligence. Reuse requires attribution under CC BY 4.0. | |
IoT Certificate Lifecycle Management Market Analysis by Mordor Intelligence
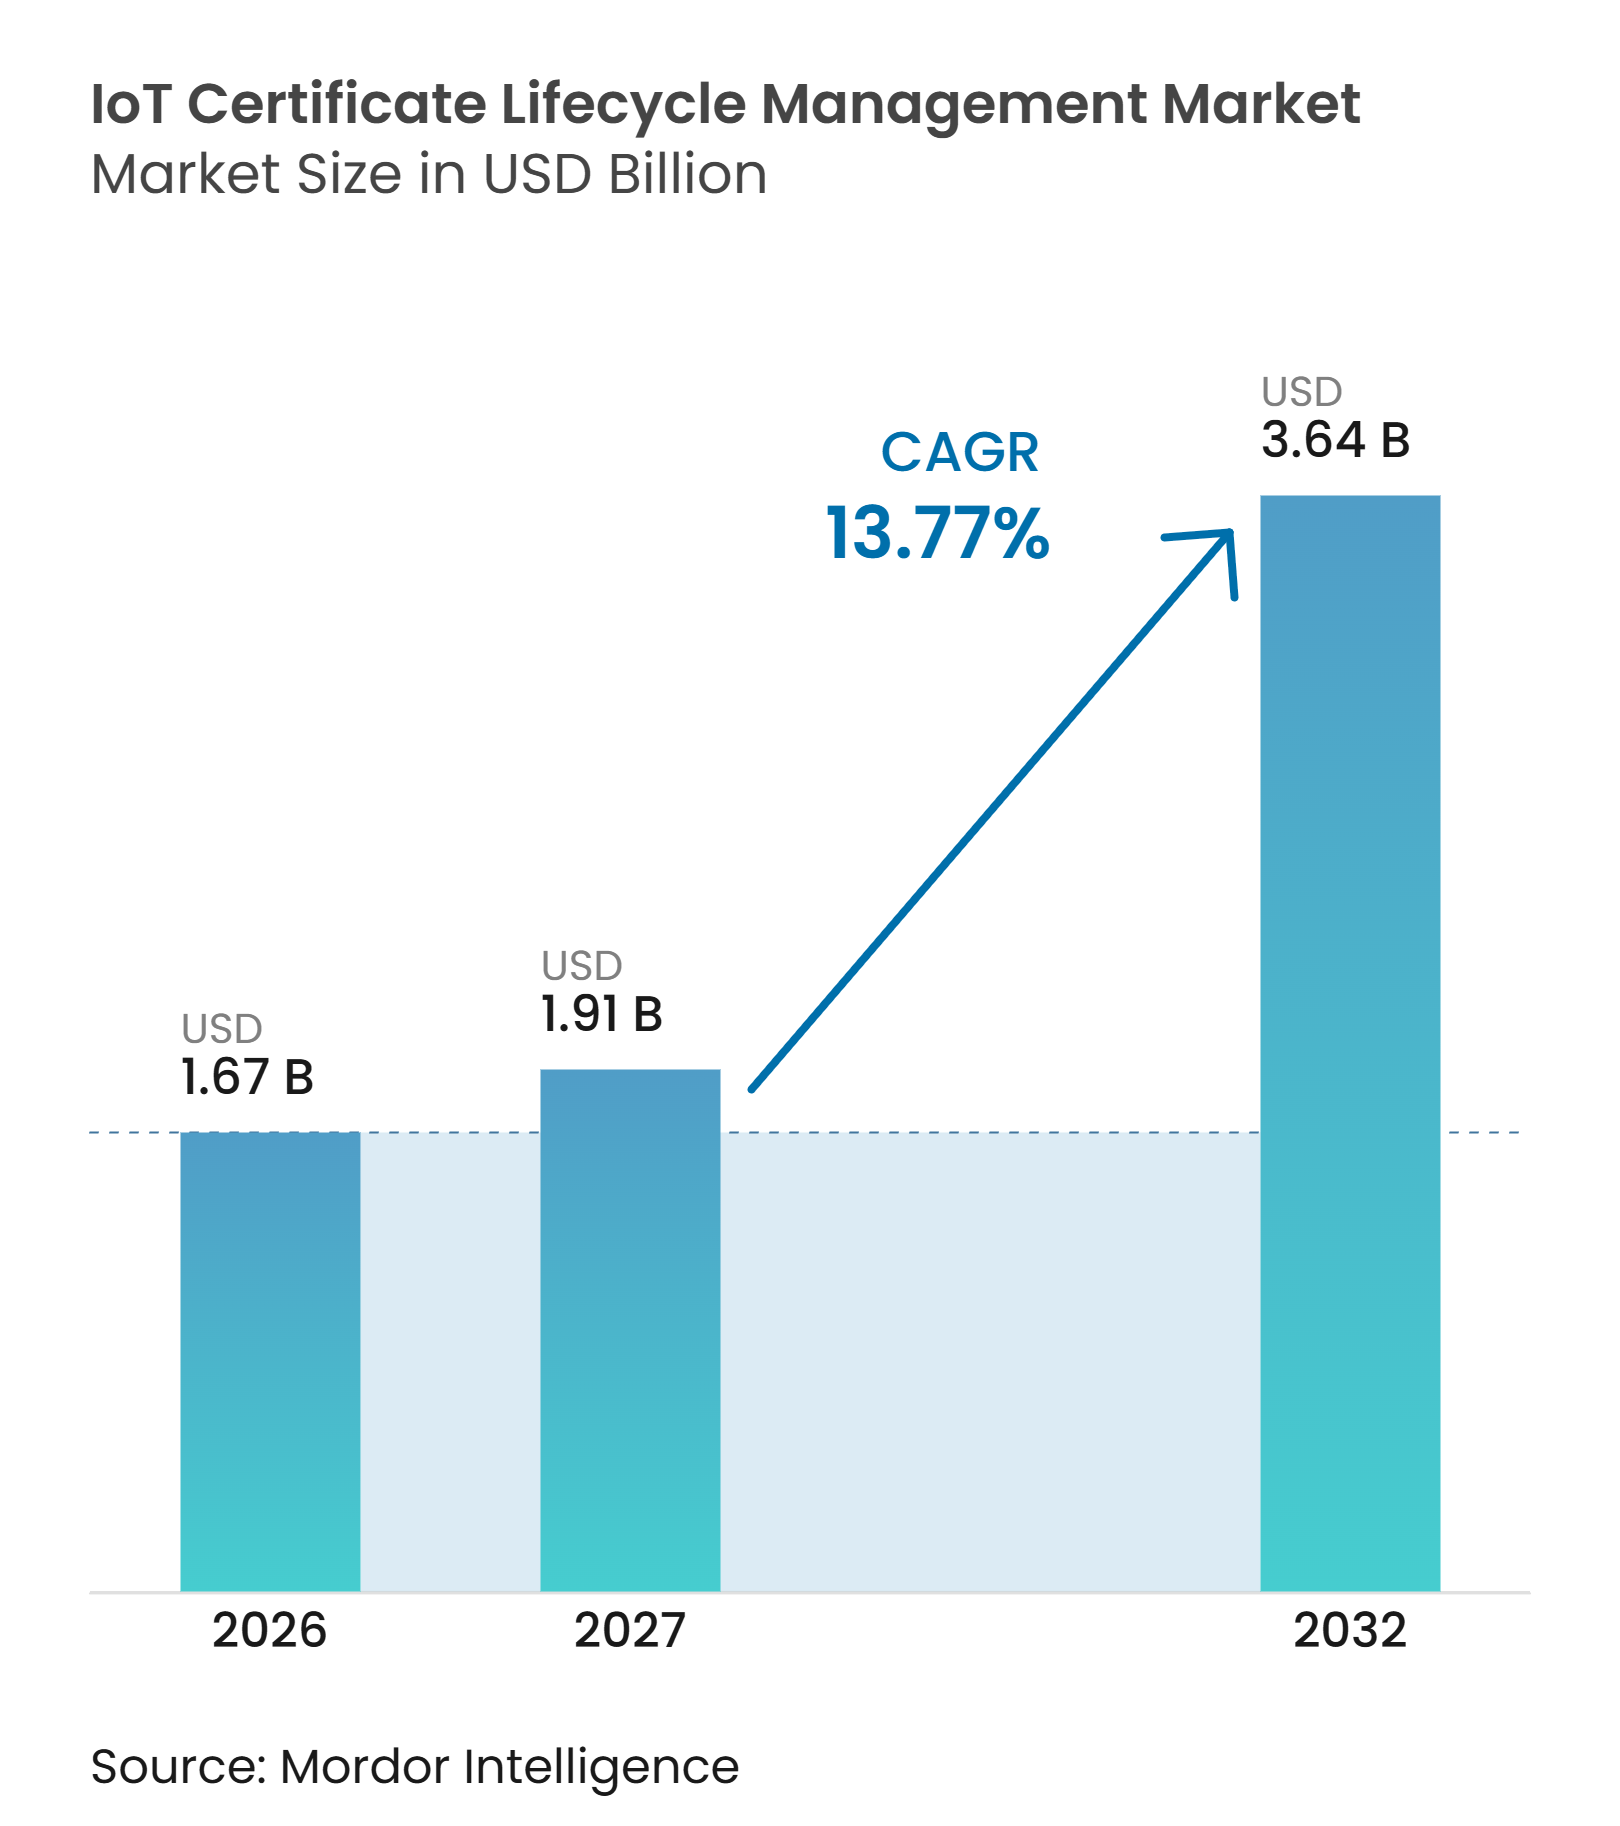
The IoT certificate lifecycle management market size is projected to be USD 1.67 billion in 2026, USD 1.91 billion in 2027, and reach USD 3.64 billion by 2032, growing at a CAGR of 13.77% from 2027 to 2032. The IoT certificate lifecycle management market is being shaped by larger connected fleets that require cryptographic identities that can be issued, renewed, and revoked under documented controls. Device variety also matters because mixed fleets use different enrollment methods, including EST, SCEP, CMPv2, and ACME, which makes manual administration difficult. Regulation is moving certificate automation closer to product design, especially where manufacturers must support secure updates and vulnerability handling throughout a device's life. Vendors are responding by combining certificate issuance, policy controls, discovery, and automation into a single platform. The IoT certificate lifecycle management market also has room for services because many organizations lack staff with PKI, operational technology, and embedded-security experience.
Key Report Takeaways
- By component, software held 63.42% of the IoT certificate lifecycle management market share in 2026, while managed and professional services are projected to expand at a 15.71% CAGR through 2032.
- By deployment, cloud-based systems accounted for 67.84% of the IoT certificate lifecycle management market size in 2026 and are projected to expand at a 16.23% CAGR through 2032.
- By organization size, large enterprises held 68.72% of the market in 2026, while small and medium-sized enterprises are expected to expand at a 17.91% CAGR through 2032.
- By application, device authentication accounted for 28.92% of the market in 2026, while secure boot and hardware attestation are projected to advance at a 16.51% CAGR through 2032.
- By device type, sensors and actuators accounted for 33.71% of the IoT certificate lifecycle management market in 2026, while connected vehicles and roadside units are projected to expand at a 16.72% CAGR through 2032.
- By end-user industry, manufacturing accounted for 26.54% of the market in 2026, while transportation and logistics are expected to expand at a 16.51% CAGR through 2032.
- By geography, North America held 34.66% of the market in 2026 in the IoT certificate lifecycle management market , while Asia-Pacific is projected to expand at a 17.52% CAGR through 2032.
Note: Market numbers in this report are based on Mordor Intelligence's proprietary estimation framework, which combines nine months of actuals with Q4 projections for base year 2026.
Global IoT Certificate Lifecycle Management Market Trends and Insights
Drivers Impact Analysis*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Connected Device Proliferation and Machine Identity Expansion | +3.2% | Global | Medium term (2-4 years) |
| Regulatory Pressure for Security by Design and Lifecycle Support | +2.8% | Global, early intensity in Europe, North America, and Asia-Pacific | Short term (≤ 2 years) |
| Industrial Operational Technology and Critical Infrastructure Modernization | +2.1% | North America, Europe, and Asia-Pacific | Medium term (2-4 years) |
| Cloud, Edge, and Zero-Trust Architecture Adoption | +1.9% | Global, concentrated in North America and Europe | Medium term (2-4 years) |
| Certificate Expiration Risk Across Long-Lived Device Fleets | +1.4% | Global | Short term (≤ 2 years) |
| Post-Quantum Crypto-Agility Planning for Embedded Devices | +1.1% | North America and Europe | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Connected Device Proliferation and Machine Identity Expansion
Connected device fleets are creating a larger administrative workload for certificate teams. Each endpoint requires an identity that can be enrolled, renewed, monitored, and revoked through its operating life. A large fleet also includes different hardware classes and operating environments, which requires support for more than one enrollment protocol. Therefore, certificate operations increase with both device count and fleet diversity. The IoT certificate lifecycle management market benefits when buyers adopt automated enrollment engines rather than manual certificate handling. This need favors platforms that can process high volumes without repeated human intervention. The operational burden reaches beyond initial certificate issuance. Sensors, gateways, controllers, vehicles, and smart meters often have different network access and renewal windows. Organizations must maintain visibility across these devices if they are to avoid expired certificates that disrupt operations. A unified platform can apply policy to identities across mixed device estates while keeping an audit trail.
Regulatory Pressure for Security by Design and Lifecycle Support
The EU Cyber Resilience Act places lifecycle security obligations on products with digital elements. Its vulnerability reporting obligations apply from September 2026, while the broader lifecycle requirements apply from December 2027. These requirements bring certificate management into product engineering and supplier assessments rather than leaving it as a later security task. ETSI's draft EN 304 624 sets out cybersecurity requirements for PKI and certificate-issuance software within this framework. It addresses certificate validity controls, access restrictions for privileged operations, and secure signing practices.[1] Certification systems are also becoming more interconnected across the Asia-Pacific region. Japan's JC-STAR scheme received mutual recognition with Singapore's Cybersecurity Labeling Scheme in June 2026, creating a pathway spanning multiple jurisdictions. This alignment can reduce duplication when manufacturers sell into multiple regulated markets. It also makes certificate lifecycle support more relevant in product procurement and compliance reviews.
Industrial Operational Technology and Critical Infrastructure Modernization
Industrial systems require certificate processes that fit production conditions. ISA/IEC 62443 covers security for industrial automation and control systems and identifies the need for structured security measures in these environments.[2] A certificate renewal can affect plant availability when a controller or gateway cannot be reached during normal production. Renewal work must therefore fit within planned maintenance periods, which may be separated by months. This makes pre-scheduled and zero-touch certificate operations important for industrial deployments. The IoT certificate lifecycle management market can serve this requirement through tools that integrate with operational technology protocols and restricted networks. Industrial Internet of Things use cases bring cloud-connected and local systems together. This makes the connection between certificate policy and operational design more direct. Platforms need to accommodate OPC UA GDS Push, EST, and CMPv2, where those protocols are used.
Cloud, Edge, and Zero-Trust Architecture Adoption
Cloud deployment supports centralized policy administration and elastic certificate enrollment capacity. It can also help organizations apply software updates without maintaining equivalent infrastructure at every location. Microsoft documents X.509 certificate management for Azure IoT environments, showing the role of cloud platforms in organizing device certificate controls. Edge devices add another requirement because they may operate with intermittent network access. Certificate platforms need to prepare credentials in advance and restore normal operation once connectivity is restored. The IoT certificate lifecycle management market is consequently moving toward systems that coordinate cloud, server, and edge environments. Zero-trust designs rely on identity checks at the device level. Shorter credential life cycles raise renewal activity and make manual processes less reliable. This favors policy-driven workflows that issue or renew certificates based on defined conditions rather than on individual administrator action.
Restraints Impact Analysis*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Legacy Device Constraints and Limited Crypto-Agility | -1.8% | Global, more acute in Asia-Pacific and Africa | Long term (≥ 4 years) |
| Shortage of PKI, Operational Technology, and Embedded-Security Expertise | -1.4% | Global | Medium term (2-4 years) |
| Intermittent Connectivity and Incomplete Over-the-Air Update Reachability | -0.9% | Africa, South America, and Asia-Pacific emerging markets | Medium term (2-4 years) |
| Certificate Chain Size, Compute, and Storage Constraints in Constrained Devices | -0.6% | Global | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Legacy Device Constraints and Limited Crypto-Agility
Long-lived devices can remain in industrial, medical, and grid settings for 10-20 years. Many of these endpoints were designed before current certificate automation practices and post-quantum planning became priorities. Some contain fixed RSA-2048 or ECC P-256 implementations in firmware or secure elements. Replacing those implementations can require hardware changes or maintenance that is difficult to schedule. The IETF describes the larger key sizes and higher computational demands associated with post-quantum approaches for constrained devices.[3] These limitations slow the shift to new cryptographic profiles across installed fleets. Certificate validation errors can also cause availability issues. CISA's 2025 advisory on Johnson Controls iSTAR panels reported an improper certificate expiration validation issue that could affect communications when a certificate expires. This issue shows why renewal planning is not only a security task. Vendors need migration options that maintain operation for established devices while allowing newer endpoints to use more adaptable profiles. These options may include staged certificate policies, local gateways, or managed replacement cycles. The IoT certificate lifecycle management market must therefore address constraints that cannot be solved by a cloud interface alone.
Shortage of PKI, Operational Technology, and Embedded-Security Expertise
Certificate lifecycle work spans PKI engineering, operational technology protocols, and embedded-device security. These skills are commonly held by separate teams, which complicates implementation and day-to-day ownership. Organizations also need to understand network segmentation, renewal timing, and the capabilities of installed devices. The 47-day public SSL/TLS certificate transition has increased attention on operating models and automation readiness. The same need is more challenging for operational technology environments that have restricted connectivity and lower certificate awareness.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Segment Analysis
By Component: Software Leads While Services Address Skills Gaps
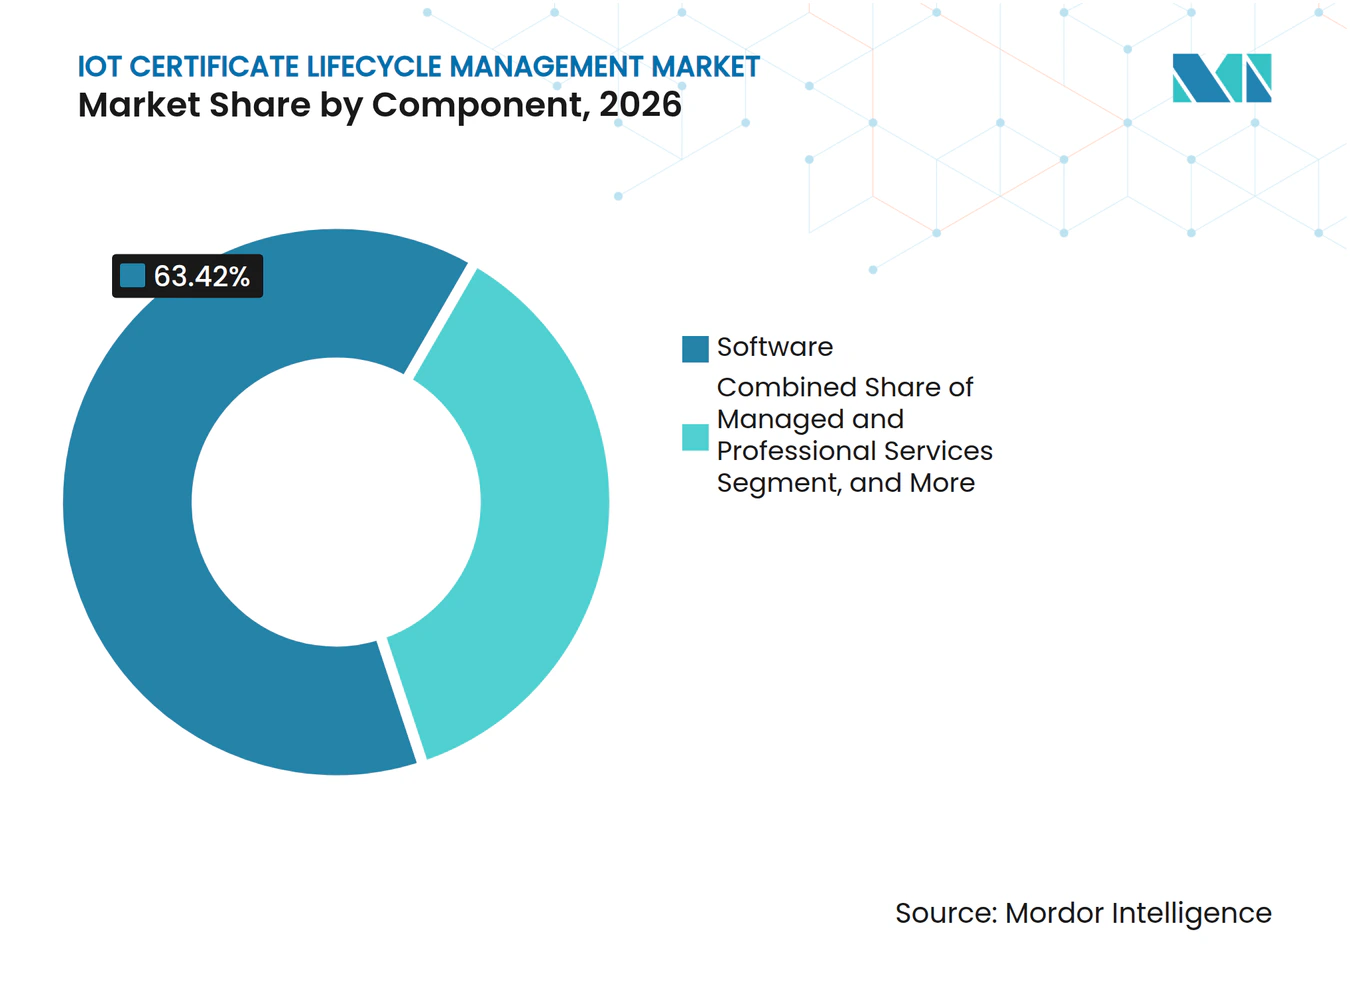
Software held 63.42% of the market in 2026. This position reflects demand for consolidated discovery, policy administration, enrollment automation, and certificate monitoring. Buyers are selecting systems that provide accountability across the certificate life cycle rather than separate tools for each task. A software platform can coordinate issuance and renewal across device groups while retaining governance records. Hardware appliances and secure key infrastructure still have a role in highly regulated and air-gapped settings. Defense, critical infrastructure, and regulated financial services may require offline issuance or locally controlled cryptographic keys.
Managed and professional services are projected to expand at a 15.71% CAGR through 2032. Their role is linked to the difficulty of finding personnel who understand PKI, operational technology, and embedded systems together. SEALSQ states that its INeS platform manages digital identities for more than 30 million smart meters and industrial IoT devices, illustrating the scale addressed by managed PKI offerings. Service providers can support initial provisioning, policy design, and recurring lifecycle tasks. The IoT certificate lifecycle management market is also seeing software and services combined in multiyear subscriptions. That model can reduce the gap between a platform purchase and its practical operation.



By Deployment: Cloud Adoption Expands Centralized Orchestration
Cloud-based deployment accounted for 67.84% of the IoT certificate lifecycle management market size in 2026. It is also projected to expand at a 16.23% CAGR through 2032. Cloud systems support centrally managed policy, elastic certificate enrollment, and updates to cryptographic libraries. This capability is useful when certificate volumes are difficult to predict across distributed device fleets. The deployment model can reduce the infrastructure burden for organizations that would otherwise maintain multiple local certificate services.
Cloud deployment does not eliminate the need for local controls. On-premises systems remain relevant where root keys must stay within a facility or where networks are air-gapped. Hybrid models can keep sensitive PKI roots on-site while moving enrollment automation and reporting into a cloud-coordinated layer. Sectigo introduced its Orchestration Gateway in August 2026 as a single layer to automate discovery, issuance, renewal, and deployment across server, cloud, and edge environments.[4] This model reflects the need to operate across different infrastructure locations. The IoT certificate lifecycle management market can therefore serve buyers who need centralized visibility without moving every security control off-site.
By Organization Size: Large Enterprises Anchor Spending While Small and Medium-Sized Enterprises Expand
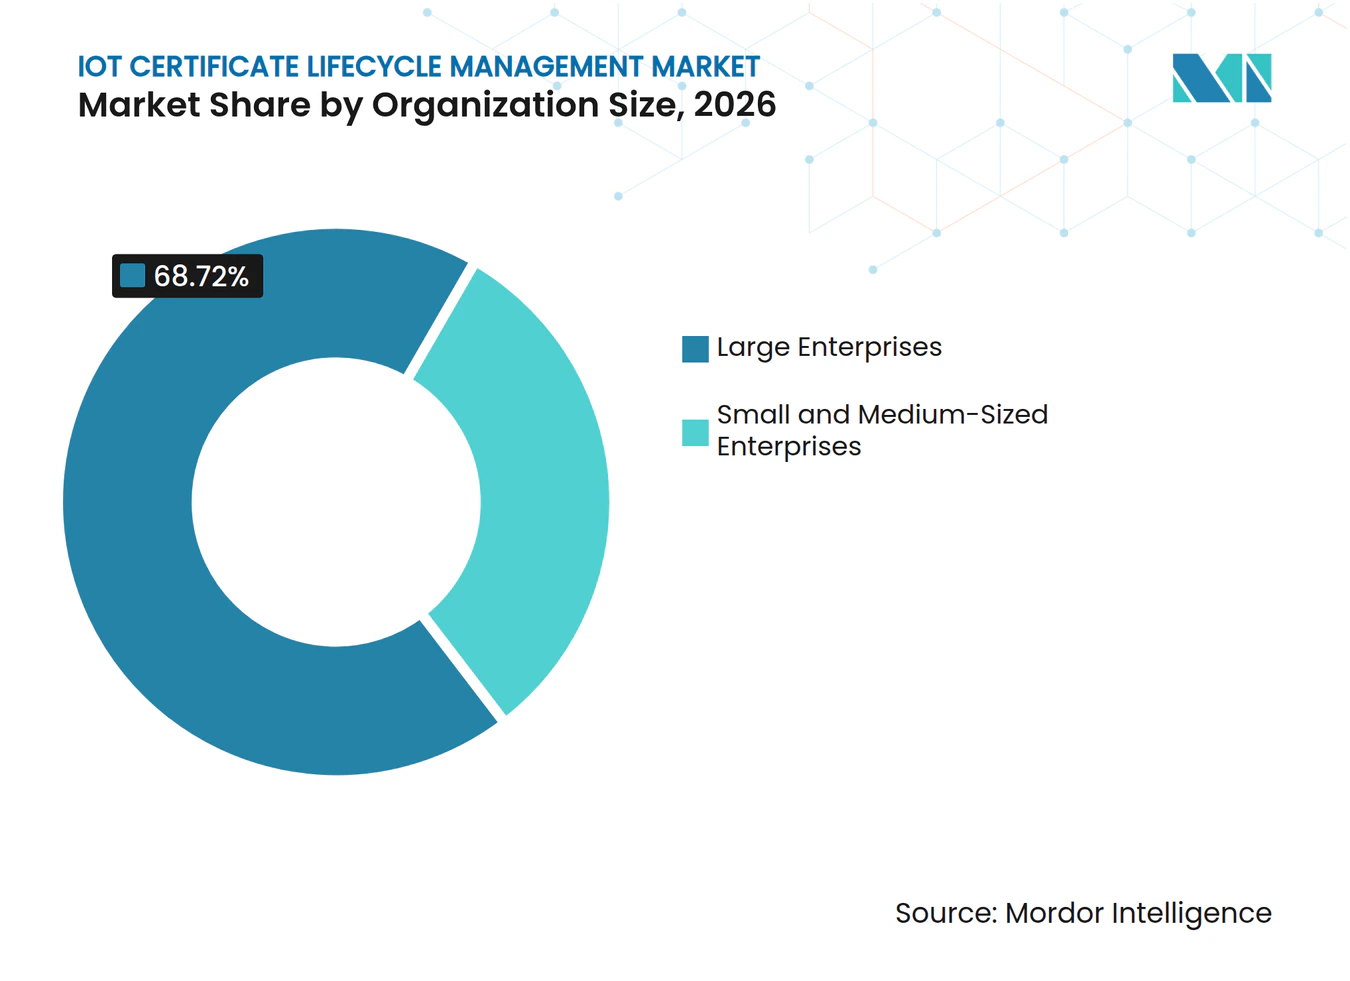
Large enterprises held 68.72% of the market in 2026. Their certificate fleets often span multiple sites, business units, and PKI hierarchies. These organizations can have dedicated security teams, but also face more complex approval structures and operating environments. High device volume makes certificate expiration a significant operational risk. Large enterprises, therefore, fund platform deployments that unify certificate visibility and automate routine actions.
Small and medium-sized enterprises are expected to expand at a 17.91% CAGR through 2032. Cloud-native services lower the initial barrier because buyers do not need to maintain on-premises CA hardware or a full internal administration team. Supply-chain requirements also bring smaller manufacturers into certificate-based device authentication programs. IEC 62443 requirements can affect suppliers that participate in industrial customer environments. The IoT certificate lifecycle management market can reach this group through simpler packages and managed operations. Smaller organizations still need platforms that fit limited security staffing and restricted capital budgets.

By Application: Device Authentication Remains the Core Use Case
Device authentication held 28.92% of the market in 2026. It verifies a device's cryptographic identity when it connects to a service, gateway, or another endpoint. This use case underpins secure device-to-cloud and device-to-device communications. Certificates support TLS, and mutual TLS sessions are used to exchange operational data. The IoT certificate lifecycle management market depends on this basic identity task because other security functions build on a trusted device identity.
Secure boot and hardware attestation are projected to expand at a 16.51% CAGR through 2032. These functions determine whether a device starts in a trusted state before it gains access to a network or service. Firmware signing and secure over-the-air updates are also important because manufacturers must maintain product security throughout an operating life. SEALSQ added secure code-signing capabilities to INeS in August 2025 for firmware integrity activities related to RED and Cyber Resilience Act requirements. The IoT certificate lifecycle management market supports these applications by providing the certificate governance needed for signing and validation. Data encryption and integrity protection are complementary uses in which devices require secure communication after identity is established.
By Device Type: Sensors and Actuators Form the Largest Installed Base
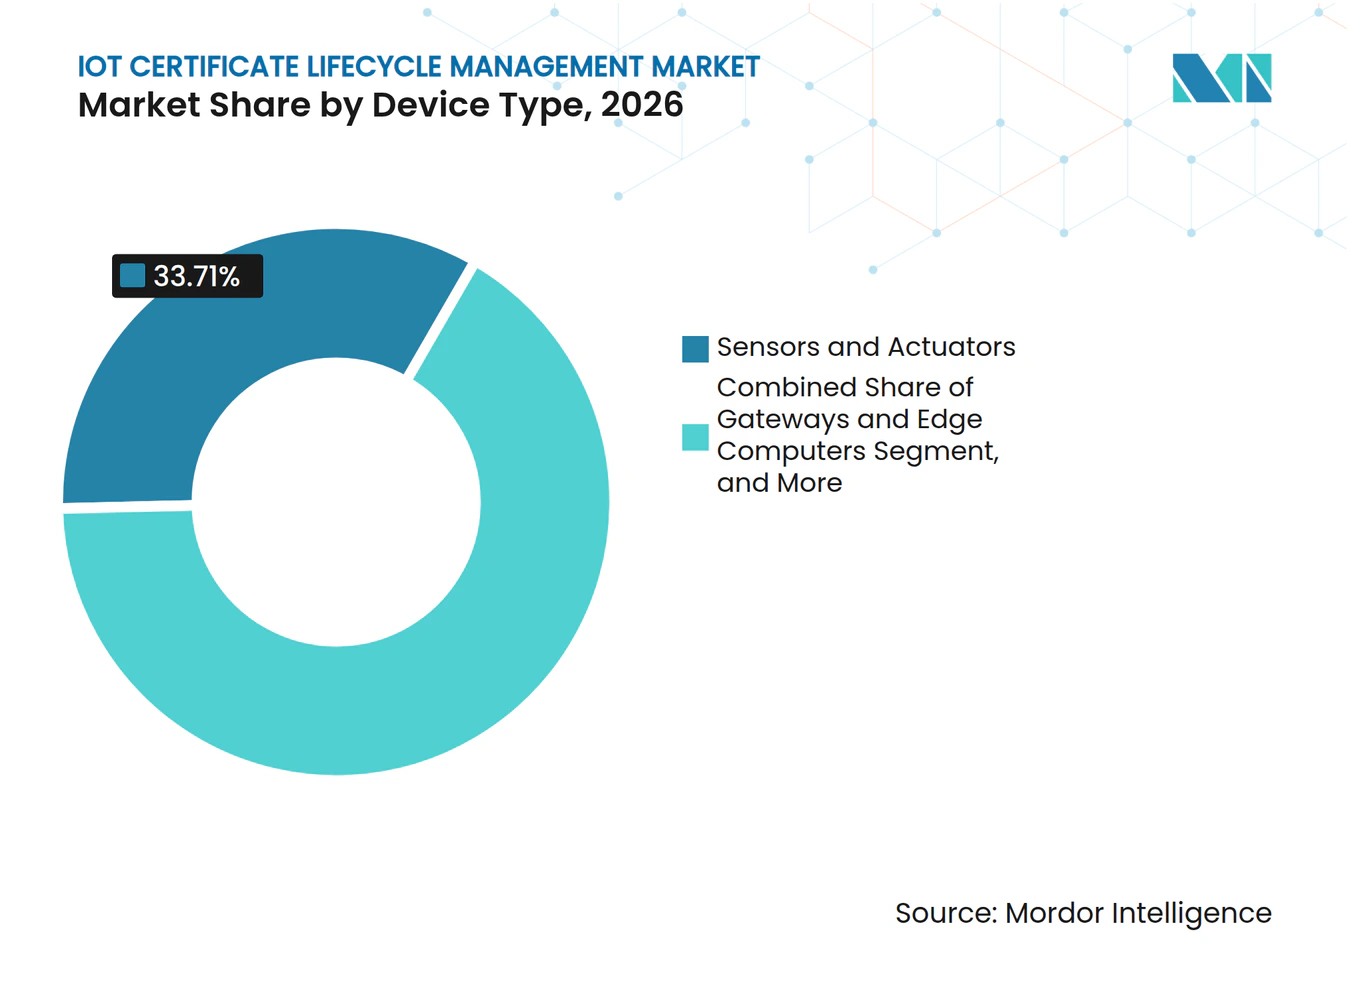
Sensors and actuators accounted for 33.71% of the market in 2026. Their leading position reflects the large number of devices deployed in industrial and consumer Internet of Things applications. Each device needs a distinct cryptographic identity, often created during manufacturing or enrollment. The high volume of these endpoints makes manual renewal impractical. Certificate controls must also account for devices with limited processing capacity and restricted connectivity.
Connected vehicles and roadside units are projected to expand at a 16.72% CAGR through 2032. V2X systems require managed credentials to support trusted communication among vehicles, road infrastructure, and related services. The 5GAA technical report addresses credential management for commercial V2X deployments.[5] Gateways and edge computers can act as aggregation points for constrained sensors that cannot run full certificate clients. Industrial controllers require renewal that is coordinated with planned plant maintenance. The IoT certificate lifecycle management market must support different device capabilities rather than applying a single enrollment model to every endpoint.
By End-User Industry: Manufacturing Provides the Broadest Adoption Base
Manufacturing accounted for 26.54% of the market in 2026. Industrial equipment relies on device identities to control access and protect data exchanges across plant networks. A certificate failure can affect production continuity, which raises the value of proactive monitoring and scheduled renewal. IEC 62443 provides a security framework for industrial automation and control systems. Manufacturing buyers also need tools that work with industrial protocols and equipment that cannot be interrupted freely.
Transportation and logistics are expected to expand at a 16.51% CAGR through 2032. Connected fleet security, V2X systems, and vehicle software update requirements are the key requirements in this segment. Healthcare and medical devices also require device identity controls, although hardware constraints can limit deployment speed. BFSI organizations use certificate management across ATMs, point-of-sale devices, and machine identity workflows. Information technology and telecommunications operators manage certificates across network equipment and service environments. Government procurement is connected to essential-entity obligations and public-sector security standards. The IoT certificate lifecycle management market therefore addresses a wide range of operational settings with different renewal windows and compliance needs.
Geography Analysis
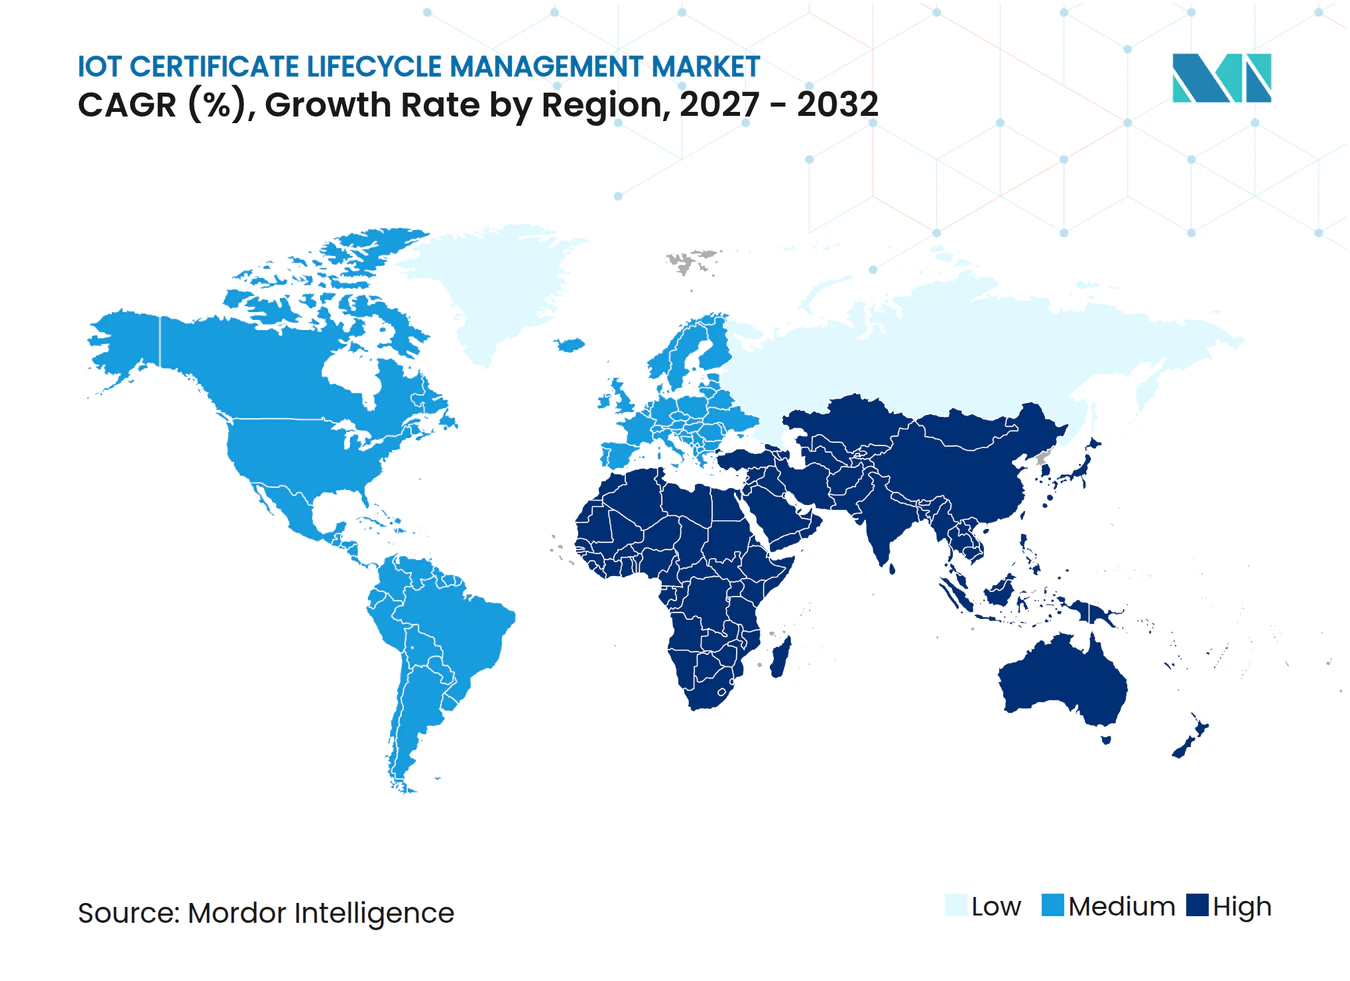
North America held 34.66% of the IoT certificate lifecycle management market share in 2026. The region has established PKI infrastructure, cloud-focused vendors, and a large base of regulated buyers. Federal procurement requirements establish a defined pathway for providers to meet public-sector security expectations. Keyfactor announced its FedRAMP authorization in 2026, reflecting the compliance threshold for cloud platforms serving U.S. government customers. Canada adds demand through connected manufacturing and smart-city programs that use sensors and gateways. South America remains smaller, with Brazil supported by digitized financial services and connected agribusiness deployments.
Europe is the second-largest regional market. Germany, the United Kingdom, France, and the Nordic countries are actively adopting because manufacturers and critical infrastructure operators face structured security requirements. The Cyber Resilience Act makes lifecycle security more relevant for producers of connected products. The European Commission provides policy and implementation materials for the Cyber Resilience Act for manufacturers. The United Kingdom's PSTI framework extends the security focus to consumer Internet of Things products. The Middle East is developing smart-city and energy-grid projects, while Africa remains at an earlier stage because infrastructure variability constrains broad deployment.
Asia-Pacific is projected to expand at a 17.52% CAGR through 2032. China, Japan, South Korea, and India are increasing the need for trusted device identity across manufacturing, transport, and electronics supply chains. China's YD/T 6866-2026 sets out guidance for pseudonymous digital certificates in Internet of Things enrollment, revocation, and inter-CA trust.[6] Japan's JC-STAR program and its recognition arrangement with Singapore support wider product security alignment IPA.GO.JP. South Korea's IoT cybersecurity certification activity supports compliance-led demand among electronics manufacturers. India adds demand as device makers integrate certificate provisioning into factory processes for export-oriented products.
Competitive Landscape
Market Concentration
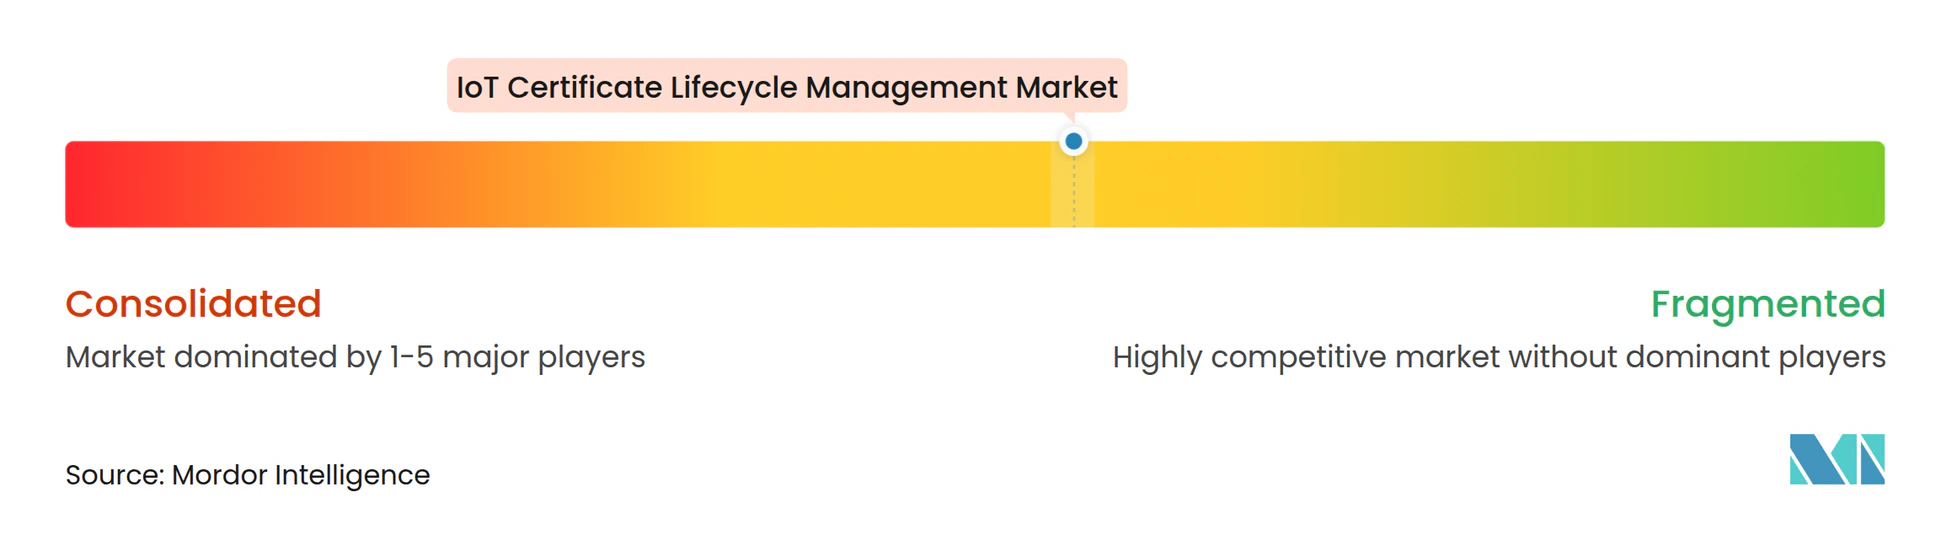
The IoT certificate lifecycle management market has a moderate level of concentration. Dedicated providers include Keyfactor, DigiCert, Sectigo, AppViewX, and Device Authority. They compete with broader security and industrial technology suppliers such as Thales, IBM, Microsoft, Cisco, and Siemens. These companies differ in their depth of PKI, automation, hardware security, cloud integration, and operational technology coverage. Competition is focused on the ability to manage identities at scale and support mixed device environments. Buyers also assess how well a platform can support policy controls, audit records, and renewal automation across long-lived assets.
Consolidation has affected the vendor landscape. Sectigo acquired Entrust's public certificate business in January 2025, expanding its enterprise operations. Keyfactor announced a USD 1 billion+ strategic growth investment in July 2026 and stated that the funding would support expansion, product innovation, and acquisitions. AppViewX acquired Eos in March 2026 to extend its certificate lifecycle platform to AI agent and machine identity security. These moves show that providers are extending from certificate issuance into broader identity and automation functions. The IoT certificate lifecycle management market rewards vendors that can unify lifecycle administration rather than offer isolated certificate tools.
Platform strategy increasingly combines issuance, automation, post-quantum readiness, and identity governance. DigiCert began moving customers from IoT Trust Manager to Device Trust Manager on the DigiCert ONE architecture during 2026. SEALSQ's 2026 certification roadmap for secure elements and trusted platform modules also addresses the hardware root-of-trust layer for device onboarding. Smaller buyers and industrial operators remain an opening for providers that support operational technology protocols without requiring a large enterprise PKI team. Purpose-built support for OPC UA GDS Push, LwM2M, and MQTT/TLS can distinguish providers in industrial Internet of Things use cases. Standards participation also matters because embedded post-quantum migration requirements are still developing.
IoT Certificate Lifecycle Management Industry Leaders
-
DigiCert, Inc.
-
Keyfactor, Inc.
-
Palo Alto Networks, Inc.
-
CyberArk Software Ltd.
-
Entrust Corporation
- *Disclaimer: Major Players sorted in no particular order
Recent Industry Developments
- September 2026: DigiCert secured a partnership with Newfold Digital, serving approximately 6 million customers globally, to modernize its SSL/TLS certificate infrastructure across brands including Network Solutions Group and Bluehost Group, extending DigiCert's AI-powered DigiCert ONE platform, encompassing PKI, DNS, and CLM, across a major web hosting ecosystem.
- August 2026: Sectigo launched the general availability of Sectigo Orchestration Gateway (SOG), an automation layer within Sectigo Certificate Manager (SCM) enabling a single lightweight installation to automate certificate discovery, issuance, renewal, and deployment across server, cloud, and edge environments, with native integration with CyberArk, HashiCorp, and Delinea for credential management.
- April 2026: Sectigo partnered with F5 to deliver automated CLM across the F5 Application Delivery and Security Platform (ADSP), enabling native SSL/TLS certificate issuance, renewal, and replacement as part of the F5 ADSP Partner Program.
- March 2026: AppViewX acquired Eos on March 19 to extend its CLM platform to AI agent and machine identity security, responding to the emergence of AI agent identities as the fastest-growing machine identity category in enterprise environments.
Global IoT Certificate Lifecycle Management Market Report Scope
The IoT certificate lifecycle management market encompasses software platforms and related services that automate and govern the discovery, issuance, provisioning, deployment, monitoring, renewal, rotation, and revocation of digital certificates for Internet of Things devices. These solutions establish trusted device identities, secure device-to-device and device-to-cloud communications, and support scalable compliance and cryptographic key management across connected-device lifecycles.
The IoT Certificate Lifecycle Management Market Report is Segmented by Component (Software, Hardware Appliances and Secure Key Infrastructure, and Managed and Professional Services), Deployment Mode (Cloud-Based, On-Premises, and Hybrid), Organization Size (Large Enterprises, and Small and Medium-Sized Enterprises), Application (Device Authentication, Secure Device-to-Cloud Communication, Secure Device-to-Device Communication, Firmware Signing and Secure OTA Updates, Secure Boot and Hardware Attestation, Data Encryption and Integrity Protection, and Other Applications), Device Type (Sensors and Actuators, Gateways and Edge Computers, Industrial Controllers and PLCs, Connected Vehicles and Roadside Units, Smart Meters and Grid Devices, and Other Devices), End-User Industry (Manufacturing, Transportation and Logistics, Healthcare and Medical Devices, Banking, Financial Services, and Insurance (BFSI), IT and Telecommunications, Government and Public Administration, and Other End-User Industries), and Geography (North America, South America, Europe, Asia-Pacific, Middle East, and Africa). The Market Forecasts are Provided in Terms of Value (USD).
| Software |
| Hardware Appliances and Secure Key Infrastructure |
| Managed and Professional Services |
| Cloud-Based |
| On-Premises |
| Hybrid |
| Large Enterprises |
| Small and Medium-Sized Enterprises |
| Device Authentication |
| Secure Device-to-Cloud Communication |
| Secure Device-to-Device Communication |
| Firmware Signing and Secure OTA Updates |
| Secure Boot and Hardware Attestation |
| Data Encryption and Integrity Protection |
| Other Applications |
| Sensors and Actuators |
| Gateways and Edge Computers |
| Industrial Controllers and PLCs |
| Connected Vehicles and Roadside Units |
| Smart Meters and Grid Devices |
| Other Devices |
| Manufacturing |
| Transportation and Logistics |
| Healthcare and Medical Devices |
| Banking, Financial Services, and Insurance (BFSI) |
| IT and Telecommunications |
| Government and Public Administration |
| Other End-User Industries |
| North America | United States |
| Canada | |
| Mexico | |
| South America | Brazil |
| Argentina | |
| Rest of South America | |
| Europe | Germany |
| United Kingdom | |
| France | |
| Italy | |
| Spain | |
| Russia | |
| Rest of Europe | |
| Asia-Pacific | China |
| Japan | |
| South Korea | |
| India | |
| Rest of Asia-Pacific | |
| Middle East | Saudi Arabia |
| United Arab Emirates | |
| Israel | |
| Rest of Middle East | |
| Africa | South Africa |
| Nigeria | |
| Rest of Africa |
| By Component | Software | |
| Hardware Appliances and Secure Key Infrastructure | ||
| Managed and Professional Services | ||
| By Deployment | Cloud-Based | |
| On-Premises | ||
| Hybrid | ||
| By Organization Size | Large Enterprises | |
| Small and Medium-Sized Enterprises | ||
| By Application | Device Authentication | |
| Secure Device-to-Cloud Communication | ||
| Secure Device-to-Device Communication | ||
| Firmware Signing and Secure OTA Updates | ||
| Secure Boot and Hardware Attestation | ||
| Data Encryption and Integrity Protection | ||
| Other Applications | ||
| By Device Type | Sensors and Actuators | |
| Gateways and Edge Computers | ||
| Industrial Controllers and PLCs | ||
| Connected Vehicles and Roadside Units | ||
| Smart Meters and Grid Devices | ||
| Other Devices | ||
| By End-User Industry | Manufacturing | |
| Transportation and Logistics | ||
| Healthcare and Medical Devices | ||
| Banking, Financial Services, and Insurance (BFSI) | ||
| IT and Telecommunications | ||
| Government and Public Administration | ||
| Other End-User Industries | ||
| By Geography | North America | United States |
| Canada | ||
| Mexico | ||
| South America | Brazil | |
| Argentina | ||
| Rest of South America | ||
| Europe | Germany | |
| United Kingdom | ||
| France | ||
| Italy | ||
| Spain | ||
| Russia | ||
| Rest of Europe | ||
| Asia-Pacific | China | |
| Japan | ||
| South Korea | ||
| India | ||
| Rest of Asia-Pacific | ||
| Middle East | Saudi Arabia | |
| United Arab Emirates | ||
| Israel | ||
| Rest of Middle East | ||
| Africa | South Africa | |
| Nigeria | ||
| Rest of Africa | ||
Key Questions Answered in the Report
What is the size of the IoT certificate lifecycle management market?
The IoT certificate lifecycle management market size is projected to be USD 1.67 billion in 2026, USD 1.91 billion in 2027, and reach USD 3.64 billion by 2032, growing at a CAGR of 13.77% from 2027 to 2032.
What is driving demand for IoT certificate lifecycle management?
Larger device fleets, lifecycle security rules, industrial modernization, and cloud and edge deployments are increasing the need for automated certificate operations. These conditions make manual issuance and renewal harder to sustain across distributed endpoints.
Which component leads the IoT certificate lifecycle management market?
Software leads with 63.42% share in 2026, supported by demand for integrated discovery, enrollment, policy management, and monitoring across diverse device fleets.
Which deployment model is expanding fastest for IoT certificate lifecycle management?
Cloud-based deployment holds 67.84% share in 2026 and is projected to expand at a 16.23% CAGR through 2032.
Which end-user sector has the largest adoption base?
Manufacturing leads with 26.54% share in 2026 because industrial equipment requires managed device identity and carefully scheduled certificate renewal to protect operational continuity.
Which region has the highest forecast expansion rate?
Asia-Pacific is projected to expand at a 17.52% CAGR through 2032, led by China, Japan, South Korea, and India, where connected manufacturing, transport, and electronics programs increase device identity needs.