
Authorization Management Market Size and Share
Market Overview
| Study Period | 2021 - 2032 |
|---|---|
| Market Size (2027) | USD 2.78 Billion |
| Market Size (2032) | USD 9.85 Billion |
| Growth Rate (2027 - 2032) | 28.75 % |
| Fastest Growing Market | Asia-Pacific |
| Largest Market | North America |
| Market Concentration | Low |
Major Players *Disclaimer: Major Players sorted in no particular order Image © Mordor Intelligence. Reuse requires attribution under CC BY 4.0. | |
Authorization Management Market Analysis by Mordor Intelligence
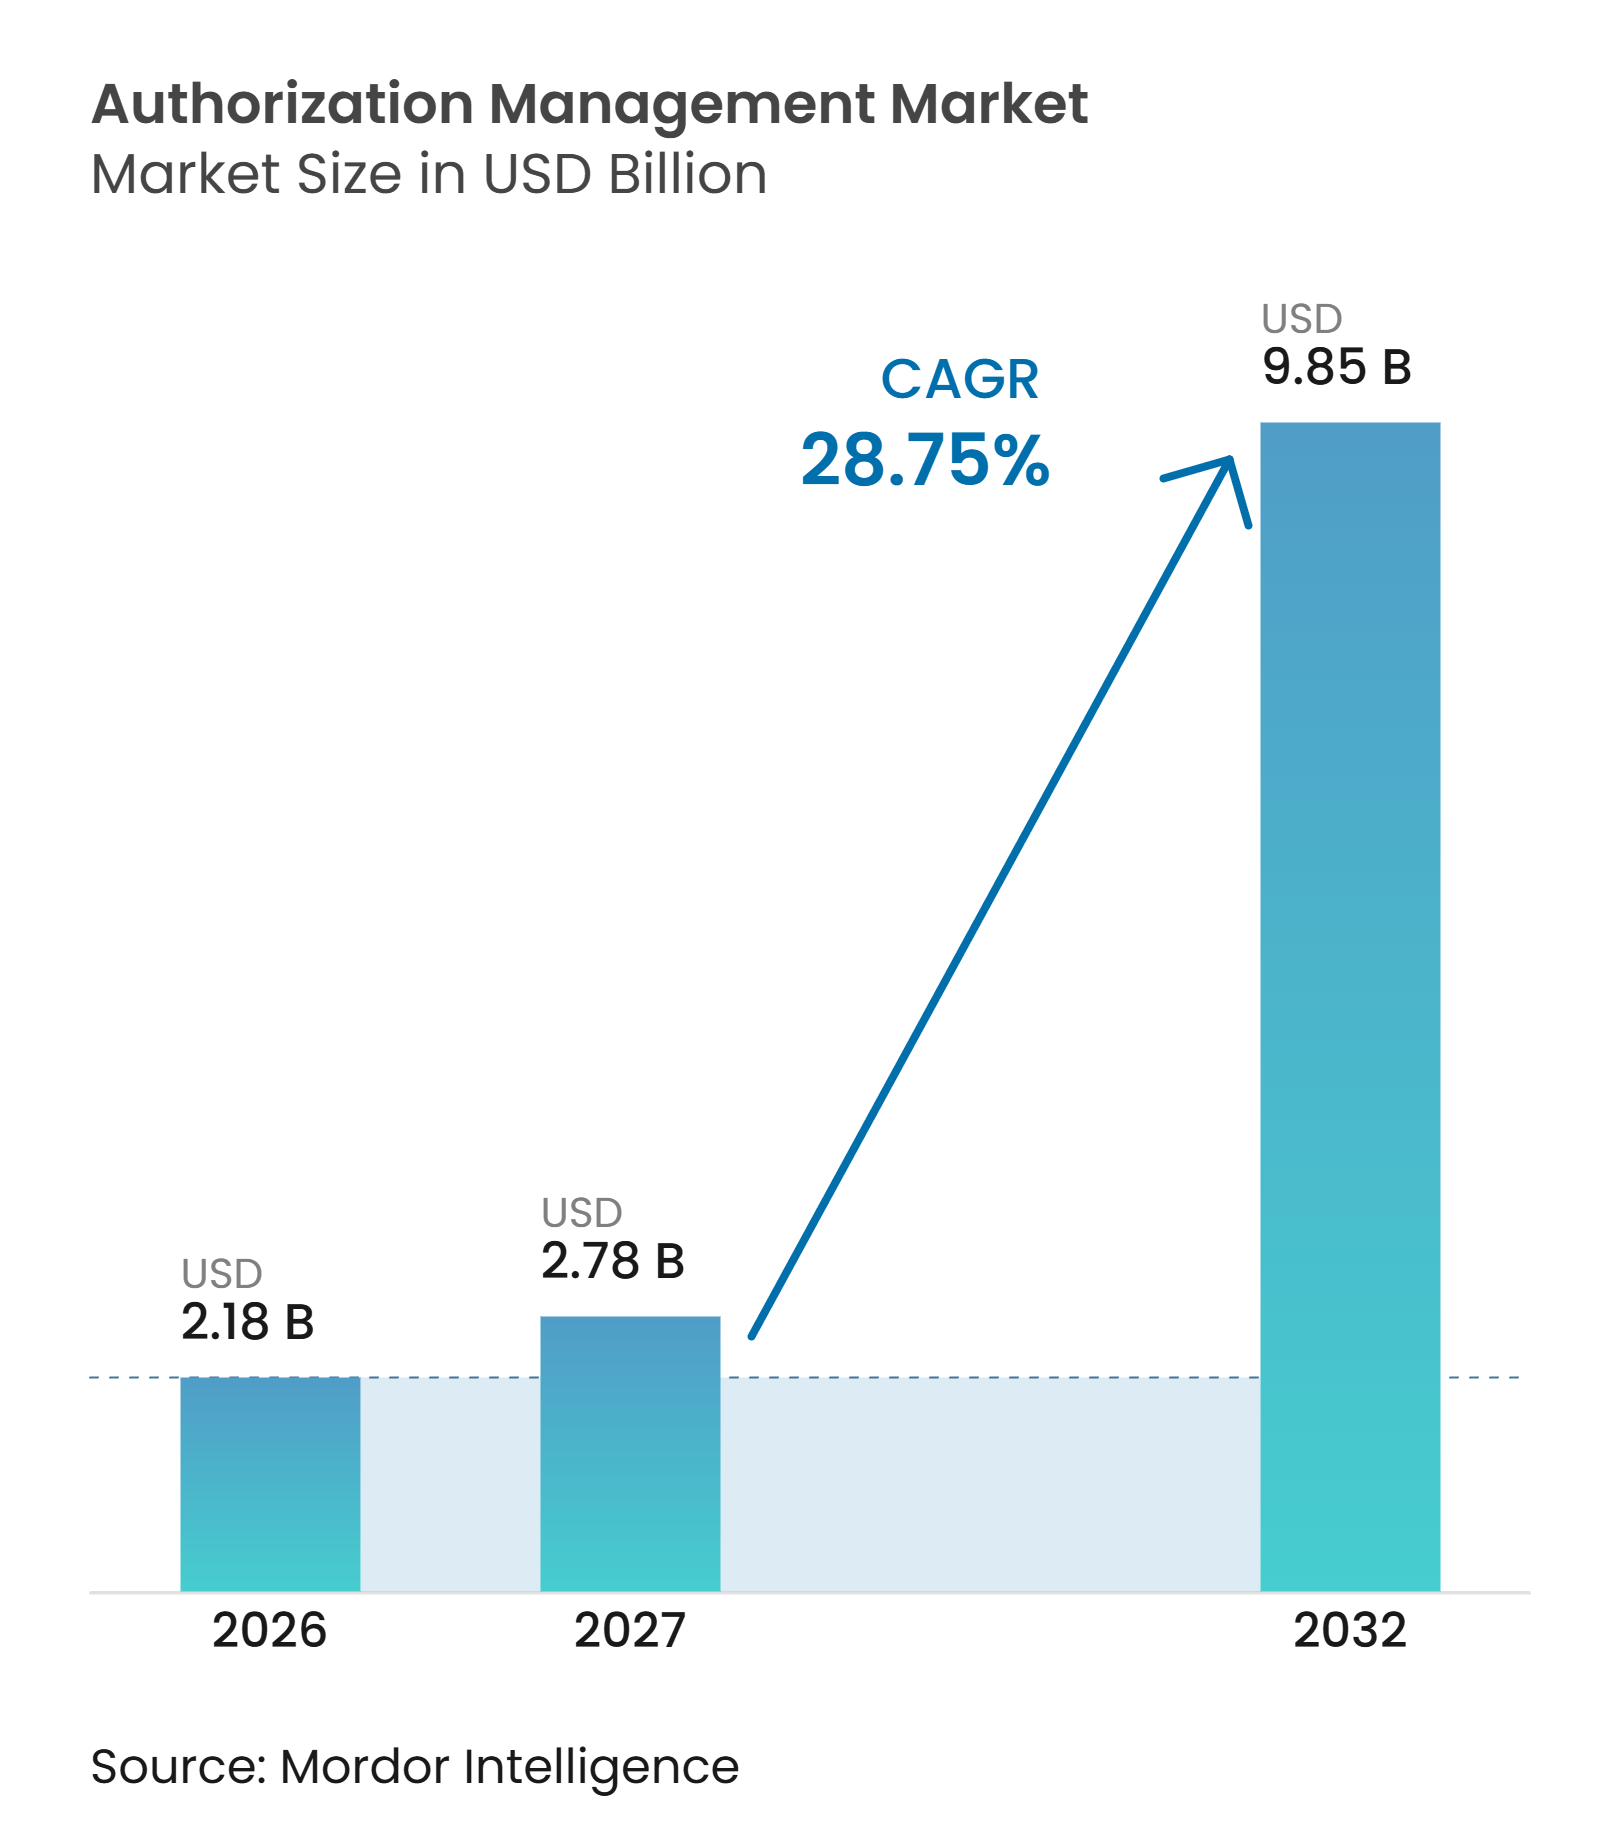
The Authorization Management Market size is projected to expand from USD 2.18 billion in 2026 to USD 9.85 billion by 2032, registering a CAGR of 28.75% between 2027 and 2032. Demand is rising as zero-trust programs require access decisions to be continuously verified rather than only when a user starts a session. The growth of service accounts, API keys, access tokens, and AI agent credentials is increasing the number of identities that need controlled permissions. Regulatory expectations for auditable least-privilege access are also moving authorization management from a preferred security practice toward a compliance requirement. Vendors are responding with runtime policy engines, managed cloud services, and tools that generate evidence of access for audit teams. The Authorization Management Market is therefore moving beyond a narrow developer-tooling role and becoming a core part of the security infrastructure.
Key Report Takeaways
- By component, Policy Decision Point and Enforcement held 58.16% of the Authorization Management Market revenue in 2026, while Authorization Data and Relationship Store are projected to expand at a 30.14% CAGR through 2032.
- By deployment mode, on-premises held 65.44% of the Authorization Management Market revenue in 2026, while cloud is projected to expand at a 30.41% CAGR through 2032.
- By organization size, large enterprises held 71.29% of the Authorization Management Market revenue in 2026, while small and medium-sized enterprises are projected to expand at a 30.78% CAGR through 2032.
- By end-use industry, BFSI held 29.15% of the Authorization Management Market revenue in 2026, while Government and Public Administration is projected to expand at a 29.44% CAGR through 2032.
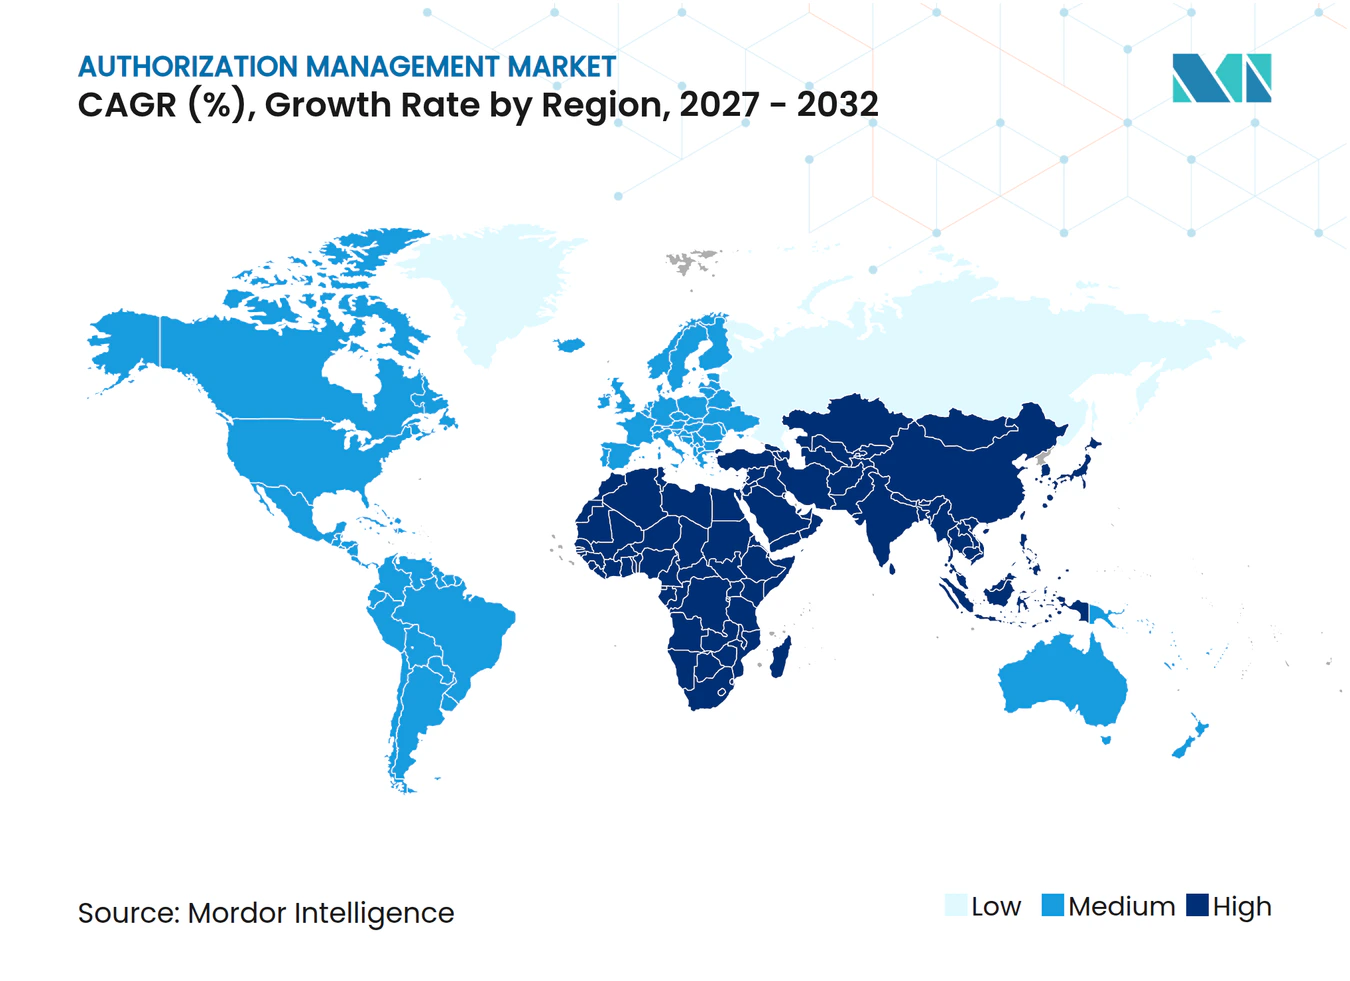
- By geography, North America held 37.16% of the Authorization Management Market revenue in 2026, while Asia-Pacific is projected to expand at a 29.85% CAGR through 2032.
Note: Market numbers in this report are based on Mordor Intelligence's proprietary estimation framework, which combines nine months of actuals with Q4 projections for base year 2026.
Market Trends and Insights
Drivers Impact Analysis of Authorization Management Market*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Zero Trust and Continuous Authorization Adoption | +7.5% | Global, with early gains in North America and Western Europe | Short term (≤ 2 years) |
| Cloud and Multi-Cloud Permission Complexity | +5.6% | North America and Europe, with spillover to Asia-Pacific | Short term (≤ 2 years) |
| Expansion of Non-Human Identity and API Access | +4.8% | Global, concentrated in North America and Asia-Pacific technology hubs | Medium term (2-4 years) |
| Regulatory Pressure for Auditable Least Privilege | +3.6% | North America and the EU, with spillover to Asia-Pacific and the Middle East and Africa | Medium term (2-4 years) |
| Authorization for AI Agents and Tool Calls | +3.2% | Global | Medium term (2-4 years) |
| Policy-as-Code Adoption in DevSecOps | +2.4% | North America, Western Europe, and Asia-Pacific technology centers | Short term (≤ 2 years) |
| Source: Mordor Intelligence | |||
Zero Trust and Continuous Authorization Adoption
Zero trust adoption is making runtime authorization a central security control for the Authorization Management Market. Organizations need systems that reassess access when device status, threat signals, or user roles change. This differs from older models that relied on permissions assigned at session startup. The OpenID Foundation’s Continuous Access Evaluation Protocol supports the exchange of security events that can trigger access changes during an active session. NIST’s Zero Trust Architecture similarly places ongoing evaluation near the center of modern access design.[1] This requirement creates demand for policy decision points, enforcement software development kits, and complete records of access decisions.
Cloud and Multi-Cloud Permission Complexity
Multi-cloud operations create separate identity and permission models that can make consistent least-privilege enforcement difficult. Each cloud platform has its own native controls, while applications often need access across multiple environments. Microservice architectures add further requests between services and APIs. Policy logic embedded separately in each service can create duplicate rules and inconsistent updates. The Authorization Management Market benefits when organizations adopt a policy layer that works across cloud environments rather than relying on disconnected controls. Cloud delivery also reduces the operational burden for teams that lack large authorization engineering functions.
Expansion of Non-Human Identity and API Access
Service accounts, API tokens, certificates, and AI agent credentials now represent a large and growing access surface. CyberArk reported that 79% of security leaders expected machine identity counts to increase in 2025, while 50% reported a machine-identity-related breach or incident in the prior 12 months. Traditional identity tools were mainly designed around employee onboarding, review, and offboarding. They are less suited to rapid machine-to-machine authorization decisions. OWASP’s 2025 framework identifies risks associated with non-human identities and provides a common vocabulary for service accounts, tokens, and similar credentials. The Authorization Management Market can address this gap by defining, through policies, what each machine identity may access and under which conditions.
Regulatory Pressure for Auditable Least Privilege
Regulatory requirements are increasing the need for records that show who accessed a resource and why access was granted. Financial institutions must maintain strong authentication and access controls in accordance with federal interagency guidance. NIST SP 800-53 also includes access-control expectations that affect how organizations document and review permissions. In August 2026, the Netherlands published profiles for the OpenID AuthZEN Authorization API and Authorization Decision Log for government use. These standards emphasize a unique record of each authorization decision and its basis. The resulting requirement for decision-level evidence supports investment in platforms that centralize policy enforcement and audit logs.
Restraints Impact Analysis of Authorization Management Market*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Legacy Application Integration Complexity | -4.1% | Global, particularly severe in South America, the Middle East and Africa, and Asia-Pacific industrial sectors | Long term (≥ 4 years) |
| Shortage of Authorization Engineering Talent | -2.9% | Global, particularly acute in Asia-Pacific and South America | Medium term (2-4 years) |
| Fragmented Policy Languages and Decision APIs | -1.7% | Global | Short term (≤ 2 years) |
| Authorization Decision Latency and Availability Trade-offs | -1.2% | Global, amplified in high-volume transaction environments | Short term (≤ 2 years) |
| Source: Mordor Intelligence | |||
Legacy Application Integration Complexity
Authorization platforms are easiest to deploy in applications that expose modern APIs and support direct integration. Many large organizations still operate mainframes, thick-client enterprise resource planning systems, and on-premises databases that lack such interfaces. ISACA notes that disconnected applications can complicate the introduction of current access controls and automation. Reverse proxies, custom middleware, and ticket-based processes can extend coverage but add work and delay policy updates. This slows the full use of the Authorization Management Market across legacy estates. The constraint is especially relevant to financial institutions and industrial manufacturers, where older systems and strict audit requirements often exist together.
Shortage of Authorization Engineering Talent
Authorization design requires knowledge of policy modeling, distributed systems, and information security. Organizations must also choose among policy languages and application programming interfaces that are not fully interchangeable. This makes policy implementation more specialized than basic identity administration. Teams without the required expertise can rely heavily on professional services during the first deployment. They may also find it harder to adapt policies when operations or compliance requirements change. Managed services, low-code editors, and reusable policy templates can reduce the burden, but they do not remove the need for sound policy design.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Authorization Management Market Segment Analysis
By Component:
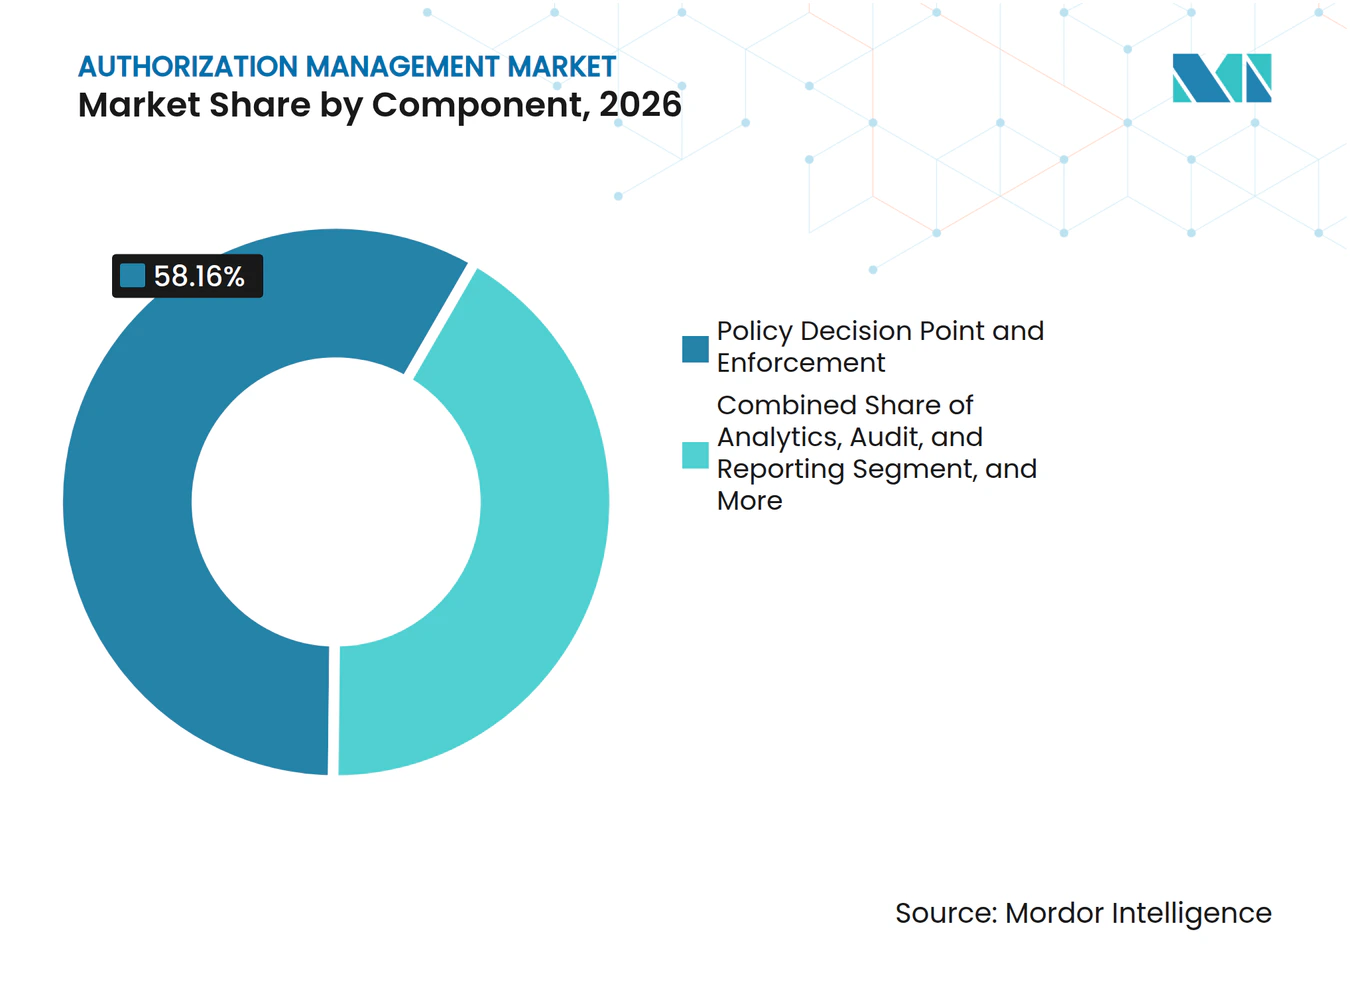
Policy Decision Points Lead While Relationship Stores Gain GroundPolicy Decision Point and Enforcement components held 58.16% of the Authorization Management Market share in 2026. These components assess every access request against defined policies, return an allow or deny outcome, and operate within the short response times required by production applications. They are commonly the first platform purchase because they provide runtime control across business applications, APIs, data services, and internal developer tools. They also generate records that audit, risk, and security teams can use to examine the context and outcome of an access request. The segment’s scale shows that customers place the greatest early value on the enforcement layer, before extending a program to more specialized capabilities.
The Authorization Data and Relationship Store is projected to record a 30.14% CAGR from 2027 to 2032. This reflects a move from flat role assignments toward relationship-based models that can describe ownership, delegation, reporting structures, and tenant boundaries. Such models are relevant to multi-tenant software, financial client relationships, and AI agent environments where permissions may apply to a single resource or action. Analytics, audit, and reporting functions remain necessary because compliance teams need evidence that can be matched to a specific control and reviewed without having to assemble spreadsheets from multiple systems. Together with other components, these functions accounted for the remaining 41.84% of 2026 component revenue.



By Deployment Mode:
On-Premises Remains Established While Cloud ExpandsOn-premises deployment accounted for 65.44% of the Authorization Management Market revenue in 2026. Regulated organizations often keep authorization systems close to sensitive data because of residency rules, air-gapped networks, local operating requirements, and prior investment in on-premises identity infrastructure. Defense agencies, sovereign wealth managers, and critical infrastructure operators may treat local deployment as an architectural requirement rather than a simple cost decision. Many organizations in this group are replacing custom access logic embedded in application code with a dedicated platform, thereby supporting ongoing demand in the on-premises category. The deployment decision reflects security, governance, integration, and operational requirements, not only the price of the software.
Cloud deployment is projected to expand at a 30.41% CAGR from 2027 to 2032. SaaS-native enterprises can use authorization as a service without installing and operating the underlying infrastructure, while multi-cloud users can apply policies above a single provider’s controls. Managed delivery can be especially useful for organizations that have limited access to specialized authorization engineers or cannot maintain a round-the-clock policy service. FusionAuth acquired Permify in November 2025 to combine authentication and fine-grained authorization in a deploy-anywhere platform.[2] Consumption-based pricing supports smaller buyers who need to increase control coverage gradually without a large hardware commitment.
By Organization Size:
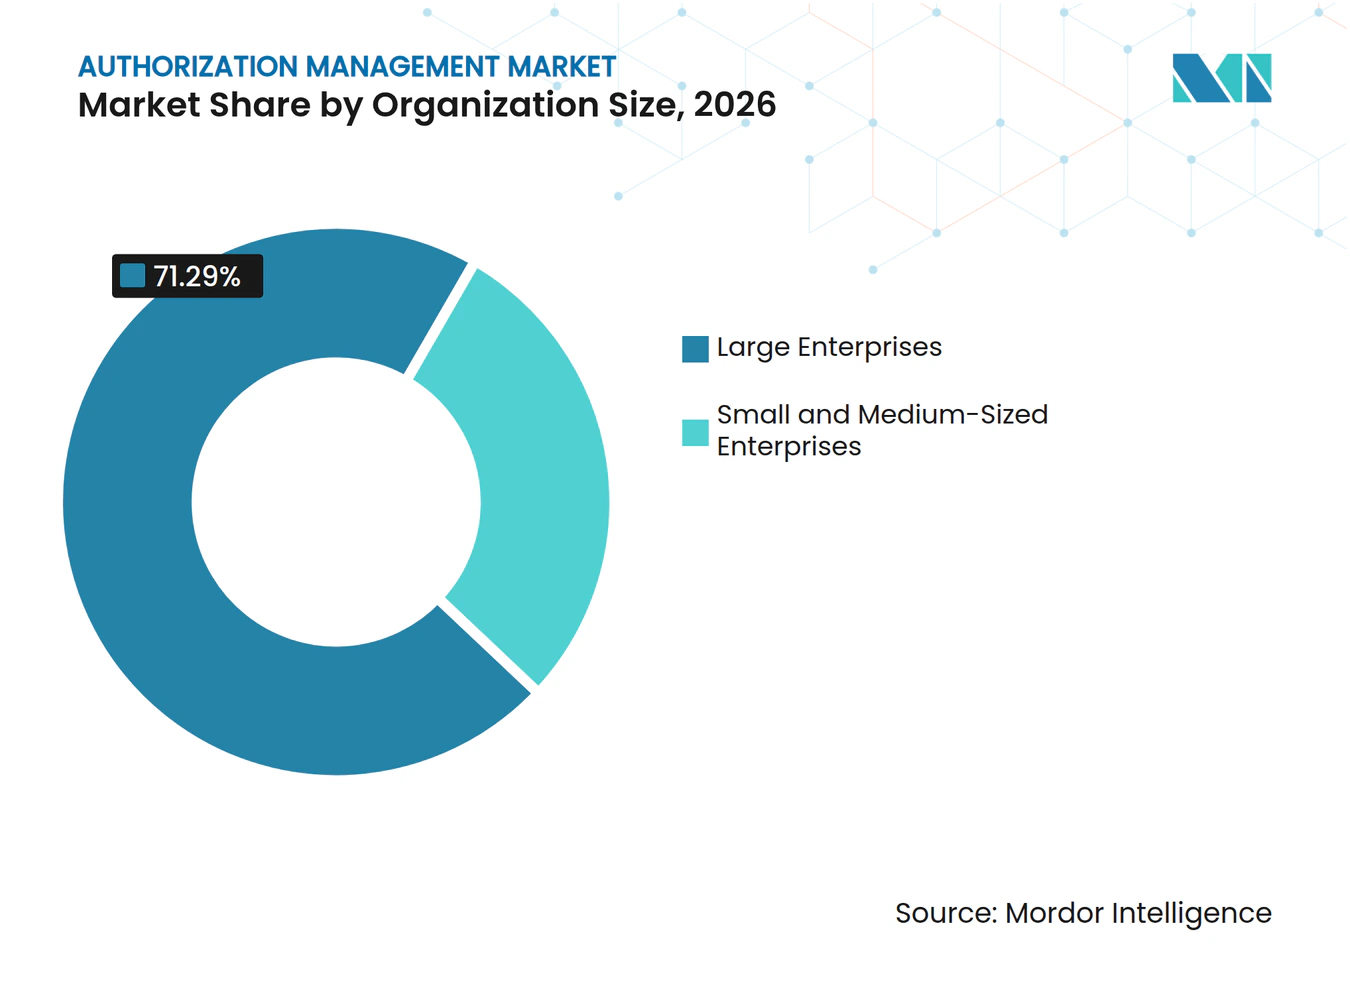
Large Enterprises Hold Revenue While SMEs AccelerateLarge enterprises held 71.29% of the Authorization Management Market share in 2026. Their complex application portfolios, large identity populations, and multiple business units create a clear need for centralized and consistent policy administration. These buyers manage human and machine identities across applications, data stores, cloud accounts, and partner connections, so maintaining separate access rules in every system becomes difficult to sustain. A central policy layer can reduce duplication and produce ongoing audit evidence, rather than requiring repeated manual collection before a review. Large enterprises consequently account for material implementation, and professional services demand when policies must cover detailed roles, attributes, approvals, and exceptions.
Small and medium-sized enterprises are projected to expand at a 30.78% CAGR from 2027 to 2032. Their adoption is supported by cloud-delivered services that offer lower entry costs, faster implementation paths, and less need to operate specialized infrastructure. Compliance expectations can also flow from banks, government buyers, and larger customers to suppliers that handle their systems or data. These organizations often value developer experience and speed to the first enforcement decision more than a broad compliance feature set, which favors low-code editors and prebuilt integrations. This creates a meaningful opening for focused authorization-as-a-service providers to demonstrate quick operational value to small security teams.

By End-Use Industry:
BFSI Leads Revenue While Government Grows FastestBFSI accounted for 29.15% of the Authorization Management Market revenue in 2026. Banks, insurers, and financial service providers must maintain separation of duties and controlled access to sensitive customer, payment, and financial reporting systems. Federal guidance calls on financial institutions to use sound authentication and access practices. These organizations need evidence that permission reviews and access outcomes comply with internal controls and external requirements, and that failed certification cycles do not result in audit findings. The sector’s large share reflects both its extensive regulatory burden and the high value of the data, transactions, and connected systems it protects.
Government and Public Administration is projected to expand at a 29.44% CAGR from 2027 to 2032. In June 2025, the US Army completed an audit-compliant identity-governance integration with its GCSS-Army system. In August 2026, the White House directed federal agencies to expand Login.gov across high-impact public-facing services and conduct digital identity risk assessments. Healthcare and life sciences require differentiated access to protected health information, while IT and telecommunications, industrial manufacturing, retail and e-commerce, and energy and utilities need stronger controls as operational and enterprise systems become more connected. Government growth reflects modernization programs, public service digitization, and the need to demonstrate auditable controls across large user populations.
Geography Analysis
North America and Europe Authorization Management Market
North America accounted for 37.16% of the Authorization Management Market revenue in 2026. The region combines a large base of regulated financial institutions, federal modernization activity, and early use of zero trust and policy-as-code methods by enterprise software and security teams. Federal programs reinforce the value of common identity and access controls across large application portfolios. Canada supports stronger identity management through government digital priorities, while Europe remains the second-largest regional area, led by Germany, the United Kingdom, and France. Across Europe, access-control obligations for essential services and financial entities create demand for systems that can apply policies consistently and document each decision.
APAC Authorization Management Market
Asia-Pacific is projected to grow at a 29.85% CAGR from 2027 to 2032, the fastest regional rate. India’s digital public infrastructure and data-protection framework are increasing access-governance needs in banking, health care, and e-commerce as more services rely on digital identities and shared data. Japan’s data-sharing agenda and cybersecurity strategy support more consistent authorization practices across government and enterprise systems. South Korean financial institutions face tighter data-access governance requirements, while Chinese companies operating under the Multi-Level Protection Scheme 2.0 manage access controls linked to system classifications. The Authorization Management Market serves cloud-native firms in Southeast Asia and industrial groups in Japan and South Korea with substantial on-premises estates, sustaining demand for both cloud-delivered and locally deployed platforms.
MEA and South America Authorization Management Market
South America, the Middle East, and Africa are smaller but growing parts of the Authorization Management Market. Brazil is a leading South American adopter because data-protection rules and open banking require fine-grained API controls, while Argentina and Mexico offer opportunities as multinational companies extend group-wide policies to regional subsidiaries. Saudi Arabia and the UAE are key Middle Eastern markets as national digital programs and financial-sector requirements raise expectations for identity management. South African and Nigerian banks are modernizing access governance practices as digital banking expands, and these regions need managed cloud platforms as well as methods that integrate with older applications.
Competitive Landscape
Market Concentration
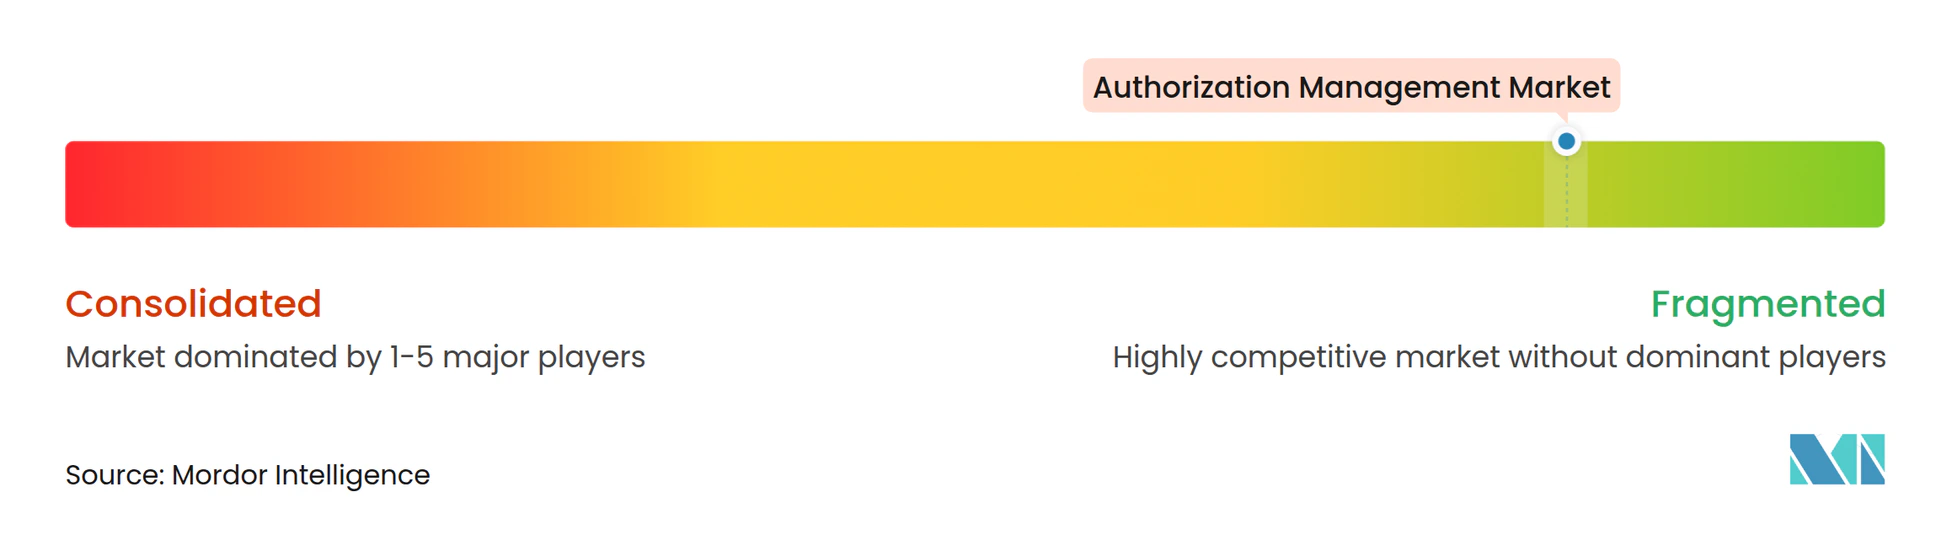
The Authorization Management Market is fragmented across pure-play providers, open-source policy projects, enterprise identity platforms, and zero-standing-privilege specialists. Pure-play providers include AuthZed, Cerbos, Permit.io, and Oso Security, while Open Policy Agent and OpenFGA provide well-known open-source policy foundations for developer teams. Enterprise identity vendors, including Axiomatics, PlainID, NextLabs, and WSO2, compete by adding detailed authorization features to broader identity offerings. Vendors differentiate themselves through developer usability, policy flexibility, deployment options, and their ability to provide audit, compliance, and professional services support. This structure leaves no single supplier with a dominant position and gives customers a wide set of platform and implementation options.
Authorization models are a core point of competition. Providers support role-based, attribute-based, and relationship-based access controls, as well as combinations, allowing customers to match policy methods to different applications. Deployment also matters because some customers need centralized cloud decisions, while others require distributed enforcement close to applications or data stores. AI readiness is gaining importance as organizations define permissions for agent tool calls and retrieval-augmented generation data. Okta introduced platform capabilities in April 2025 to help customers discover and govern AI agents and other non-human identities.
Standards can reduce switching risk and encourage customers to favor interoperable systems. The Netherlands’ 2026 government profile for the OpenID AuthZEN Authorization API exemplifies a decision-exchange approach that supports common implementation patterns.[3] FusionAuth’s November 2025 purchase of Permify combined authentication and fine-grained authorization in a single platform, while Kong introduced native machine-identity capabilities in Kong Konnect for machine-to-machine API access control. Opportunities remain in smaller organizations, AI agent authorization, and operational technology settings where adoption is still developing, particularly for suppliers that pair compliance-ready audit logs with dependable low-latency decisions.
Authorization Management Industry Leaders
-
Axiomatics AB
-
PlainID Ltd.
-
AuthZed, Inc.
-
Permit.io, Inc.
-
Cerbos Limited
- *Disclaimer: Major Players sorted in no particular order
Authorization Management Market Companies Covered in this Report
- Cerbos Limited
- Permit.io, Inc.
- AuthZed, Inc.
- Oso Security, Inc.
- Axiomatics AB
- PlainID Ltd.
- Styra, Inc.
- Aserto, Inc.
- SGNL AI, Inc.
- Warrant Technologies, Inc.
- NextLabs, Inc.
- ObjectSecurity, Inc.
- Velotix Ltd.
- Authomize, Inc.
- Pomerium, Inc.
- Permify, Inc.
- Open Policy Agent Project
- OpenFGA Project
- FusionAuth, Inc.
- WSO2 LLC
Recent Industry Developments in Authorization Management Market
- August 2025: The Netherlands' Programming Council for Generic Digital Infrastructure published the NLgov Profile for OpenID AuthZEN Authorization API 1.0.0 and the Authorization Decision Log 1.0.0 standards, which require Dutch government organizations to log every authorization decision with a unique identifier that links the data subject, access event, and decision basis. The standards provide a standardized, internationally aligned authorization decision exchange protocol, a significant precedent for government-mandated authorization decision auditability.
- August 2026: The White House issued Memorandum M-26-18, directing all federal agencies to adopt Login.gov across High Impact Service Provider public-facing digital services within timelines of 12 to 24 months, and requiring Digital Identity Risk Management assessments aligned with NIST SP 800-63-4. The mandate materially expands procurement requirements for authorization management across US federal civilian agencies.
- November 2025: FusionAuth acquired Permify on November 20, 2025, an open-source, Zanzibar-inspired fine-grained authorization service, creating what the company describes as the first platform to unify authentication and authorization in a single deploy-anywhere architecture. FusionAuth plans to release the integrated product and revised pricing model in 2026, targeting organizations seeking to consolidate identity stacks and reduce third-party SaaS dependencies.
- October 2025: Kong Inc. announced native availability of Kong Identity within Kong Konnect at API Summit 2025, providing machine-to-machine API access control without a third-party identity provider. The capability assigns every automated API client a unique, verifiable identity and enforces precise authentication and authorization at the API gateway layer, extending zero trust control to non-human identities at the infrastructure level.
Global Authorization Management Market Report Scope
The Authorization Management Market comprises software platforms and services that enable organizations to define, manage, enforce, audit, and monitor authorization policies governing access to applications, APIs, data, workloads, machine identities, and digital resources. These solutions support fine-grained access control, policy-as-code frameworks, relationship-based authorization, authorization decision-making, and policy governance across cloud and on-premises environments. The market includes authorization policy engines, policy enforcement solutions, authorization data stores, analytics platforms, consulting, implementation, support, and managed services.
The Authorization Management Market Report is Segmented by Component (Policy Decision Point and Enforcement, Authorization Data and Relationship Store, Analytics, Audit, and Reporting, and Other Components), Deployment Mode (On-Premises, and Cloud), Organization Size (Large Enterprises, and Small and Medium-Sized Enterprises), End-Use Industry (Banking, Financial Services, and Insurance [BFSI], Government and Public Administration, Healthcare and Life Sciences, IT and Telecommunication, Industrial Manufacturing, Retail and E-commerce, Energy and Utilities, and Other End-User Industries), and Geography (North America, South America, Europe, Asia-Pacific, Middle East, and Africa). The Market Forecasts are Provided in Terms of Value (USD).
Segmentation Overview
| Policy Decision Point and Enforcement |
| Authorization Data and Relationship Store |
| Analytics, Audit, and Reporting |
| Other Components |
| On-Premises |
| Cloud |
| Large Enterprises |
| Small and Medium-Sized Enterprises |
| Banking, Financial Services, and Insurance (BFSI) |
| Government and Public Administration |
| Healthcare and Life Sciences |
| IT and Telecommunication |
| Industrial Manufacturing |
| Retail and E-commerce |
| Energy and Utilities |
| Other End-User Industries |
| North America | United States |
| Canada | |
| South America | Brazil |
| Argentina | |
| Mexico | |
| Rest of South America | |
| Europe | Germany |
| United Kingdom | |
| France | |
| Italy | |
| Russia | |
| Rest of Europe | |
| Asia-Pacific | China |
| Japan | |
| India | |
| South Korea | |
| Rest of Asia-Pacific | |
| Middle East | Saudi Arabia |
| United Arab Emirates | |
| Rest of Middle East | |
| Africa | South Africa |
| Nigeria | |
| Rest of Africa |
| By Component | Policy Decision Point and Enforcement | |
| Authorization Data and Relationship Store | ||
| Analytics, Audit, and Reporting | ||
| Other Components | ||
| By Deployment Mode | On-Premises | |
| Cloud | ||
| By Organization Size | Large Enterprises | |
| Small and Medium-Sized Enterprises | ||
| By End-Use Industry | Banking, Financial Services, and Insurance (BFSI) | |
| Government and Public Administration | ||
| Healthcare and Life Sciences | ||
| IT and Telecommunication | ||
| Industrial Manufacturing | ||
| Retail and E-commerce | ||
| Energy and Utilities | ||
| Other End-User Industries | ||
| By Geography | North America | United States |
| Canada | ||
| South America | Brazil | |
| Argentina | ||
| Mexico | ||
| Rest of South America | ||
| Europe | Germany | |
| United Kingdom | ||
| France | ||
| Italy | ||
| Russia | ||
| Rest of Europe | ||
| Asia-Pacific | China | |
| Japan | ||
| India | ||
| South Korea | ||
| Rest of Asia-Pacific | ||
| Middle East | Saudi Arabia | |
| United Arab Emirates | ||
| Rest of Middle East | ||
| Africa | South Africa | |
| Nigeria | ||
| Rest of Africa | ||
Key Questions Answered in the Report
What is the size of the Authorization Management Market?
The Authorization Management Market is projected to expand from USD 2.18 billion in 2026 to USD 9.85 billion by 2032, at a 28.75% CAGR from 2027 to 2032.
What is driving adoption of authorization management platforms?
The Authorization Management Market is supported by zero trust programs, rising machine identities, cloud permission complexity, and the need for auditable least-privilege controls.
Which component has the largest share of authorization management revenue?
Policy Decision Point and Enforcement held 58.16% of component revenue in 2026 because it supports runtime access decisions and audit records.
Which deployment approach is growing fastest?
Cloud deployment is projected to grow at a 30.41% CAGR through 2032 as organizations adopt managed, multi-cloud policy services.
Which end-use sector leads authorization management spending?
BFSI held 29.15% of revenue in 2026 because financial institutions need strong access controls, segregation of duties, and audit evidence.
Which region is expected to grow fastest?
Asia-Pacific is projected to grow at a 29.85% CAGR through 2032, supported by digital government programs and financial-sector access requirements.