
Managed DNSSEC Services Market Size and Share
Market Overview
| Study Period | 2021 - 2032 |
|---|---|
| Market Size (2027) | USD 0.56 Billion |
| Market Size (2032) | USD 1.07 Billion |
| Growth Rate (2027 - 2032) | 17.23 % |
| Fastest Growing Market | Asia-Pacific |
| Largest Market | North America |
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image © Mordor Intelligence. Reuse requires attribution under CC BY 4.0. | |
Managed DNSSEC Services Market Analysis by Mordor Intelligence
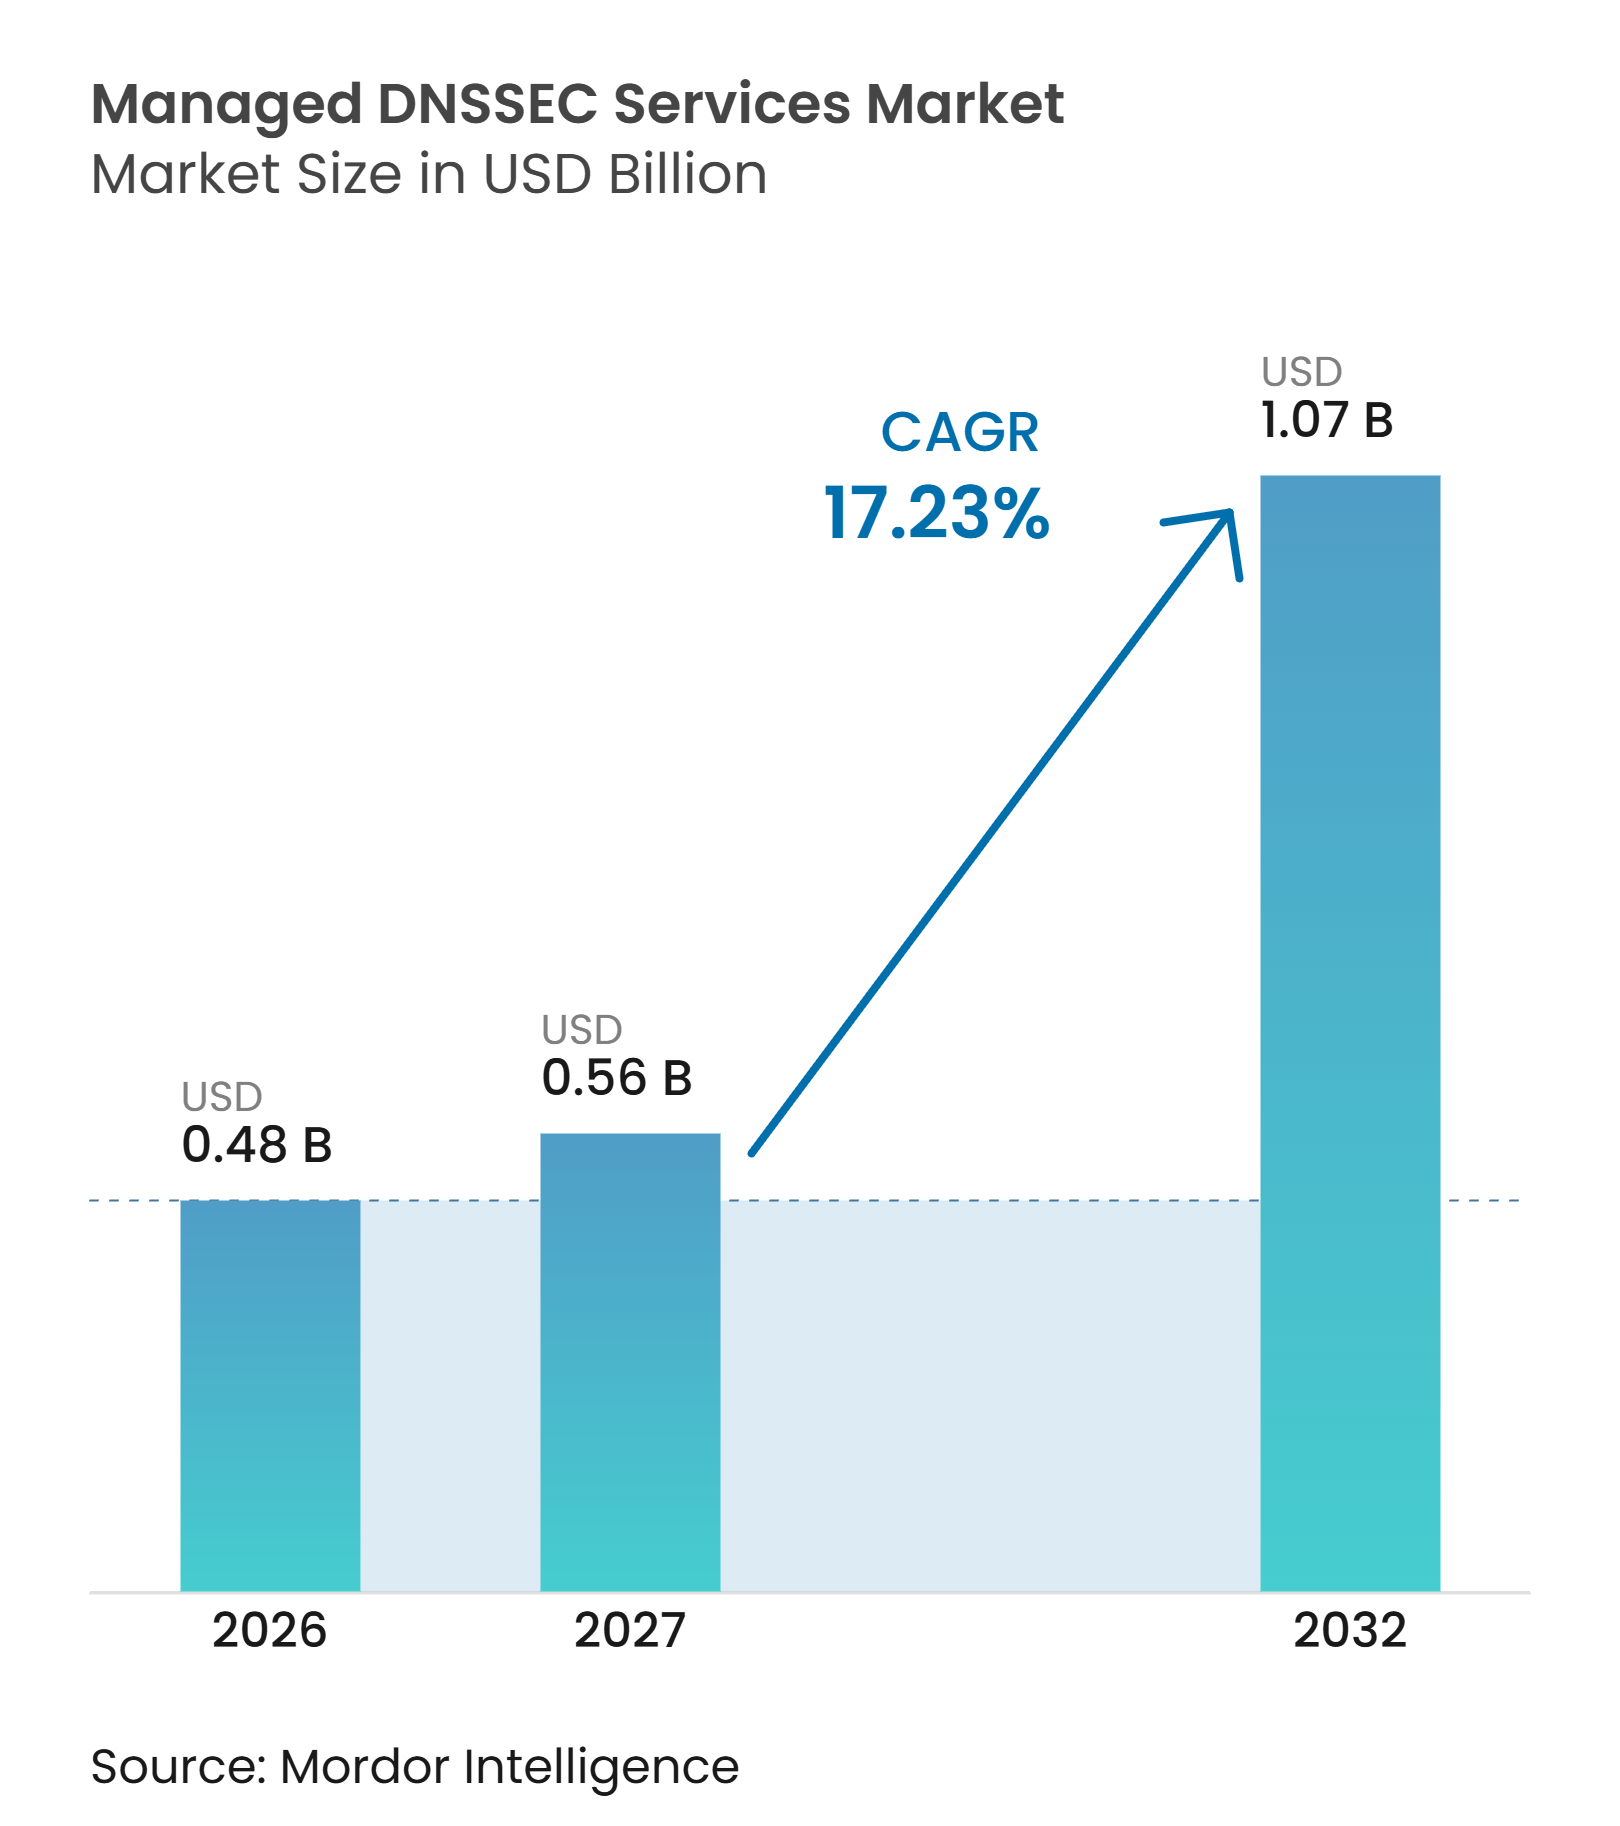
The managed DNSSEC services market size is projected to expand from USD 0.48 billion in 2026 and USD 0.56 billion in 2027 to USD 1.07 billion by 2032, registering a CAGR of 17.23% between 2027 to 2032. Demand reflects an unresolved authentication gap, because global DNSSEC validation reached 35.4% in Q3 2025, compared with 49.4% across EU member states, leaving many resolution chains without cryptographic protection. Managed signing, key management, and monitoring reduce the operational burden that can make in-house key rollover difficult and can disrupt a domain when timing mistakes reach caching resolvers. Cloud-native deployment is also increasing the number of zones, delegation records, and validation paths that teams must manage across different providers, with limited scope to defer professional support as applications and infrastructure change. Providers in the managed DNSSEC services market are responding by combining DNSSEC with broader DNS visibility, compliance automation, certificate lifecycle capabilities, and structured migration support. Sovereign DNS and post-quantum migration are widening the buying case beyond network teams to include security, privacy, legal, and continuity functions.
Key Report Takeaways
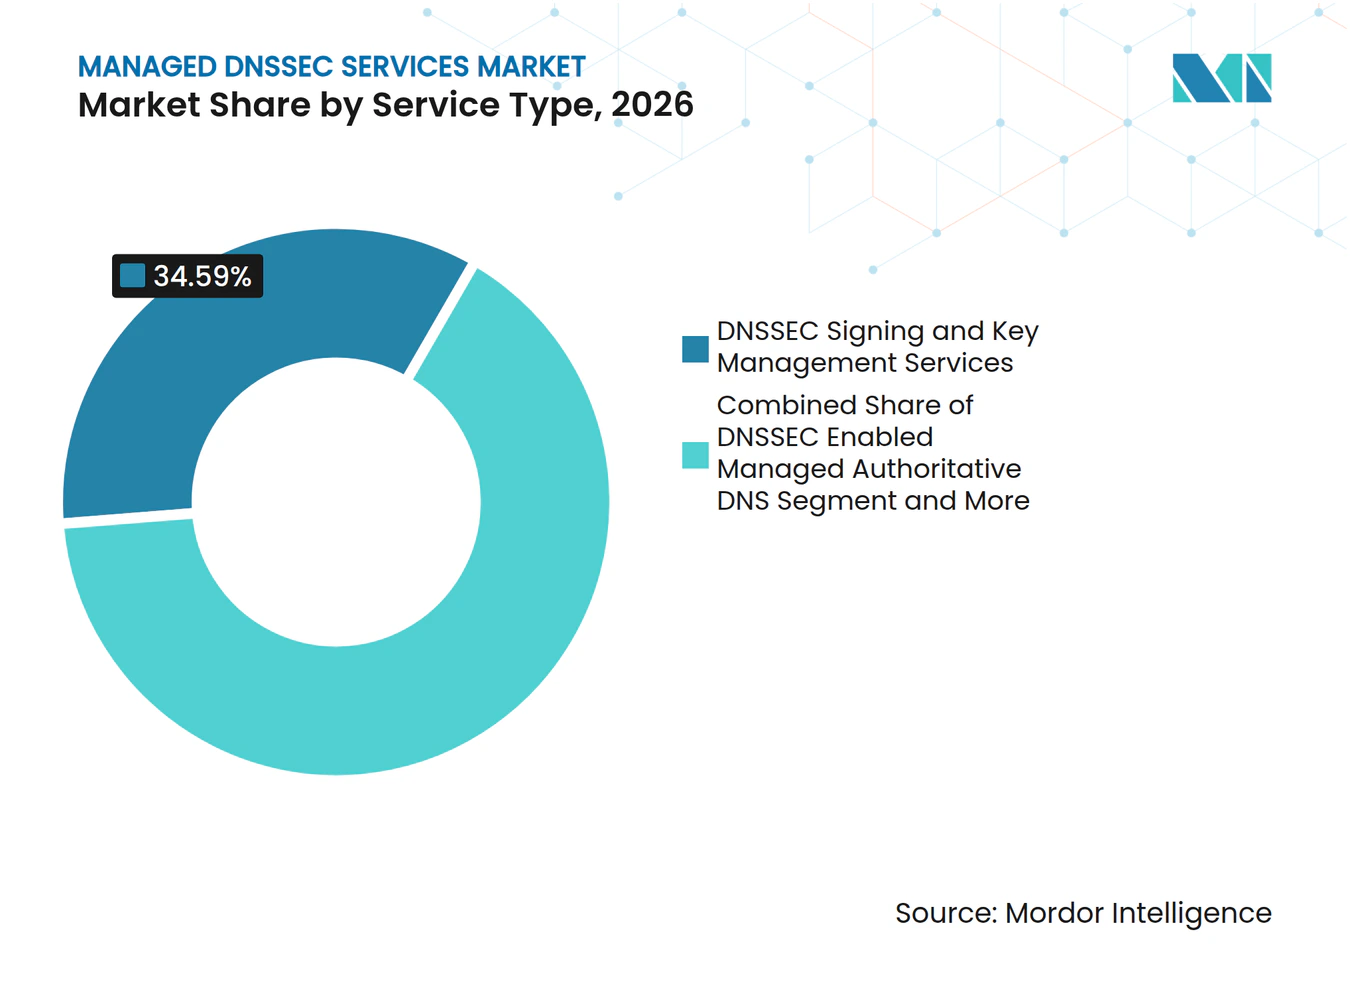
- By service type, DNSSEC Signing and Key Management Services held 34.59% of revenue in 2026, while Secondary DNSSEC and Multi-Provider Resilience Services is projected to expand at an 18.49% CAGR through 2032.
- By enterprise size, large enterprises accounted for 76.99% of revenue in 2026, while SMEs are projected to expand at an 18.79% CAGR through 2032.
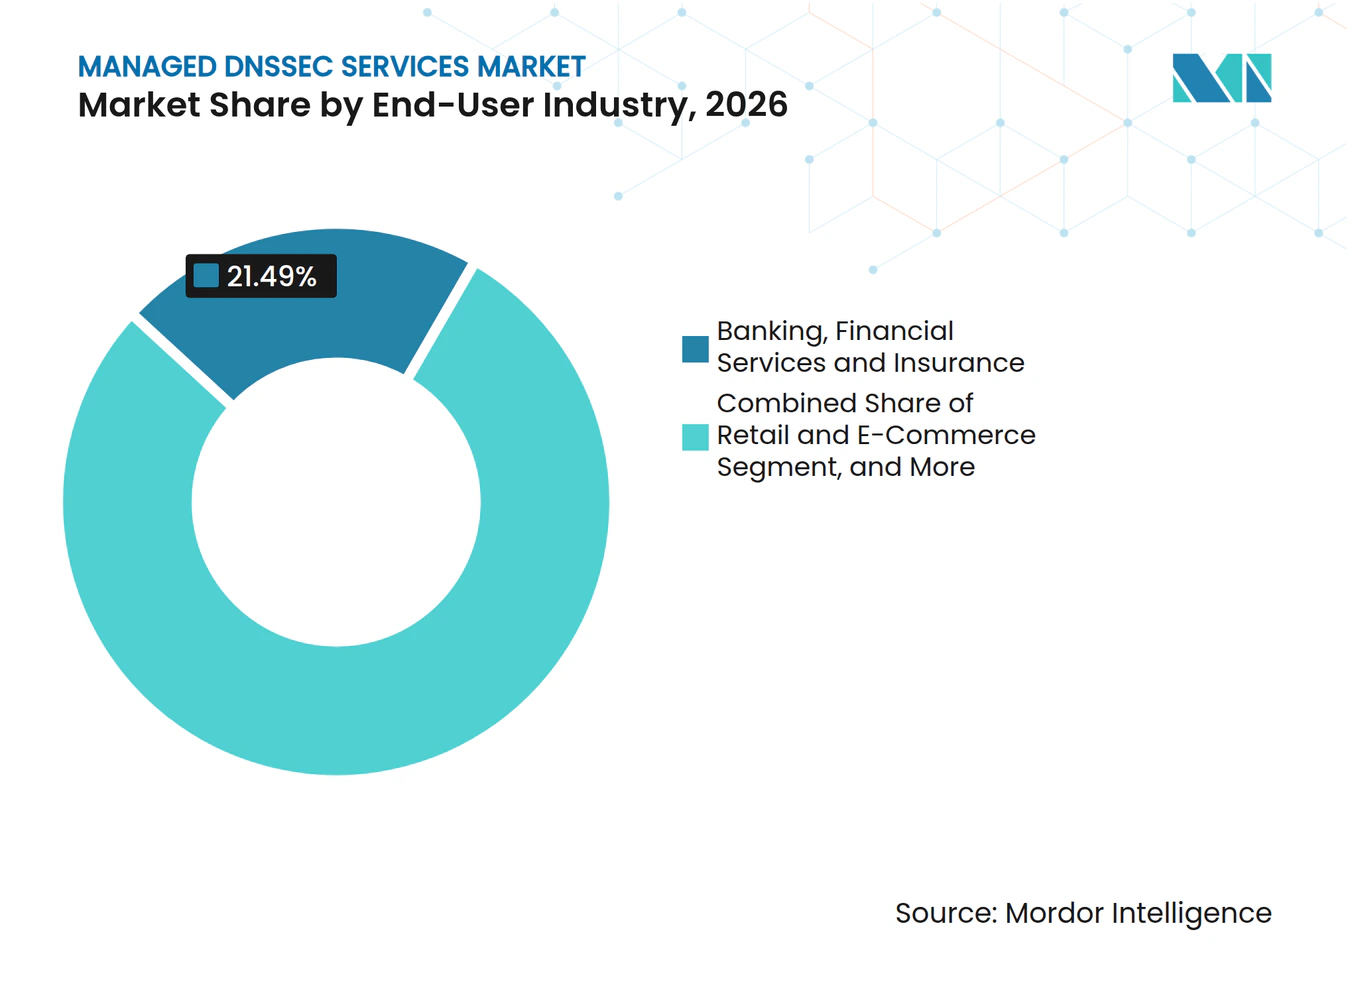
- By end-user industry, BFSI held 21.49% of revenue in 2026, while government and public sector is projected to expand at an 18.64% CAGR through 2032.
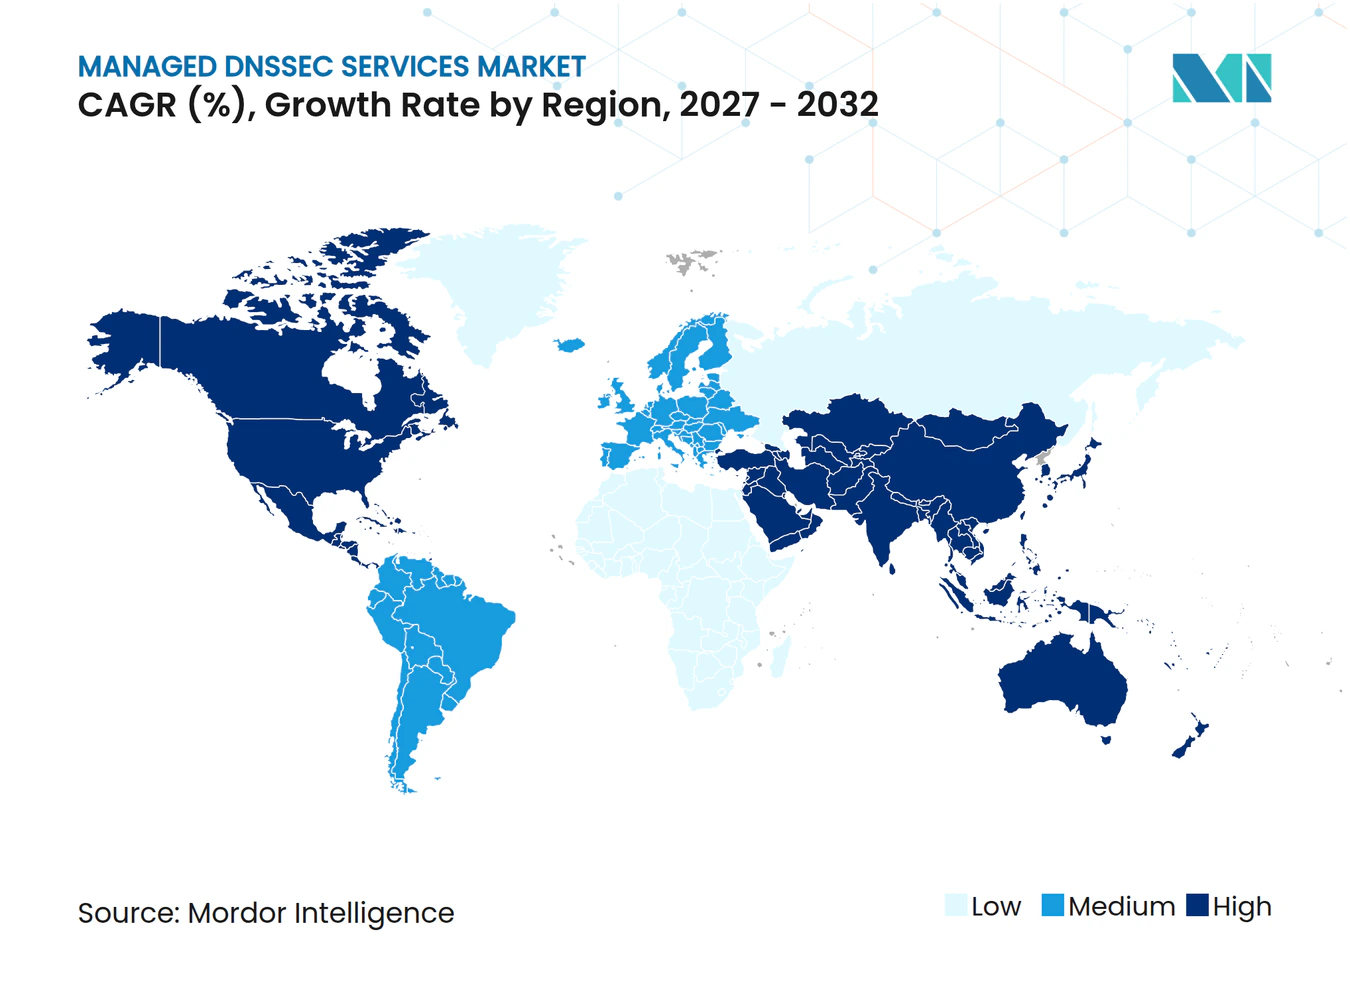
- By geography, North America held 41.51% of managed DNSSEC services market share in 2026, while Asia-Pacific is projected to expand at an 18.72% CAGR through 2032.
Note: Market numbers in this report are based on Mordor Intelligence's proprietary estimation framework, which combines nine months of actuals with Q4 projections for base year 2026.
Market Trends and Insights
Drivers Impact Analysis of Managed DNSSEC Services Market*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Rising DNS-Based Cyberattacks and Demand for Authenticity | +5.2% | Global | Short term (≤ 2 years) |
| Cloud-Native and Multi-Cloud Application Expansion | +3.6% | Global, with Asia-Pacific and North America leading | Medium term (2-4 years) |
| Increasing Need for High-Availability Internet Services | +2.9% | North America and Europe core, Asia-Pacific growing | Medium term (2-4 years) |
| Growth of Edge Computing, CDN and Multi-CDN Architectures | +2.2% | North America and Asia-Pacific core, spillover to Middle East and Africa | Long term (≥ 4 years) |
| Expansion of IoT Endpoints and Dynamic DNS Dependencies | +1.8% | Global, with Asia-Pacific and North America leading | Medium term (2-4 years) |
| Data Residency and Digital Sovereignty Requirements | +1.5% | Europe and Asia-Pacific, with early gains in Middle East | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
Rising DNS-Based Cyberattacks and Demand for Authenticity
DNS threat activity is strengthening the security case for the managed DNSSEC services market. EfficientIP reported 13.85 billion DNS threat signals in H1 2026, up 24% from H2 2025, based on more than 150 billion daily DNS transactions. Malware became the leading DNS-based threat category during the period, which increases the importance of protecting a core service that attackers can use for infrastructure discovery and redirection. Domain-generation activity rose before the subsequent increase in newly observed domains and malware activity, giving security teams a reason to monitor trusted DNS response chains earlier in an attack cycle. EfficientIP also reported that 95% of surveyed security decision-makers had experienced at least 1 DNS-related incident in the prior 12 months, with an average attack cost of USD 1.1 million for mid-sized and large organizations.[1] The managed DNSSEC services market therefore benefits when DNS controls move from a network operations concern to a defined security spending priority.
Cloud-Native and Multi-Cloud Application Expansion
Cloud-native deployments create more zones, DS record handoffs, and resolver validation paths for enterprise teams to maintain. The burden becomes heavier when teams use the native DNS tools of several cloud providers, because configuration standards, access controls, and ownership can differ by environment. Infoblox reported that its Universal DDI platform added unified management for external DNS across Akamai and Cloudflare from 1 control plane. That capability reflects a broader need for consistent control across varied DNS environments and for an auditable operating model. EfficientIP has similarly described centralized, overlay-based management as a durable approach for hybrid and multicloud DNS operations. Providers in the managed DNSSEC services market that coordinate signing across several cloud environments are better placed than providers that only sign zones hosted by a single platform.
Increasing Need for High-Availability Internet Services
Edge computing and CDN deployments have made DNS a latency-sensitive routing layer. The shift creates a need for signing that can keep pace with endpoints deployed across many locations and with frequent delegation changes. Cloudflare added NSEC3 support for enterprise DNSSEC zones in June 2025, supporting live-signed and pre-signed secondary zones while limiting zone-enumeration exposure.[2] PowerDNS implemented automated authenticated DNSSEC bootstrapping under RFC 9615 in May 2026, reducing manual DS record provisioning for signed zones. In a multi-CDN setting, unsigned or invalid responses can undermine routing decisions that depend on geography, load, and application conditions, and may redirect traffic toward an unintended endpoint before traditional application controls react. Providers in the managed DNSSEC services market that combine anycast delivery, automation, and controlled key ceremonies can shorten deployment cycles for organizations operating distributed edge footprints.
Growth of Edge Computing, CDN, and Multi-CDN Architectures
Edge computing and CDN deployments have made DNS a latency-sensitive routing layer. The shift creates a need for signing that can keep pace with endpoints deployed across many locations. Cloudflare added NSEC3 support for enterprise DNSSEC zones in June 2025, supporting live-signed and pre-signed secondary zones while limiting zone-enumeration exposure. PowerDNS implemented automated authenticated DNSSEC bootstrapping under RFC 9615 in May 2026, reducing manual DS record provisioning for signed zones.[3] In a multi-CDN setting, unsigned or invalid responses can undermine routing decisions that depend on geography, load, and application conditions. Managed DNSSEC providers that combine anycast delivery, automation, and controlled key ceremonies can shorten deployment cycles for organizations operating distributed edge footprints.
Restraints Impact Analysis of Managed DNSSEC Services Market*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| DNSSEC Key-Rollover and Multi-Signer Operational Complexity | -2.1% | Global | Medium term (2-4 years) |
| Legacy DNS Migration and Change-Control Risk | -1.6% | North America and Europe | Medium term (2-4 years) |
| Managed DNS Price Commoditization and Free-Service Substitution | -1.2% | Global, sharpest in SME and mid-market segments | Short term (≤ 2 years) |
| Single-Provider Concentration and SaaS Outage Exposure | -0.9% | Global | Long term (≥ 4 years) |
| Source: Mordor Intelligence | |||
DNSSEC Key-Rollover and Multi-Signer Operational Complexity
DNSSEC key management requires coordinated timing across Zone Signing Key and Key Signing Key rollover stages. An error in TTL sequencing can make a zone unavailable to validating resolvers, even when other parts of the DNS environment continue to operate and the underlying application remains available. The IETF DNSOP working group stated in July 2025 that organizations using automated DS maintenance should verify consistency across authoritative name servers before making updates. That requirement adds work for organizations with many zones, registrars, and providers, especially where responsibilities are split among several teams. PowerDNS automated initial DNSSEC bootstrapping through RFC 9615 in May 2026, but KSK rollover and algorithm migration still require careful operational management. Providers in the managed DNSSEC services market can differentiate through rollover monitoring, TTL tracking, and adoption measurement, although those capabilities also raise delivery and development costs.
DNSSEC key management requires coordinated timing across Zone Signing Key and Key Signing Key rollover stages. An error in TTL sequencing can make a zone unavailable to validating resolvers. The IETF DNSOP working group stated in July 2025 that organizations using automated DS maintenance should verify consistency across authoritative name servers before making updates. That requirement adds work for organizations with many zones and providers. PowerDNS automated initial DNSSEC bootstrapping through RFC 9615 in May 2026, but KSK rollover and algorithm migration still require careful operational management. Service providers can differentiate through rollover monitoring, TTL tracking, and adoption measurement, although those capabilities also raise delivery and development costs.
Legacy DNS Migration and Change-Control Risk
Organizations operating legacy BIND or Windows DNS environments can face difficult migration processes. Zone transfer and DS delegation require coordinated changes among registrars, parent zones, and secondary providers, often within strict change-control windows. A broken chain of trust can return SERVFAIL to validating resolvers, creating direct operational risk for e-commerce and financial domains and requiring a carefully sequenced rollback plan. BlueCat released Integrity X 25.1 in September 2025 with DNSSEC, FIPS 140-2 Level 3 HSM support, and migration validation capabilities. The product direction shows that migration assurance is commercially important alongside signing capability. The managed DNSSEC services market remains constrained where organizations lack specialist DNS resources and providers do not offer phased, well-supported migration routes.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Managed DNSSEC Services Market Segment Analysis
By Service Type:
Key Management Supports Revenue While Resilience Services Lead ExpansionDNSSEC Signing and Key Management Services held 34.59% of revenue in 2026. It provides the base capability needed before a zone can be validated, monitored, or used in a multi-provider structure. Organizations use managed signing when they need support for key generation, storage, rollover, and chain-of-trust maintenance across several domains, including domains with different registrars or secondary providers. This work can be difficult to perform internally when operations teams coordinate with registrars, parent zones, and secondary providers, as key timing and delegation records must remain aligned. DNSSEC-Enabled Managed Authoritative DNS appeals to buyers that prefer 1 provider for zone hosting and signing, although that choice can create provider concentration risk.
Secondary DNSSEC and Multi-Provider Resilience Services is projected to expand at an 18.49% CAGR through 2032. This part of the managed DNSSEC services market is supported by the move toward active-active DNS and multi-CDN deployments, where organizations need continuous authentication during infrastructure changes. Multi-signer arrangements allow providers to operate their own keys instead of sharing a single private signing key, which can be inconsistent with enterprise risk controls. Akamai’s July 2025 support for multi-signer DNSSEC gives enterprise users a practical route to this design. Monitoring, validation, compliance, and migration support are companion purchases for signed-zone operators that need evidence of signing health and a safe transition from BIND or Windows DNS.



By Enterprise Size:
Large Enterprises Lead While SMEs Expand Through Cloud DeliveryLarge enterprises held 76.99% of revenue in 2026. Their leading position reflects greater exposure to sector-specific requirements and their ability to fund professional services, hardware security modules, and dedicated DNS expertise. Large organizations also manage more public domains and complex cloud environments, increasing the value of centralized signing, monitoring, and documented ownership. They commonly need evidence for security reviews, supplier assessments, incident response, and internal control processes that do not apply in the same way to smaller organizations. These conditions make them the main revenue source for providers in the managed DNSSEC services market and support demand for enterprise service levels.
SMEs are projected to expand at an 18.79% CAGR through 2032. Cloud-delivered platforms reduce the need for dedicated HSMs and specialized DNS engineering headcount, which had historically limited adoption at smaller scale. Smaller organizations in financial technology, digital health, and government contracting can face DNSSEC requirements through customer vendor-security programs. Infoblox introduced token-based licensing for its security portfolio in September 2025, using a consumption-aligned model that can lower the initial commitment for variable workloads. Standard paid plans with DNSSEC from ClouDNS, DNSimple, and easyDNS broaden access, but they can place pressure on margins in the SME portion of the managed DNSSEC services market.
By End-User Industry:
Financial Services Lead While Public Sector Adoption AcceleratesBFSI accounted for 21.49% of revenue in 2026. The segment’s role reflects the importance of authenticated internet domains for institutions that handle customer accounts, high-value transactions, digital service access, and regulated customer communications. fTLD Registry requires DNSSEC for all .bank and .insurance registrants, making it a condition for qualifying domains. IT and telecommunications providers buy managed DNSSEC services for their own networks and may include them in offerings for enterprise clients, which extends their use beyond direct internal requirements. Healthcare and life sciences buyers are also using DNSSEC as cloud-based patient portals and distributed application endpoints expand.
Government and public sector is projected to expand at an 18.64% CAGR through 2032. National requirements can extend DNSSEC deployment across public digital services, rather than leave implementation to individual organizations or departments. The Czech Ministry of Industry and Trade reported in June 2025 that the gov.cz domain had been correctly signed under the supervision of the National Cyber and Information Security Agency, following the state administration DNSSEC program. Retail, e-commerce, media, and entertainment have lower adoption shares, yet DNS-related brand abuse strengthens the case to protect customer-facing domains and reduce avoidable service risk. These patterns broaden the end-user base for the managed DNSSEC services market.

Geography Analysis
North America represented 41.51% of revenue in 2026. The region benefits from a large concentration of commercial DNS providers, established enterprise buyers, and mandate-driven procurement. The U.S. Executive Order issued in January 2025 directed Federal Civilian Executive Branch agencies to enable encrypted DNS within 180 days and required encrypted DNS in resolver procurement. CISA’s Protective DNS program has created a reference model that state, local, and tribal bodies can use for their own procurement requirements. Canadian and Mexican suppliers that serve U.S. government-linked customers can also face similar security assessments, extending demand beyond direct federal purchases.
Asia-Pacific is projected to expand at an 18.72% CAGR through 2032. The managed DNSSEC services market size in the region benefits from 5G investment, government digitization, and tighter requirements for critical information infrastructure. India’s public digital programs and expanding cloud-based financial services create a large DNS authentication surface that requires reliable protection for high-volume transactions and widely distributed digital-service users. South Korea’s Network Act and Personal Information Protection Act amendments that took effect in 2025 raised cybersecurity expectations for telecommunications, e-commerce, and healthcare operators. Providers that establish regional key-management capacity and anycast-delivered signing ahead of formal adoption requirements can improve their position.
Europe’s regulatory influence combines the NIS2 Directive, DORA, and the EU Data Act, while DNS4EU signals that European institutions consider DNS control part of digital sovereignty. European data residency requirements place more value on local key custody in the managed DNSSEC services market, particularly where organizations need to demonstrate operational control. The Middle East has earlier-stage demand, supported by Saudi Arabia’s Vision 2030, UAE telecommunications liberalization, and critical-infrastructure protection frameworks. Africa and South America remain developing opportunities, with South Africa, Nigeria, Egypt, and Brazil serving as demand centers as cloud infrastructure and public digital services expand.
Competitive Landscape
Market Concentration
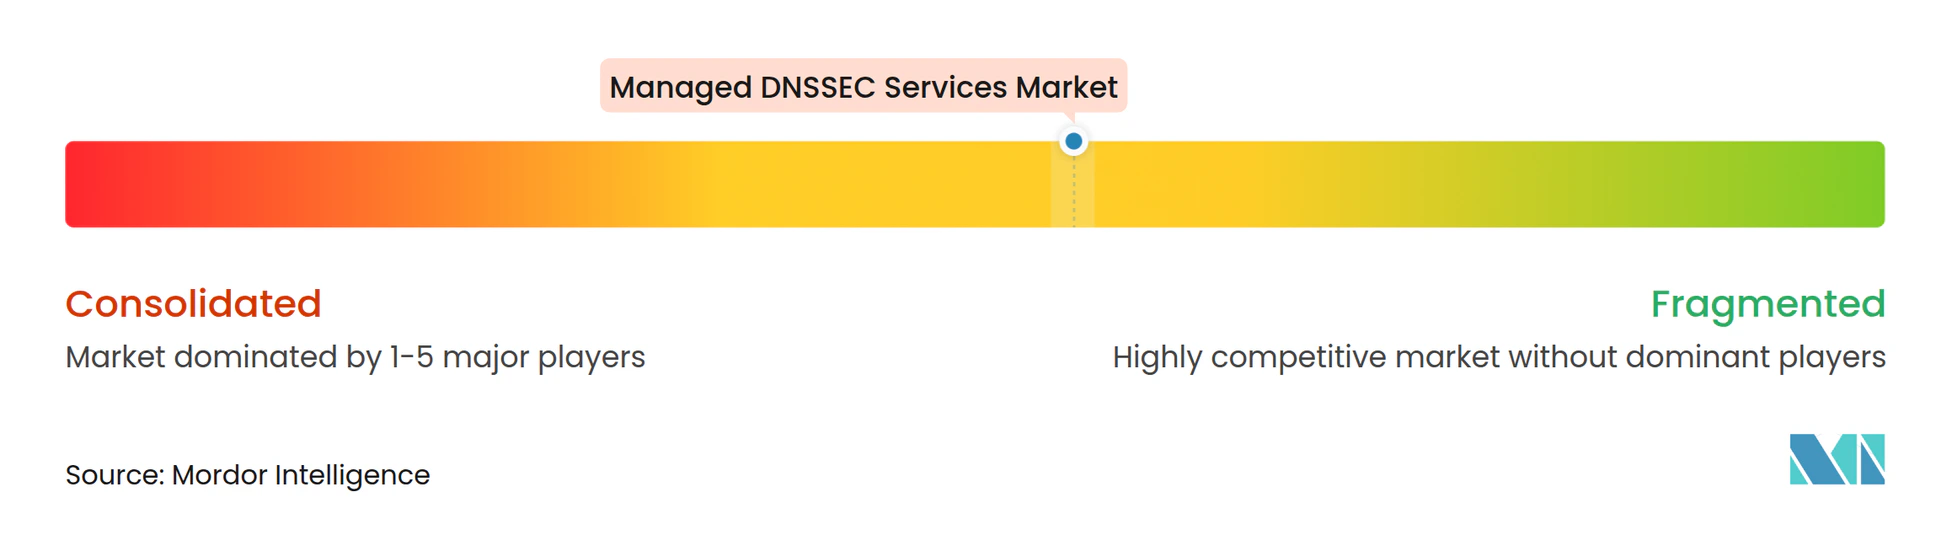
The managed DNSSEC services market includes hyperscale DNS platforms, such as Cloudflare, Akamai, and Verisign, alongside enterprise DDI vendors, including Infoblox, EfficientIP, and BlueCat. Hyperscale providers compete through global anycast infrastructure and large resolver or authoritative DNS footprints. DDI providers position DNSSEC within broader DNS, DHCP, and IP address management offerings that support daily network operations. Competition is moving toward integrated platforms that combine signing, monitoring, compliance, migration support, and multicloud visibility. This approach makes DNSSEC part of a wider security and operations purchase rather than a standalone service.
Cloudflare enabled ML-DSA-44 post-quantum DNSSEC validation on the 1.1.1.1 resolver in September 2026. Verisign published its Merkle Tree Ladder mode strategy for post-quantum DNSSEC in October 2025, using a hash-based SLH-DSA approach intended to reduce transport burden. These moves place post-quantum readiness among the areas where infrastructure providers can distinguish their offerings as customers assess longer-term algorithm migration. They also show that the next upgrade cycle includes architectural choices that extend beyond ordinary zone signing. The managed DNSSEC services market rewards providers that can demonstrate these capabilities in production operations.
Akamai launched DNS Posture Management in June 2025 for multicloud DNS visibility and automated assessment against frameworks including NIST, PCI DSS, and HIPAA. Infoblox launched Infoblox IQ in June 2026, applying agentic AI to DNS query data, DHCP leases, IP assignments, and security events. Verisign completed a root-zone ZSK signing HSM transition in 2025, with an 80-day post-publication window for the prior key as a rollback safeguard. The managed DNSSEC services market still has openings in SME monitoring, sovereign services, IoT device namespaces, and migration support for regulated buyers that need credible key-management practices.
Managed DNSSEC Services Industry Leaders
-
Cloudflare, Inc.
-
Akamai Technologies, Inc.
-
Verisign, Inc.
-
Vercara, LLC
-
Tiggee LLC
- *Disclaimer: Major Players sorted in no particular order
Managed DNSSEC Services Market Companies Covered in this Report
- Cloudflare, Inc.
- Akamai Technologies, Inc.
- Verisign, Inc.
- Vercara, LLC
- Tiggee LLC
- Infoblox Inc.
- BlueCat Networks Inc.
- EfficientIP S.A.S.
- ClouDNS Ltd.
- DNSimple Corporation
- Vitalwerks Internet Solutions, LLC
- easyDNS Technologies Inc.
- EuroDNS S.A.
- Netnod AB
- PowerDNS.COM B.V.
- Constellix LLC
- Total Uptime Technologies, LLC
- Netriplex LLC
- Rage4 DNS Ltd.
- 1984 ehf
Recent Industry Developments in Managed DNSSEC Services Market
- October 2026: EfficientIP released its H1 2026 DNS Threat Intelligence Report, disclosing that total DNS threat signals rose 24% from H2 2025 to reach 13.85 billion hits, with malware daily activity roughly quadrupling between January and April 2026 and overtaking phishing as the leading DNS-based threat category for the first time. The report, drawn from over 150 billion daily DNS transactions, materially shifts enterprise DNS threat prioritization toward authenticated resolution chains, reinforcing demand for managed DNSSEC signing and validation services.
- September 2026: Cloudflare enabled ML-DSA-44 post-quantum DNSSEC validation on its 1.1.1.1 resolver, becoming the first major public resolver operator to implement a NIST-standardized post-quantum signature algorithm, DNSSEC algorithm 18, at production scale. The company plans to follow with ML-DSA-44 signing support for Cloudflare Authoritative DNS and corresponding DS record support for Cloudflare Registrar, to be made available at no additional charge to all customers.
- July 2026: Verisign announced the delegation of .web into the global DNS root zone with Verisign as the designated registry operator, expanding the company’s DNSSEC zone-signing responsibility beyond .com and .net to include a new generic top-level domain.
- June 2026: Infoblox launched Infoblox IQ, an agentic AI operations layer built on DNS query data, DHCP leases, IP address assignments, and security events flowing through the Infoblox Platform. Infoblox IQ for Threat Defense reached general availability by the end of June 2026, while DDI and assistant modules entered early access.
Global Managed DNSSEC Services Market Report Scope
The Managed DNSSEC Services Market refers to the industry focused on the outsourcing, deployment, monitoring, maintenance, and lifecycle management of Domain Name System Security Extensions (DNSSEC) by specialized managed service providers to ensure the authenticity, integrity, and trustworthiness of DNS transactions.
The Managed DNSSEC Services Report is Segmented by Service Type (DNSSEC Signing and Key Management Services, Secondary DNSSEC and Multi-Provider Resilience Services, DNSSEC Monitoring, Validation and Compliance Services, DNSSEC-Enabled Managed Authoritative DNS, and DNSSEC Professional Services and Migration Support), Enterprise Size (Large Enterprises and Small and Medium Enterprises), End-User Industry (Banking, Financial Services and Insurance, IT and Telecommunications, Media and Entertainment, Retail and E-commerce, Healthcare and Life Sciences, Government and Public Sector, and Other End-User Industries), and Geography (North America, Europe, Asia-Pacific, Middle East, Africa, and South America). The Market Forecasts are Provided in Terms of Value (USD).
Segmentation Overview
| DNSSEC Signing and Key Management Services |
| DNSSEC Monitoring, Validation and Compliance Services |
| Secondary DNSSEC and Multi-Provider Resilience Services |
| DNSSEC-Enabled Managed Authoritative DNS |
| DNSSEC Professional Services and Migration Support |
| Large Enterprises |
| Small and Medium Enterprises |
| Banking, Financial Services and Insurance |
| IT and Telecommunications |
| Media and Entertainment |
| Retail and E-Commerce |
| Healthcare and Life Sciences |
| Government and Public Sector |
| Other End-User Industries |
| North America | United States |
| Canada | |
| Mexico | |
| Europe | Germany |
| United Kingdom | |
| France | |
| Italy | |
| Spain | |
| Rest of Europe | |
| Asia-Pacific | China |
| Japan | |
| India | |
| South Korea | |
| Australia | |
| Rest of Asia-Pacific | |
| Middle East | Saudi Arabia |
| United Arab Emirates | |
| Turkey | |
| Israel | |
| Rest of Middle East | |
| Africa | South Africa |
| Egypt | |
| Nigeria | |
| Rest of Africa | |
| South America | Brazil |
| Argentina | |
| Rest of South America |
| By Service Type | DNSSEC Signing and Key Management Services | |
| DNSSEC Monitoring, Validation and Compliance Services | ||
| Secondary DNSSEC and Multi-Provider Resilience Services | ||
| DNSSEC-Enabled Managed Authoritative DNS | ||
| DNSSEC Professional Services and Migration Support | ||
| By Enterprise Size | Large Enterprises | |
| Small and Medium Enterprises | ||
| By End-User Industry | Banking, Financial Services and Insurance | |
| IT and Telecommunications | ||
| Media and Entertainment | ||
| Retail and E-Commerce | ||
| Healthcare and Life Sciences | ||
| Government and Public Sector | ||
| Other End-User Industries | ||
| By Geography | North America | United States |
| Canada | ||
| Mexico | ||
| Europe | Germany | |
| United Kingdom | ||
| France | ||
| Italy | ||
| Spain | ||
| Rest of Europe | ||
| Asia-Pacific | China | |
| Japan | ||
| India | ||
| South Korea | ||
| Australia | ||
| Rest of Asia-Pacific | ||
| Middle East | Saudi Arabia | |
| United Arab Emirates | ||
| Turkey | ||
| Israel | ||
| Rest of Middle East | ||
| Africa | South Africa | |
| Egypt | ||
| Nigeria | ||
| Rest of Africa | ||
| South America | Brazil | |
| Argentina | ||
| Rest of South America | ||
Key Questions Answered in the Report
What is the managed DNSSEC services market size?
The managed DNSSEC services market is projected to increase from USD 0.48 billion in 2026 to USD 1.07 billion by 2032, at a 17.23% CAGR from 2027 to 2032. The estimate also places the 2027 value at USD 0.56 billion.
Which managed DNSSEC service has the largest share?
DNSSEC Signing and Key Management Services held the largest share at 34.59% in 2026 because signing is required before validation, monitoring, or multi-provider resilience can be used. These activities keep the DNSSEC chain of trust active after a zone is deployed.
Which managed DNSSEC service is expanding fastest?
Secondary DNSSEC and Multi-Provider Resilience Services is projected to expand at an 18.49% CAGR through 2032 as enterprises move toward active-active and multi-CDN architectures. Multi-signer processes can support these architectures without a single shared private key.
Why are enterprises adopting managed DNSSEC services?
Organizations adopt these services to manage signing, key rollover, monitoring, and compliance without maintaining the specialist capability needed for in-house DNSSEC operations. The managed DNSSEC services market also supports migration from legacy DNS settings and coordination across multiple cloud providers.
Which end-user sector leads managed DNSSEC spending?
BFSI held 21.49% of revenue in 2026, supported by domain-security requirements for regulated financial institutions and .bank or .insurance registrants. Government and public sector is the faster-expanding segment at an 18.64% CAGR through 2032.
Which region is expanding fastest for managed DNSSEC services?
Asia-Pacific is projected to expand at an 18.72% CAGR through 2032, supported by 5G investment, government digital programs, and critical infrastructure security requirements. North America remained the largest regional revenue contributor, representing 41.51% in 2026.